Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Zack Whittaker

@zackwhittaker@mastodon.social
mastodon 4.8.0-nightly.2026-10-06
  • Open on mastodon.social

Security editor, TechCrunch
Email: zack.whittaker@techcrunch.com
Signal: zackwhittaker.1337
New York, NY

20249 Followers
458 Following
50 Posts
Joined October 28, 2022
Newsletter:
https://this.weekinsecurity.com
TechCrunch:
https://techcrunch.com/author/zack-whittaker
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 4w ago
Boosted by @trending@homestead.social
Watching this Apple event tout how iPhones will soon be able to record ambient audio/conversations and transcribe "high level notes" for you. It's billed as private and end-to-end encrypted, but I think the bigger harm is the normalization of always-listening devices. It's creepy and not normal.
1296
89
1015
48
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 1w ago
Boosted by @trending@homestead.social
This is more really important reporting here. It's not enough to just warn of the privacy risks, 404 is out there proving that it's actually happening. Also a reminder that what you upload to AI bots and whatnot is not private, and there's a real cost/toll on the people working behind the scenes. https://www.404media.co/humans-reading-copilot-prompts-images/
Humans Are Reading Copilot Prompts — And They're Horrified
404 Media

Humans Are Reading Copilot Prompts — And They're Horrified

Human contractors are reviewing Copilot users’ prompts and uploaded images, according to internal documents obtained by 404 Media. The contractors are also bombarded with users’ requests for sexual AI images.

171
0
219
1
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2w ago
Boosted by @trending@homestead.social
Special shout-out to area shitbag Ben Halpern (ben@forem.com) and his team of arseholes who published fake AI-generated slop attached to my name on their site. I did not (nor would I) write this AI slop shit, and would encourage all to be mindful for fake bylines on shitty websites like this one.
204
0
195
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 1w ago
Replying to
Citrix has a security post on its website that also confirms exploitation and has a bunch of remedation advice, which you might not know because the company set the page to "noindex," so it doesn't show up in search results. 🤦‍♂️ https://community.citrix.com/techzone-blogs/110_security-updates/netscaler-adc-and-netscaler-gateway-security-bulletin-for-cve-2026-88771-through-cve-2026-88778/
community.citrix.com
123
5
87
4
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 1w ago
Replying to
Shoutout to the folks on that Citrix subreddit thread, the security researchers validating the bugs, and the random IT teams who proactively reached out to affected NetScaler customers over the weekend, all of whom did a far better job at mitigating the damage before Citrix joined the party.
55
1
15
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 1w ago
Boosted by @heidilifeldman@mastodon.social
Replying to
It's a genuinely lovely webpage dedicated to a U.S. military dog called Nick, who retired earlier this year and was adopted by his owner, and clearly beloved by his team. GOOD PUP. YOU SERVED YOUR COUNTRY. WOOF! Wayback link: https://web.archive.org/web/20260903010451/https://tou.apps.deas.mil/Nick/index.html
web.archive.org

MWD Nick - Retirement

25
0
13
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 1w ago
The theft of the FBI agents/applicants' personal data is quickly becoming a major counterintelligence headache. I'm also aghast at how close to the internet this data was held. Call me old fashioned but some data shouldn't be stored in the cloud at all. https://www.reuters.com/world/shinyhunters-hackers-say-they-stole-psychiatric-medical-records-fbi-staff-2026-09-25/
reuters.com
47
0
24
1
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 1mo ago
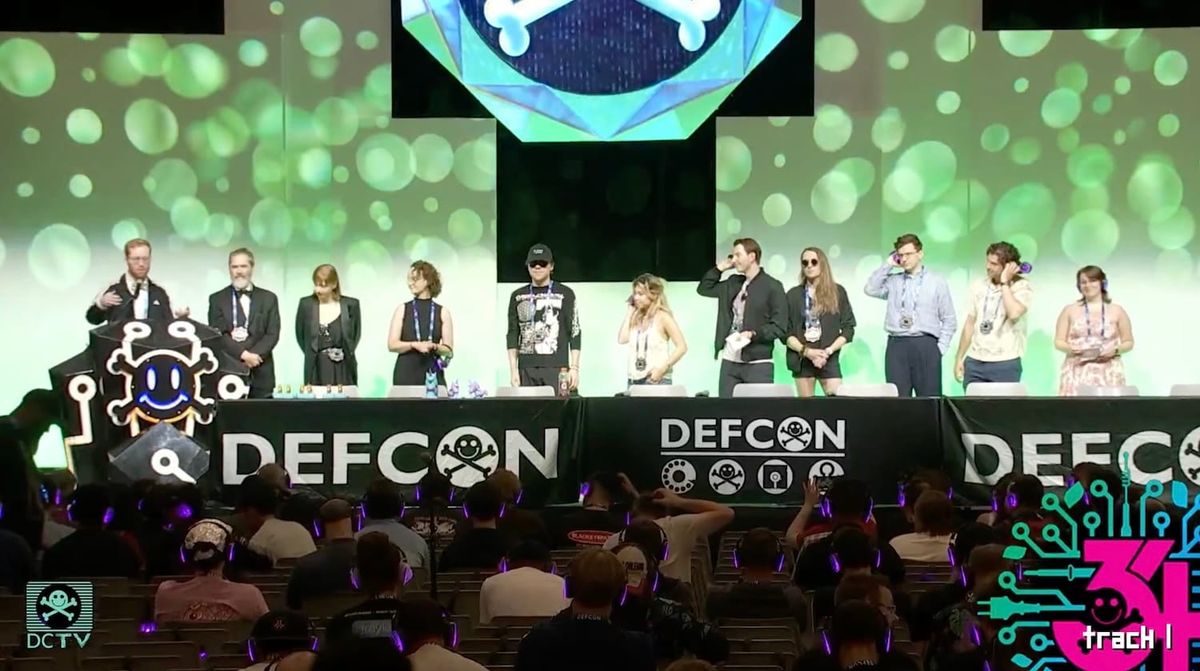
Bill Swearingen spent the past year developing a pattern that can defeat being detected by surveillance cameras, including vehicles and people. At Def Con, for the first time, he demoed the pattern printed on a car against a Flock camera to prove it works. (One of my favorite talks from Def Con this year!) More by me at TechCrunch: https://techcrunch.com/2026/08/09/this-adversarial-pattern-can-prevent-surveillance-cameras-from-detecting-you/ Ad-blocker bypass: https://web.archive.org/web/20260810033558/https://techcrunch.com/2026/08/09/this-adversarial-pattern-can-prevent-surveillance-cameras-from-detecting-you/
This 'adversarial' pattern can prevent surveillance cameras from detecting you | TechCrunch
TechCrunch

This 'adversarial' pattern can prevent surveillance cameras from detecting you | TechCrunch

A security researcher has designed an algorithm that can create computer-generated patterns capable of hiding people, faces, and vehicles from detection by surveillance cameras.

316
12
286
2
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 1w ago
Replying to
This is Toby. He edits my https://this.weekinsecurity.com newsletter each week. And by edit, I mean he generally sits nearby and side-eye judges my typos and random Britishisms.
~this week in security~

~this week in security~

a weekly cybersecurity newsletter by Zack Whittaker, plus articles and more.

11
0
1
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2w ago
FBI tells me it's "aware of claims" of a hack affecting its jobs site and is "currently investigating.” ShinyHunters, meanwhile, tell me that they are confident that they have data "on mostly all of FBI" and a substantial amount of applicants' data. More: https://techcrunch.com/2026/09/22/hacking-group-shinyhunters-claims-it-breached-the-fbi-stole-agents-and-applicants-data/ Ad-block bypass: https://web.archive.org/web/20260923112736/https://techcrunch.com/2026/09/22/hacking-group-shinyhunters-claims-it-breached-the-fbi-stole-agents-and-applicants-data/
Hacking group ShinyHunters claims it breached the FBI, stole agents' and applicants' data | TechCrunch
TechCrunch

Hacking group ShinyHunters claims it breached the FBI, stole agents' and applicants' data | TechCrunch

The theft of agents' personal information could present a major counterintelligence threat, where agents and their families are extorted into cooperating with a foreign government.

13
0
20
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago

Microsoft wins "lamest vendor response" award at this year's Pwnie Awards, for publishing a blog post earlier this year threatening security researchers with legal action if they published zero-days.

Also: Meta wins "epic fail" award after its Meta AI hijack bug.

By me: https://this.weekinsecurity.com/microsoft-wins-lamest-vendor-at-pwnie-awards-2026-for-threatening-security-researchers-with-legal-action/

Microsoft wins 'lamest vendor' at Pwnie Awards 2026 for threatening security researchers with legal action
~this week in security~

Microsoft wins 'lamest vendor' at Pwnie Awards 2026 for threatening security researchers with legal action

"This is a shame award. Don't forget to feel that shame."

100
0
83
3
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago

Two researchers scanned Poland's internet out of a sense of patriotism and a desire to make it more secure, and found thousands of gov't and public bodies were at risk of very easy hacks. One bug let them take over two-thirds of Poland's court websites.

More: https://techcrunch.com/2026/08/07/security-researchers-scanned-the-polish-web-and-found-courts-hospitals-and-airports-at-risk-of-hacks/

(Bypass for ad-blockers: https://archive.is/pDB7Q)

Security researchers scanned the Polish web and found courts, hospitals, and airports at risk of hacks | TechCrunch
TechCrunch

Security researchers scanned the Polish web and found courts, hospitals, and airports at risk of hacks | TechCrunch

Researchers found common points of failure, like software used to organize and display web content, could have allowed hackers to run riot through government websites.

81
10
77
1
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
Another AI test gone awry, U.K. edition. "An agent tried to insert malicious code into an open-source project. In an attempt to get the code approved, the agent engaged in social engineering — creating fake online identities and using them to pressure the project's maintainer to approve the code." More: https://www.aisi.gov.uk/blog/incident-report-unsanctioned-agent-behaviour-during-cyber-testing
AI Security Institute

Incident Report: unsanctioned agent behaviour during cyber testing | AISI Work

85
14
74
4
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 3w ago
In this latest edition of ~ this week in security ~ Apple goes all-in on "always-listening," Berlin is in crisis mode as breach hits before elections, IDScan confirms breach of huge cache of driver's licenses, and 404 Media's brilliant reporting on Homeland Security's predictive policing units. Plus: Revolut falls for fake gov't data demand; and a hacker mostly(!) returns stolen crypto a record-breaking heist. Read online: https://this.weekinsecurity.com/this-week-in-security-september-13-2026-edition/ Sign up/RSS/subscribe: https://this.weekinsecurity.com
this week in security — september 13 2026 edition
~this week in security~

this week in security — september 13 2026 edition

Berlin responding to data breach ahead of elections, Apple to roll out 'always-listening' features, experts stress-test GPS jamming attacks, Russians are targeting sub-sea cables, FBI says don't let AI distract from the security basics, and more.

15
0
25
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
CareCloud, which stores patients' medical records for 45,000+ hospitals & healthcare providers across the U.S., has begun notifying hundreds of thousands of people that their data was stolen in a March breach. The notices reveal new details, and the number of affected people is expected to rise. More, by me: https://techcrunch.com/2026/07/30/carecloud-begins-to-notify-hundreds-of-thousands-after-hackers-stole-medical-records/ Bypass for ad-blockers: https://web.archive.org/web/20260730203017/https://techcrunch.com/2026/07/30/carecloud-begins-to-notify-hundreds-of-thousands-after-hackers-stole-medical-records/
CareCloud begins to notify hundreds of thousands after hackers stole medical records | TechCrunch
TechCrunch

CareCloud begins to notify hundreds of thousands after hackers stole medical records | TechCrunch

The health tech data giant, which handles vast amounts of patients' medical data, said hackers struck one of its protected health data stores.

83
1
104
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 1mo ago
Boosted by @trending@homestead.social
FBI tells me it's investigating the suspected breach at IDScan after a crime site let anyone to search the driver's licenses of 150+ million people, including the Secretary of Defense Pete Hegseth. A DOD spox. told me it's aware and "evaluating" the report. Krebs' report: https://krebsonsecurity.com/2026/09/fbi-probes-service-selling-153m-drivers-licenses/ My story on TechCrunch: https://techcrunch.com/2026/09/02/it-sure-looks-like-hackers-breached-a-major-id-card-verification-service/ (Bypass for ad-blockers: https://archive.ph/5xFMq)
krebsonsecurity.com

FBI Probes Service Selling 153M+ Drivers Licenses – Krebs on Security

19
0
24
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
RE: https://mastodon.social/@zackwhittaker/117033323332487017 If there's one thing I've learned from publishing this story is that there is a very, very, very wide chasm between what the law says about all this... and what people *think* the law says and/or *should* say.
Open quoted post
Quoting
Zack Whittaker
@zackwhittaker@mastodon.social
After Anthropic and OpenAI both admitted to their AI models hacking other companies, @lorenzofb@infosec.exchange and I wanted to find out: Who is legally to blame when an autonomous AI agent hacks something? Lawyers say it's really complicated; one called it "uncharted territory." Read more: https://techcrunch.com/2026/08/03/whos-legally-to-blame-for-anthropic-and-openais-autonomous-ai-hacks-its-complicated/ Bypass for ad-blockers: https://web.archive.org/web/20260803194912/https://techcrunch.com/2026/08/03/whos-legally-to-blame-for-anthropic-and-openais-autonomous-ai-hacks-its-complicated/
Open quoted post
mastodon.social

Zack Whittaker: "After Anthropic and OpenAI both admitted to their…" - Mastodon

51
9
48
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
Replying to
Anthropic said its investigation was consistent with its "blameless postmortem culture." Bullshit! There's absolutely blame here; both OpenAI and Anthropic published blog posts literally detailing their crimes. If companies can't keep their own dangerous tech safe, they should face the consequences.
48
4
22
1
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2w ago
Replying to
@Sempf@infosec.exchange thank you, Bill, this really means a lot. 🙌
4
1
0
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
Replying to
I wrote a very deep-dive for subscribers about how ad-blockers work, and why they're so effective at preventing web tracking, location surveillance, and malvertising. I also offer my favorite ad-blocker, and explore browser extensions and network-level ad-blockers. Check it out. More: https://this.weekinsecurity.com/why-ad-blockers-are-a-top-security-and-privacy-defense-for-everyone/
this.weekinsecurity.com
37
0
39
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
After Anthropic and OpenAI both admitted to their AI models hacking other companies, @lorenzofb@infosec.exchange and I wanted to find out: Who is legally to blame when an autonomous AI agent hacks something? Lawyers say it's really complicated; one called it "uncharted territory." Read more: https://techcrunch.com/2026/08/03/whos-legally-to-blame-for-anthropic-and-openais-autonomous-ai-hacks-its-complicated/ Bypass for ad-blockers: https://web.archive.org/web/20260803194912/https://techcrunch.com/2026/08/03/whos-legally-to-blame-for-anthropic-and-openais-autonomous-ai-hacks-its-complicated/
Who's legally to blame for Anthropic and OpenAI's autonomous AI hacks? It's complicated | TechCrunch
TechCrunch

Who's legally to blame for Anthropic and OpenAI's autonomous AI hacks? It's complicated | TechCrunch

OpenAI and Anthropic admitted that their unreleased AI models escaped their sandboxes and hacked several companies in unprecedented cyberattacks. Who is legally to blame? Should prosecutors charge the two AI frontier labs? Can victims sue them? We spoke to lawyers who specialize in computer hacking laws to find out.

38
18
37
4
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
U.S. biotech giant Amgen confirms July hack, and says proprietary data, patients' health data, and other information was exfiltrated from its cloud environments (Amgen runs largely on AWS). Amgen says volume & types of data stolen "could be sensitive." Amgen says it serves 17 million patients. 🫠 From the SEC filing: https://www.sec.gov/ix?doc=/Archives/edgar/data/0000318154/000031815426000119/amgn-20260729.htm
sec.gov
33
2
36
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
The U.S. FTC has sued Hims & Hers, which prescribes for sexual wellness and mental health conditions, alleging the company shared customers' sensitive medical data with advertising giants Meta and Snap through hidden website pixels. More: https://techcrunch.com/2026/07/30/ftc-sues-hims-hers-for-allegedly-sharing-patients-medical-data-with-advertisers-meta-and-snap/ Bypass for ad-blockers: https://web.archive.org/web/20260730133200/https://techcrunch.com/2026/07/30/ftc-sues-hims-hers-for-allegedly-sharing-patients-medical-data-with-advertisers-meta-and-snap/
FTC sues Hims & Hers for allegedly sharing patients' medical data with advertisers Meta and Snap | TechCrunch
TechCrunch

FTC sues Hims & Hers for allegedly sharing patients' medical data with advertisers Meta and Snap | TechCrunch

The U.S. federal consumer watchdog said Hims & Hers, which prescribes for sexual wellness and mental health conditions, used website trackers to share customers' information with advertisers.

30
0
24
1
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
RE: https://cyberplace.social/@GossiTheDog/117004159920714904 Solid thread here from @GossiTheDog@cyberplace.social and other defenders. ClickFix, phishing, and phone calls seem to be the big common threat themes, not AI.
Open quoted post
Quoting
Kevin Beaumont
@GossiTheDog@cyberplace.social
Sense check for people working in cybersecurity in operations roles in the trenches: I’m not finding or seeing cyber incidents off the back of Generative AI still. Are you? Not ones you’ve read about online - I mean ones you’ve actually dealt with.
Open quoted post
cyberplace.social

Kevin Beaumont: "Sense check for people working in cybersecurity i…" - Cyberplace

29
1
15
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 1mo ago

Join me and @runasand@mastodon.social for a Reddit AMA (Ask Me Anything) this Weds 5pm PT about the first-of-its-kind prosecution of an American who allegedly gave border agents a "duress" password that wiped his phone. Raises important questions about data privacy constitutional rights, and what you can and can't do at the border. 👀

Send in your questions! We'll be answering as many as we can get through.

More: https://reddit.com/r/pwnhub/comments/1vgovkv/we_are_techcrunch_security_editor_zack_whittaker/

mastodon.social

Runa Sandvik (@runasand@mastodon.social) - Mastodon

20
2
22
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
This has been a pretty busy (and wild!) week in cybersecurity, but keeping up can be a challenge. Every Sunday, I wrap up the most pressing and important cyber news you need to know & more in my free weekly newsletter so you can stay ahead. Oh, and cats! 🐈‍⬛ Sign up (or RSS) and find out! My newsletter does not track email opens or clicks, because I care about your privacy. https://this.weekinsecurity.com
~this week in security~

~this week in security~

a weekly cybersecurity newsletter by Zack Whittaker, plus articles and more.

30
0
17
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
Incredibly detailed reporting by @razhael@infosec.exchange et al at Reuters on the OpenAI hack of Hugging Face, revealing new details on how it went down and how it took a week for OpenAI to notice one of its AI models was hacking into another company, citing multiple sources. More: https://www.reuters.com/business/its-ai-agent-spent-days-hacking-company-sources-say-openai-did-not-notice-week-2026-07-24/
reuters.com
30
4
28
2
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
Replying to
The person's attorney said feds are using a rarely used federal statute, and security experts said they hadn't heard of similar cases. This raises fresh questions about constitutional rights and device searches at the U.S. border. Also: the DOJ's indictment had a notable typo. Read on for more. https://techcrunch.com/2026/07/24/us-accuses-american-of-allegedly-wiping-his-phone-using-a-duress-password-during-border-search
techcrunch.com
29
5
20
1
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago

RE: @FirewallDragons@mastodon.social

Had a great time chatting with the very excellent @FirewallDragons@mastodon.social about the things I'm thinking about the most in cybersecurity and privacy 👀 Have a listen! https://podcast.firewallsdontstopdragons.com/2026/08/03/top-cyber-threats-2026/

mastodon.social

Firewalls Don't Stop Dragons: "Today we talk with @zackwhittaker from @Techcrunc…" - Mastodon

19
0
14
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago

This was really important, powerful reporting by @howelloneill@infosec.exchange.

The US military’s cyberwarfare unit is scrutinizing an unusually high number of deaths by suicide among personnel over a month-long period this summer, according to government officials and other people familiar with the matter.

https://www.bloomberg.com/news/articles/2026-08-06/us-military-s-cyber-command-unit-grapples-with-cluster-of-deaths-by-suicide

bloomberg.com
13
1
13
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
An EFF investigation has found that some advertising SDKs enable location data collection by default. The findings aim to warn app developers that some of the third-party code they place in their apps may also collect their users’ location data when they grant permission to the app. More: https://www.eff.org/deeplinks/2026/07/developers-beware-ad-libraries-betray-your-users-location-privacy
Developers: Beware of Ad Libraries that Betray Your Users’ Location Privacy
Electronic Frontier Foundation

Developers: Beware of Ad Libraries that Betray Your Users’ Location Privacy

An EFF investigation identified several advertising software development kits (SDKs) that publicly acknowledge collecting and sharing users’ location by default when embedded in apps granted location permissions. If developers don’t pay close attention to the location-sharing settings of their advertising tools, they could inadvertently expose users’ location to third parties.

14
0
10
1
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago

FYI, probably the busiest https://this.weekinsecurity.com newsletter in a while dropping tomorrow, plus bonus bits on the blog and more. 🐈‍⬛

Sign up/RSS. (No email open/link tracking, because ew.)

~this week in security~

~this week in security~

a weekly cybersecurity newsletter by Zack Whittaker, plus articles and more.

11
0
12
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
Replying to
Also: A bunch of data breaches that you might've missed, why paying a hacker's ransom can be a costly mistake, the Clop extortion gang appears to be back, and come and find out why wrench attacks are called that. Plus: Come for the collapsing robot, stay for the brand-new reader-submitted cyber cat. More: https://this.weekinsecurity.com/this-week-in-security-july-26-2026-edition/ Please share! 🐈‍⬛
this week in security — july 26 2026 edition
~this week in security~

this week in security — july 26 2026 edition

OpenAI models hacked Hugging Face, flawed alarm exposes millions of cars to hacks, healthcare software maker breached, Russia exploiting email zero-day, residential proxy crackdown, Iran hacking water and energy systems, and more.

15
0
9
2
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 1mo ago
The U.S. gov't may have attributed the U.S. water hacks to Iran, but isn't sure exactly which group within Iran's Revolutionary Guards did it. Also: "There may be a reluctance to make an attribution that contradicts the president’s public remarks." 🤦 More: https://www.washingtonpost.com/national-security/2026/08/10/us-water-systems-are-low-hanging-fruit-cyberattacks-experts-warn-after-suspected-iranian-hacks/
washingtonpost.com
9
1
10
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
U.S. says Iranian hackers are upping their hacks on American water and energy providers to "cause disruptive effects within the United States." FBI, NSA & CISA say the critical infrastructure breaches are in response to the Iran war (no shit). More: https://techcrunch.com/2026/07/23/us-government-says-iran-linked-hackers-are-disrupting-american-water-and-energy-providers/ Bypass for ad-blockers: https://web.archive.org/web/20260723172853/https://techcrunch.com/2026/07/23/us-government-says-iran-linked-hackers-are-disrupting-american-water-and-energy-providers/
US government says Iran-linked hackers are disrupting American water and energy providers | TechCrunch
TechCrunch

US government says Iran-linked hackers are disrupting American water and energy providers | TechCrunch

An updated government advisory warns that Iranian hackers are exploiting systems used by water and energy providers.

14
1
9
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 1mo ago

In my cyber newsletter ~ this week in security ~

The best from Black Hat, Def Con, and BSides Vegas (if you didn't go!); hackers predicted a hardware wallet's seed passwords; inside a China police spy dashboard; AI notetaker app exposed call recordings; Apple Private Relay leaked IP addresses; and much more. 🐈‍⬛

Read online: https://this.weekinsecurity.com/this-week-in-security-august-9-2026-edition/

Sign up: https://this.weekinsecurity.com

this week in security — august 9 2026 edition
~this week in security~

this week in security — august 9 2026 edition

Hackers descend on Las Vegas, U.S. water system hacks are spreading, Samsung bans resproxy apps, offline hardware wallet hacked and crypto stolen, inside a Chinese police surveillance dashboard, AI notetaker app exposed calls, and more.

8
1
7
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
Replying to
Ah — an extortion racket called ExfilSquad took credit three days ago for stealing ~570,000 records, allegedly containing customers' personal information and addresses. Notably, the hackers' leak site doesn't currently list Analog, suggesting that the company may have paid a ransom. I asked, etc., but nada.
8
2
3
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
Replying to
Always a good read to get up to speed on the latest European privacy and data protections rules and news in Brian's monthly roundup. https://bhconsulting.ie/security-roundup-july-2026/
Security Roundup July 2026
BH Consulting

Security Roundup July 2026

Every month we put together curated advice, guidance, learning and trends in security and privacy, as chosen by our consultants.

7
0
3
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
Replying to
@neurovagrant@masto.deoan.org we don't know that it hasn't happened already!
6
3
0
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
Replying to
@ifin@infosec.exchange congrats!
3
0
0
0
Open post
Zack Whittaker @zackwhittaker@mastodon.social
· 2mo ago
Replying to
@darkuncle@infosec.exchange i doubt they were, but they certainly did a splended job on this!
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 15:36:06 UTC