Remote
Ian Campbell 🏴
@neurovagrant@masto.deoan.org
Security ops engineer for DomainTools, DT Investigations threat researcher, writer, voracious reader. he/him. Fan of good trouble. Opinions here mine only. No LLM content from me, all flaws detected are human-generated. Autistic/depressed/anxious/hungry.
#infosec #cybersecurity #privacy #actuallyautistic #neurodivergent
4234 Followers
1638 Following
50 Posts
Joined November 13, 2022
advice:
Be the computing problem you wish to see in the world.
DomainTools Investigations:
Latest work reading list::
the rm -rf's will continue until morale improves
Open post
Boosted by @DataKnightmare@mastodon.xyz
Heard a great quote the other day that I think we should amplify:
"Windows is the Flock camera of operating systems."
64
0
59
0
Open post
RE: https://mastodon.social/@Sarahp/117010326592463918
this isn't to report AI slop
this is to help tune their model.
Open quoted post
Quoting
LinkedIn adds a button to report AI-generated ‘slop’ https://techcrunch.com/2026/07/30/linkedin-adds-a-button-to-report-ai-generated-slop/
Open quoted post 507
32
396
2
Open post
RE: https://mastodon.social/@violetblue/117277215709060410
if you find yourself saying something like "no politics in my hacking blog"
i want you to stop
think REAL hard about what you just said
and if you STILL don't understand what was incorrect about it, please for everyone's sake go sell shoes or something.
hacking is political. technology is political. always has been. and always will be.
Open quoted post
Quoting
New: when a hacking blog says "no politics" (👀), my Anthropic update, more OpenAI hack attacks emerge as Altman peddles OpenAI’s cyber-defense product, stalkers use AirTags and Teslas to murder and harass women; Meta's half-assed coverup of CSAM ads... #cybersecurity
https://www.patreon.com/violetblue/posts/cybersecurity-15-169578509
Open quoted post 52
1
37
1
Open post
Boosted by @kcarruthers@infosec.exchange
RE: https://infosec.exchange/@kcarruthers/117277224142241619
wait why would an irish band sympathize with the palestinia-
*hand to earpiece*
ohhhhhhhhhhhhhhhhhhh.
Open quoted post
Open quoted post
Quoting
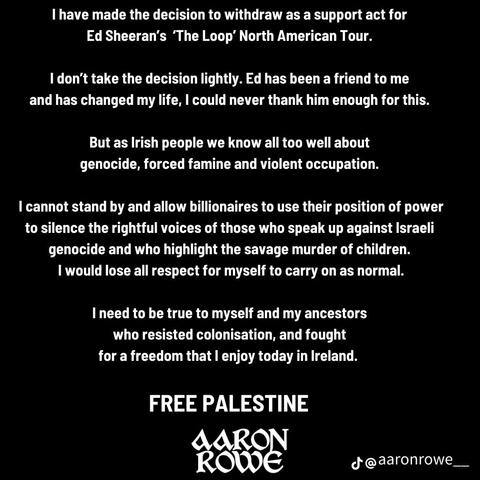
Good on Aaron Rowe: his statement on withdrawal from Ed Sheeran tour

22
0
8
0
Open post
They should put out a sequel to the Shaft series called “Shaftermath.”
Bonus points if it involves elevator engineering.
Thank you, thank you, I’ll be here all well.
5
0
2
0
Open post
The more I use it and the more I learn about it, almost every LLM use case in enterprises does one thing well:
it signals exactly where the company that’s deployed it is intent on underspending.
112
2
67
0
Open post
Open post
Exhausting, demoralizing, generally bad day.
Please send good memes.
13
3
1
0
Open post
RE: https://cyberplace.social/@GossiTheDog/117009205530767591
hey it's almost like, once again, adblocking is a critical security measure
Open quoted post
Quoting
Adform, a web advertising firm, have been hacked and have been serving a supply chain attack to steal crypto https://doublepulsar.com/adform-compromised-to-serve-crypto-stealer-via-supply-chain-attack-2f1ec024f33e
Open quoted post 70
7
90
0
Open post
*pokes head up from conference-land, gasping for air*
so...i miss anything good out in the world, or more of the same?
4
2
0
0
Open post
Replying to
@spiegelmama@infosec.exchange The wording is a pretty transparent appeal to AI opponents, but it's not in order to reduce AI content.
It's utilizing volunteer bias to get those most opposed to share how they detect (or think they detect) AI prose in order to make it less detectable.
In short, fuck em.
43
2
11
0
Open post
Replying to
@briankrebs@infosec.exchange I would love to see the raw body of the scam email to see if there was any attempt at prompt injection, or if it was literally just Gemini falling for a basic scam email.
37
5
1
0
Open post
Open post
RE: https://techhub.social/@Techmeme/117308800902835850
They're not sending their best...
Open quoted post
Quoting
Investigation: AI hacker house AGI House had 37 incidents logged by police since 2022, many for party-related complaints, as Bay Area tech houses proliferate (Kirsten Grind/New York Times)
https://www.nytimes.com/2026/09/21/technology/agi-house-ai-culture.html
http://www.techmeme.com/260921/p20#a260921p20
Open quoted post 2
1
0
0
Open post
Open post
2
1
2
0
Open post
Open post
Replying to on masto.deoan.org
i hate this fucking timeline. integrity and vigilance are apparently for chumps.
4
1
0
0
Open post
RE: https://mastodon.social/@hrbrmstr/117031467694127984
Gonna be a hot one in Vegas, unsurprisingly.
An important reminder: certain medications, including and especially some antidepressants (SNRIs and some SSRIs) increase your heat sensitivity deeply.
Some also increase your alcohol sensitivity deeply.
Please take care.
7
1
5
0
Open post
Palworld update:
I kinda started counterfeiting gold coins.
This caused the cops to raid my base.
I had forgotten to log out and just left it running,
but luckily my base is ringed with a series of .50 caliber machine guns crewed by witches
as well as several dinosaurs wielding rocket launchers.
And that’s Palworld.
7
0
1
0
Open post
Replying to
add to that:
ssokeyportal[.]com - first seen 25 or so minutes ago.
1
0
1
0
Open post
Cyber defense is adversarial. Swagger for every block, strut like you own it for every detection, dance for every threat uncovered.
Don’t let attackers have all the fun. We are the adversaries. Defend and hunt like you damn well mean it.
Happy hacker summer camp, friends.
5
1
0
0
Open post
I reckon they can skip most of the diagnostic battery for autism on this one
5
0
0
0
Open post
Open post
Hugging Face wasn’t the only target of OpenAI’s uncontrolled/unsupervised agent
https://www.reuters.com/business/openais-rogue-agent-compromised-an-account-second-tech-firm-sources-say-2026-07-28/
5
1
4
0
Open post
Me, elsewhere: “I long for the NorseCorp days now. Back when it was artisanal, hand-crafted cyber grift, rather than AI slop irresponsibly rushed to market.”
4
1
0
0
Open post
RE: https://infosec.exchange/@metacurity/117031178228141971
lol okay Partnered Health
Open quoted post
Quoting
"Partnered Health has obtained an injunction preventing access to the data itself for any purpose."
https://www.cyberdaily.au/security/13986-exclusive-partnered-health-responds-to-inc-ransom-data-breach-claims
Open quoted post 4
1
2
0
Open post
Replying to
@zackwhittaker@mastodon.social what do you think Grok is doing?
I'm guessing popping iCloud accounts for nudes.
4
0
0
0
Open post
RE: https://ioc.exchange/@abuse_ch/117009056997384855
QUIT ABUSING THE ABUSE SERVICE!
c'mon people. having been on the receiving end of similar, y'all gotta realize just how finite the resources are to keep something like this rolling, and how hard it is to secure more while still serving the community.
Open quoted post
Open quoted post
Quoting
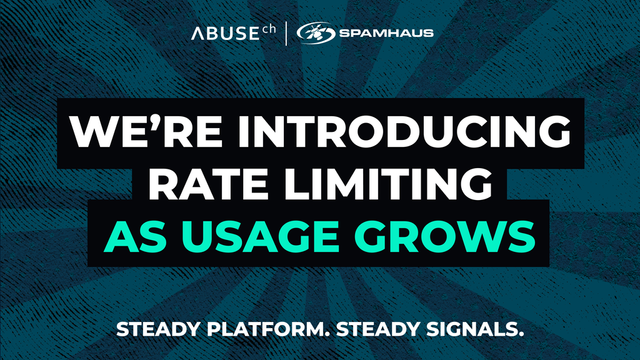
📢 SERVICE UPDATE | As you may have noticed, we've experienced some downtime recently which was largely caused by a small number of users exceeding our Fair Use Policy.
To protect platform stability and ensure fair access for everyone as our user base grows, we are introducing API rate limits. Accounts generating unusually high query volumes may be temporarily limited for up to 72 hours.
Repeated or persistent abuse may result in longer-term restrictions on API access.

4
1
2
0
Open post
RE: https://infosec.exchange/@psylo/117003011519421493
My paid sub to Psylo continues to help me sleep at night
Open quoted post
Open quoted post
Quoting
Psylo 1.3.0 was just approved 🥳🤘 It took a whole week to go through app review but luckily with 0 rejection rounds.
It’s a pretty big release with major improvements to performance, anti-fingerprinting, and website compatibility.
Full release notes 👇

4
1
1
0
Open post
Replying to
@zackwhittaker@mastodon.social can't wait until it happens to a defense contractor
2
5
0
0
Open post
Replying to
@freediverx@mastodon.social @psylo@infosec.exchange Psylo's a @mysk@mastodon.social project - they've made more substantial contributions to iOS privacy, over the course of years, than anyone else I can think of
2
1
0
0
Open post
Replying to
When you see one week that the Central Bank of Iran is specifically looking for partners to convert Iranian rials to UAE dirhams,
and the next week that there's suddenly a flourishing of Dubai startups doing dirham-backed stablecoins,
it doesn't take Sherlock Holmes to really get it.
2
0
0
0
Open post
Think I’ll propose an “east coast early riser” track for hacker summer camp next year. Prospective agenda:
0300 - Coffee (Dunkin’s)
0330 - Welcome
0335 - Keynote - Why the Red Sox Are Better Even When They’re Worse
0336 - More Coffee (still Dunk’s)
0337 - Leaving each other alone until the coffee takes hold
0400 - Lightning Talks, Boston Format (mid-word r letters may not be fully pronounced)
0500 - Break for… you guessed it… coffee.
0530 - Expert Panel - Boston Bluntness or Autistic Bluntness or Both? Saying What We Think as a Superpower
0615 - Lightning Talks II - Airing of Grievances
0730 - Locknote - Per My Last Email, Guy
0800 - Coffee.
1
1
0
0
Open post
Replying to
@xorhex@infosec.exchange @mysk@mastodon.social @freediverx@mastodon.social @psylo@infosec.exchange i'm awful at chess. only winning move for me is not to play. ;)
1
5
0
0
Open post
thinking about blackhat/defcon, and some year i want my org to sponsor a quiet reading party.
maybe low-key waitstaff taking care of drinks and snacks, and handing out warm washcloths.
"no eye contact chill rager; unless someone's wearing a green sign they get left alone to rest"
back in my meditation days, at the retreat center the folks on silent retreats would wear a big button that said "in loving silence"
i wonder what the hacker equiv would be
1
4
1
0
Open post
Open post
Oh this is a good one.
Physical letters being mailed out by a threat actor pretending to be the IRS, trying to get folks to "declare" their cryptocurrency holdings in a fake portal that auths to and drains the wallets.
https://www.coinbase.com/blog/consumer-protection-tuesday-fake-irs-scam
0
0
0
0
Open post
Replying to
@ADHDruid@infosec.exchange @da_667@infosec.exchange @cR0w@infosec.exchange @krypt3ia@infosec.exchange oh da and I have compared notes on Rimworld already.
It’s where I let the worst version of myself out to play, and da seems to do the same thing.
0
1
0
0
Open post
Replying to
@cR0w@infosec.exchange honestly? it's a good thing you didn't come to Vegas.
ai psychosis as far as the eye could see, drowning out people doing the Actual Work.
0
1
0
0
Open post
Replying to
@winterknight1337@infosec.exchange @da_667@infosec.exchange gotta admit i don't know this reference off the top of my head
0
1
0
0
Open post
Open post
RE: https://infosec.exchange/@BleepingComputer/117077078527523059
Now - these things can happen of course - but there is not one single detail as to *how* it happened or how they've changed process to avoid it happening again.
This is confirmation bias for me, sure, but whaddaya wanna bet AI was involved?
https://blog.mozilla.org/security/2026/08/10/updated-gpg-key-for-signing-firefox-and-thunderbird-releases/
Open quoted post
Quoting
Mozilla announced today that it updated the GPG key used to sign Firefox and Thunderbird releases after it was accidentally exposed on GitHub.
https://www.bleepingcomputer.com/news/security/mozilla-updates-gpg-key-for-signing-firefox-thunderbird-releases-after-exposure/
Open quoted post 0
16
1
0
Open post
RE: https://infosec.exchange/@da_667/117009614714601301
WELL THAT'S A RELIEF
IT'S A GOOD THING A MASTER KEY HAS NEVER BEEN ABUSED ACROSS MICROSOFT ENVIRONMENTS BEFORE
PERHAPS THEY WILL LEARN FROM THIS SINGULAR UNIQUE EXPERIENCE
0
1
0
0
Open post
Replying to
@krypt3ia@infosec.exchange shrug
i'm a fan. think she does good work, from a unique and important perspective.
0
1
0
0
Open post
Replying to
@davidfetter@kolektiva.social david we've had the discussion previously about what you should do if you don't like things i'm talking about:
go elsewhere.
i'm too tired to humor you today.
0
0
0
0