Exa 
Full Stack Devops Engineer
⭐️ #web #sysadmin #programming #infosec #privacy
Arch Linux
Sway
neovim
Someone apparently found some security issues in Forgejo but isn't willing to follow the security procedure of the project.
What is troubling me is that their posts calling out of the potential vulnerabilities are getting removed on Mastodon, first on infosec[.]exchange then on mastodon[.]social.
What is the limit on rules against harassment when it targets an entity (the Forgejo/Codeberg project) and not individuals? Is it okay to downplay or hide the potential security issues in this story?
I'm happy to host my own instance with my own rules.
https://dustri.org/b/carrot-disclosure-forgejo.html
EDIT: The post in question was restored on infosec[.]exchange.
I just don't like this part:
All EPI and Wero data is stored in European data centers, and is encrypted and protected against potential extraterritorial access through appropriate security measures.
The application that runs on AWS surely has access to the encryption keys. Sounds like an excuse. Unless proven otherwise it doesn't prevent extraterritorial access.
@macgeneration@social.macg.co Euh ... C'est incompréhensible techniquement ça.
Là où beaucoup de protocoles font transiter le trafic de plusieurs personnes dans un tunnel partagé, Surfshark explique que Dausos attribue à chacun son propre tunnel dédié. Autrement dit, les données ne circulent pas dans le même couloir que celles des autres utilisateurs, ce qui doit limiter certaines pertes d’efficacité et renforcer l’isolation du trafic.
C'est quoi un tunnel partagé ? Un VPN dans le sens qu'on l'entend est un NAT + un tunnel pour chaque utilisateur.
Et plus rapide qu'AES je veux bien voir ça, sachant que les CPU ont un support matériel pour AES depuis des années.
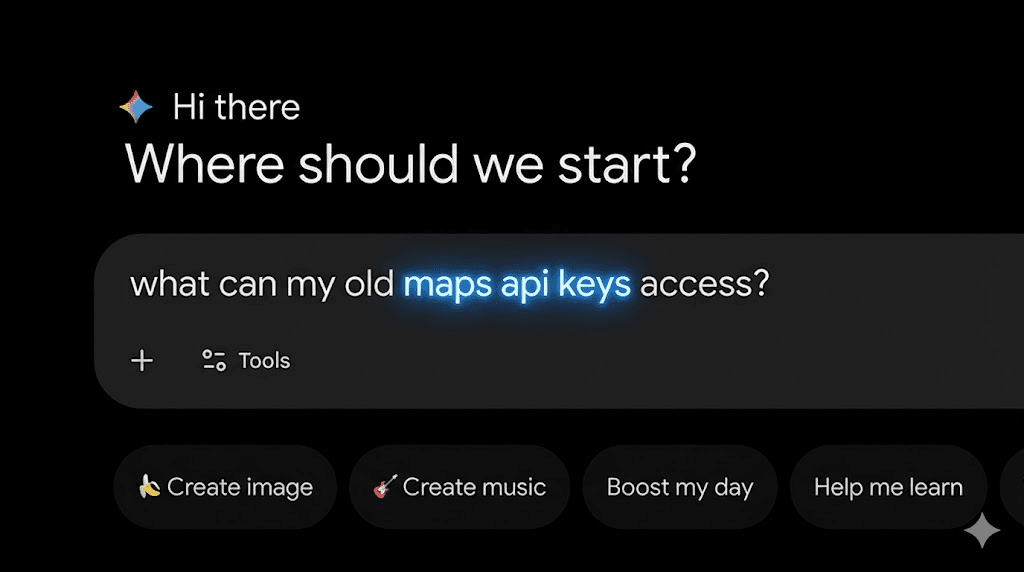
We scanned millions of websites and found nearly 3,000 Google API keys, originally deployed for public services like Google Maps, that now also authenticate to Gemini even though they were never intended for it. https://trufflesecurity.com/blog/google-api-keys-werent-secrets-but-then-gemini-changed-the-rules via https://news.ycombinator.com/item?id=47156925