Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

sash

@sash@hachyderm.io
mastodon 4.7.3
  • Open on hachyderm.io

Writing Python & more 🐍 • internet infrastructure & standards • community organiser • aspiring rustacean 🦀 • Write the Docs • IRRD & BGP • 🏳️‍🌈🏳️‍⚧️ • she/they

812 Followers
391 Following
30 Posts
Joined February 09, 2023
www:
mxsasha.eu
ASN:
213279
work:
reliablycoded.nl
Open post
sash @sash@hachyderm.io
· 6mo ago

Are you still only using two factor authentication? I'm way ahead of you with my 7 factor authentication 🔐

1038
59
441
6
Open post
sash @sash@hachyderm.io
· 4mo ago
Boosted by @trending@homestead.social
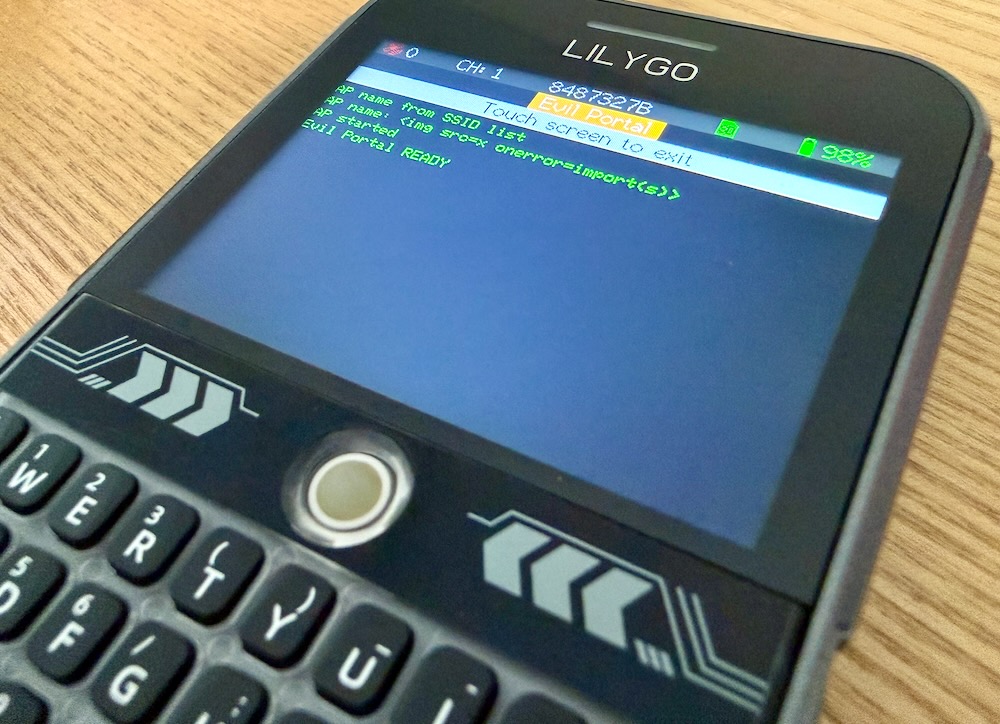
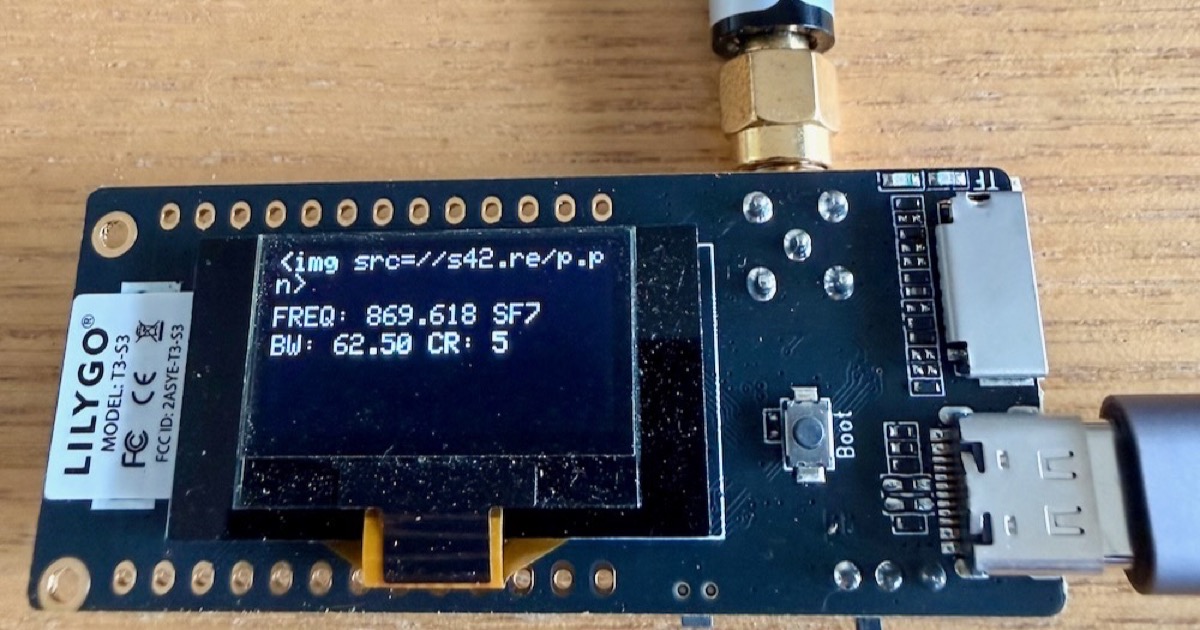
I found that crafted MeshCore node names could compromise Home Assistant instances running meshcore-card, with an XSS leading to remote root access on the HA host. An attacker could then access anything controlled or visible through Home Assistant. The attacker doesn't need to be near the target, as MeshCore advertisements are repeated over the mesh, which is dense in NL. This also affects around 20 public MeshCore analyzer websites. Some of those run CoreScope, where it looks like a vibecoding bot broke the XSS filter while hallucinating a bugfix. The analyzers are mostly public data though. In addition, the less popular MeshCore-Home-Assistant-Panel-v2 is likely also affected, but I was unable to make contact with the maintainer. MeshCore node names are only 32 bytes, and each rendered in a different place in the page, so I had to be creative to run a more substantial payload. I found a way with three node names using an iframe feature I never heard of before. https://mxsasha.eu/posts/meshcore-xss-home-assistant/
Rooting Home Assistant through MeshCore: XSS attacks with a LoRa node name
mxsasha.eu

Rooting Home Assistant through MeshCore: XSS attacks with a LoRa node name

A crafted MeshCore node name could compromise any Home Assistant instance running meshcore-card as soon as someone viewed a dashboard with that card. MeshCore …

194
28
218
5
Open post
sash @sash@hachyderm.io
· 5mo ago

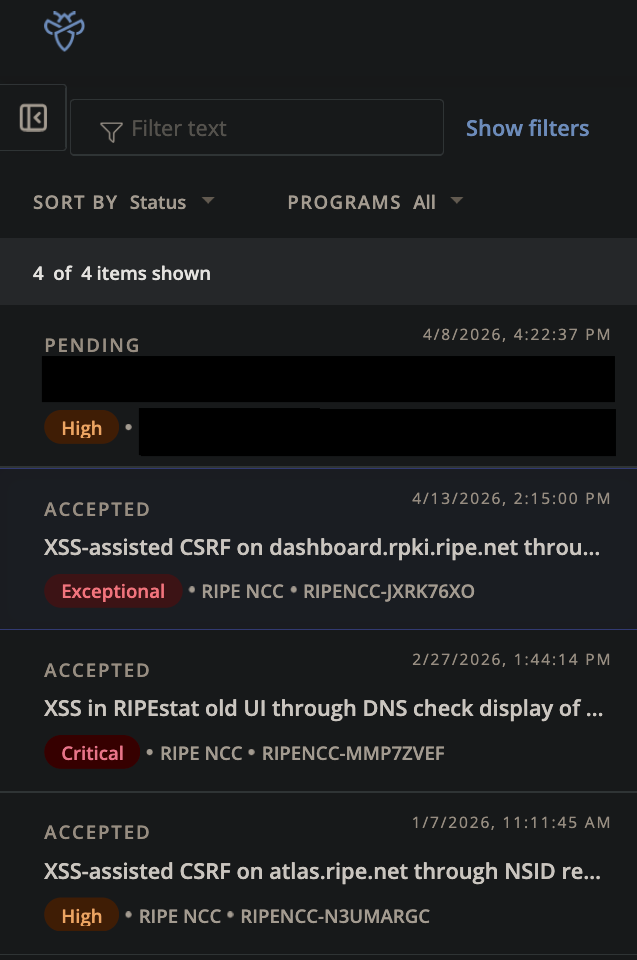
RIPE NCC made session tokens for the entire member portal available to over 1000 third parties, by design. Full access to the RPKI dashboard, the RIPE Database, and everything else. RIPE NCC had placed strangers under the same domain as their most critical systems.

The RIPE NCC SSO cookie is scoped to `*.ripe.net`, so browsers send it to any HTTPS server under that domain. Atlas anchor hosts and RIPE meeting attendees all had assigned hostnames under that domain, and nothing stopped them from requesting a valid TLS certificate for those hostnames. A single link click was enough to leak the token.

The impact went further than my publication from last week with XSS+CSRF: this allows full session access, including adding admin users and API keys that persist silently.

Full write-up: https://mxsasha.eu/posts/ripe-ncc-sso-cookie-exposure/

Resolved about 3 months after my report, by adding two DNS records. RIPE NCC has not published any acknowledgement of this vulnerability, nor credited me as the reporter on their own channels.

1000 third parties could have stolen RIPE NCC session tokens - by design
mxsasha.eu

1000 third parties could have stolen RIPE NCC session tokens - by design

The RIPE NCC made its all-powerful single sign-on tokens available to over 1000 third parties. From a single link click, any logged-in RIPE NCC user would leak …

127
10
140
3
Open post
sash @sash@hachyderm.io
· 6mo ago

Rooting OpenWRT from the parking lot: I discovered an XSS in the OpenWRT SSID scan page, that can be chained to remote root access 👾
Write-up and demo: https://mxsasha.eu/posts/openwrt-ssid-xss-to-root/
CVE-2026-32721, fixed in 24.10.6 / 25.12.1

Root from the parking lot: OpenWrt XSS through SSID scanning (CVE-2026-32721)
mxsasha.eu

Root from the parking lot: OpenWrt XSS through SSID scanning (CVE-2026-32721)

Lately, I’ve been experimenting with unusual XSS vectors. XSS (cross-site scripting) allows an attacker to execute arbitrary javascript in another …

157
18
129
0
Open post
sash @sash@hachyderm.io
· 4mo ago

A RIPE Atlas probe could have been enough to hijack a RIPE NCC user's next login, giving full access to the member portal, including the RPKI dashboard and the RIPE Database.

I discovered a session fixation vulnerability in RIPE NCC's single sign-on: the session token was not rotated on login. Two ways to exploit it: a new XSS in RIPEstat through DNS NS records, or a free Atlas probe. Anyone with a free RIPE NCC account can host a probe, approved automatically. Installing a web server and serving one HTML page was all it took.

This builds on my earlier posts on the XSS+CSRF exploit chain and session token exposure through CAA misconfigurations: https://mxsasha.eu/posts/ripe-ncc-session-fixation/

The vulnerability was fixed within 20 days. This all took place before my #RIPE92 talk from last week, only some of it made it into that talk. More structural fixes are pending.

mxsasha.eu
32
1
25
0
Open post
sash @sash@hachyderm.io
· 5mo ago

Just over 4 years after publishing the first draft, NRTMv4 has been approved by the IESG! This was my first ever IETF draft. This new protocol dramatically improves Internet Routing Registry security and reliability.

All that remains now is the RFC Editor process. Four authors went through 11 versions, 25 reviewers/implementers, dozens of comments, and 5 interoperable implementations. Catch my talk at the #RIPE92 database working group to learn more.

https://datatracker.ietf.org/doc/draft-ietf-grow-nrtm-v4/

hachyderm.io
33
1
18
0
Open post
sash @sash@hachyderm.io
· 5mo ago
Replying to
My disclosure process with RIPE NCC took 14 months, 26 messages, and included two incorrect fixes for the same vulnerability. I wrote about the process, with thoughts on what better would look like for RIPE NCC and others: https://mxsasha.eu/posts/ripe-ncc-disclosure-retrospective/
Inside a 14-month responsible disclosure with the RIPE NCC
mxsasha.eu

Inside a 14-month responsible disclosure with the RIPE NCC

This post covers the disclosure process for the vulnerabilities described in my RPKI exploit chain, through RIPE NCC’s Responsible Disclosure Policy. …

30
0
13
0
Open post
sash @sash@hachyderm.io
· 4mo ago
Replying to
@litchralee_v6@ipv6.social yes, also because HTML is just one option. Maybe someone puts them in SQL, or LDAP, or shell. Only the code that prepares it for a particular context can know how to make it safe.
5
0
1
0
Open post
sash @sash@hachyderm.io
· 6mo ago

RE: @sash@hachyderm.io

Thank you, people of mastodon and reddit ✨I was already aware this is not actually 7-factor auth technically ✨
Also it's a bad idea mainly for other reasons: one glitch in this usb hub could fry all my keys at the same time 🔥

hachyderm.io
10
1
2
0
Open post
sash @sash@hachyderm.io
· 5mo ago

I have been working on a set of vulnerabilities for 14(!) months, but the end is in sight! Just sent the draft blogs to the vendor for review, got € 3200 in bug bounties, and in two weeks I should be able to publish my attack chain on critical internet infrastructure 🕵️‍♀️

8
0
2
0
Open post
sash @sash@hachyderm.io
· 6mo ago
Replying to
The password is #7. And actually there were two more tokens that didn’t fit in this hub :)
9
2
0
0
Open post
sash @sash@hachyderm.io
· 6mo ago
Replying to
@zuthal @wmd I remember those for serial ports, I'm not an electrical engineer but I think it will create some issues with usb
7
2
0
0
Open post
sash @sash@hachyderm.io
· 4mo ago
Replying to
@po3mah@mastodon.social if it's the latest version of meshcore-card, you are safe for the vulnerability I documented it, to the best of my knowledge. And the maintainer of meshcore-card handled my disclosure perfectly.
2
0
0
0
Open post
sash @sash@hachyderm.io
· 5mo ago
Replying to
@hrbrmstr Thanks! Plenty of things are broken, I have a backlog of disclosures and posts. Next week I'll have another RIPE NCC post. That one is a bit harder, but much more rewarding, with full session takeover and persistent access.
3
1
0
0
Open post
sash @sash@hachyderm.io
· 6mo ago
Replying to
@tecHunt @jill I just kind of gathered them over time. Some are a bit old and crappy, but they work for U2F. My newest is a Token2 Bio3, didn't fit in the hub.
3
0
0
0
Open post
sash @sash@hachyderm.io
· 6mo ago
Replying to
@BafDyce Yeah that took me a bit of time to find. An alert(1) fits easy of course, but I have the most fun if I can show a full running exploitation to something practical :)
3
0
0
0
Open post
sash @sash@hachyderm.io
· 5mo ago
Replying to
@nyanbinary yes, although in this case, "administrative" includes almost any RIPE NCC platform, like e-learning courses, the blog (RIPE Labs), running an Atlas measurement, submitting a talk to a RIPE meeting, and so on. The same session token covers all services.
2
1
0
0
Open post
sash @sash@hachyderm.io
· 5mo ago
Replying to
@jelte openssl calls this SignatureAlgorithms, and Postfix has no direct option for this, you need to do it through openssl.conf. Here's my latest config for this: https://github.com/internetstandards/Internet.nl/issues/1553#issuecomment-4306775294
GitHub

Update integration test environment to use proper mail server to test 100% mail · Issue #1553 · internetstandards/Internet.nl

Currently we use mailhog, which does not support TLS at all. Migrating to a proper mail server would allow us to test this better in the integration tests. Recently, I wrote a postfix configuration...

2
2
0
3
Open post
sash @sash@hachyderm.io
· 6mo ago

Tracking 30 vulnerability findings right now, all variations on the same mistake. Responsible disclosure is getting pretty draining. Vendors range from pretty great to deeply exhausting. Some of this is account takeover, some of it is worse. I do this in my free time, so irresponsible disclosure is starting to sound appealing :)

2
0
0
0
Open post
sash @sash@hachyderm.io
· 4mo ago
Replying to
@meph@social.treehouse.systems yes, bots, misconfigured clients, and similar, are sometimes a problem in NL too. MeshCore is pretty easy to DoS even by accident, in EU we also have max 10% duty cycle for transmit.
1
0
0
0
Open post
sash @sash@hachyderm.io
· 6mo ago

RE: @koire@hachyderm.io

FIDO2 tokens (like yubikey) are great, but you either want more than one or a good process around recovery codes. Making logins more complicated will lower the risk of account compromise, but increase the risk of locking yourself out. Always have a plan for what happens if a token, phone or other hardware breaks, is lost, or stolen.
hachyderm.io
2
0
0
0
Open post
sash @sash@hachyderm.io
· 6mo ago
Replying to
@silhouette until the hub glitches and fries every key at the same time 🔥
2
0
0
0
Open post
sash @sash@hachyderm.io
· 5mo ago
Replying to
@alex@fedi.smith.geek.nz here it is: https://hachyderm.io/@sash/116526841260403543
hachyderm.io
1
1
0
0
Open post
sash @sash@hachyderm.io
· 5mo ago
Replying to
@alex@fedi.smith.geek.nz I can't be sure if ASPA was vulnerable. It's the same GraphQL API, but there is an additional entityTag field, and there are some requirements on it. I can't determine if it's enough to function as a CSRF token. As it is the same API, it now too has the stricter CORS and Content-Type filters. My next two posts will cover full RIPE NCC session takeovers, so that one would definitely have included ASPA :)
1
3
0
0
Open post
sash @sash@hachyderm.io
· 5mo ago
Replying to
@jelte ah good catch, missed that line - I added it to my sample
1
0
0
0
Open post
sash @sash@hachyderm.io
· 6mo ago
Replying to
@Hyperlynx it's just a sticker, it's this one: https://www.yubico.com/nl/product/yubistyle-covers-tie-dye-keychain-usb-a-c-nfc/ They make a few other nice ones: https://www.yubico.com/nl/product/yubistyle-covers-usb-a-c-nfc/
yubico.com
1
0
0
0
Open post
sash @sash@hachyderm.io
· 6mo ago
Replying to
@lunareclipse or just don't open that scan page ;)
1
0
0
0
Open post
sash @sash@hachyderm.io
· 6mo ago
Replying to
@uvok there's a lot of these, I've been playing with it a lot over the last year, and I have some more fun ones in my queue waiting for release :)
0
0
0
0
Open post
sash @sash@hachyderm.io
· 6mo ago
Replying to
@GoblinKing_f@pawb.fun I don't, they are partially backups for each other. Some off-site, some with me, some at home, some in the office :)
0
1
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 16:08:28 UTC