Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Trail of Bits

@trailofbits@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

We help secure the world’s most targeted organizations and products. We combine security research with an attacker mentality to reduce risk and fortify code.

1868 Followers
5 Following
50 Posts
Joined October 31, 2022
Website:
https://trailofbits.com
Podcast:
https://trailofbits.audio
GitHub:
https://github.com/trailofbits
Blog:
https://blog.trailofbits.com
Open post
Trail of Bits @trailofbits@infosec.exchange
· 2w ago
SAML was created in 2002 by merging four rival XML security protocols into one spec. That design still generates vulnerabilities: a canonicalization flaw via XML comments in 2018, XML round-trip bugs in Go's stdlib in 2020, a GitHub Enterprise SAML auth bypass in 2025, and more. Matt Schwager breaks down 5 design flaws behind the pattern and makes the case for moving to OIDC. https://blog.trailofbits.com/2026/09/21/saml-a-fractal-of-bad-design/ #SAML #OIDC
SAML: A fractal of bad design
The Trail of Bits Blog

SAML: A fractal of bad design

SAML, the XML-based authentication protocol that birthed the SSO industry, is fundamentally flawed due to XML complexity, canonicalization issues, enveloped signatures, and design ossification, making it vulnerable to signature wrapping attacks and parser differentials that persist despite decades of awareness. Organizations should migrate to OpenID Connect (OIDC), which avoids these pitfalls through simpler JSON-based design, detached signatures, and agile evolution.

4
1
4
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago

Google used a ZK proof to disclose a quantum breakthrough that cuts the cost of breaking cryptocurrency by 20x without handing attackers the circuit.

The Rust code behind the proof had memory safety bugs. We used this new attack surface to forge a proof that beats Google’s on every metric.

Google patched it within days. Their quantum claims are unaffected. https://blog.trailofbits.com/2026/04/17/we-beat-googles-zero-knowledge-proof-of-quantum-cryptanalysis/

blog.trailofbits.com
41
1
25
2
Open post
Trail of Bits @trailofbits@infosec.exchange
· 6mo ago

C and C++ run your OS, your browser, your database, and your critical infrastructure. They're also the easiest languages to get catastrophically wrong.

We wrote down everything a security auditor should check: language-level bug classes, stdlib pitfalls, Linux and Windows issues from usermode to kernel, seccomp sandbox escapes, and ptrace handler race conditions.

One checklist, hundreds of checks. https://appsec.guide/docs/languages/c-cpp/

appsec.guide
18
1
16
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 2mo ago
Attackers drained $20M+ from protocols built around Uniswap v4 hooks. The two largest were Cork (~$12M) and Bunni ($8.4M). Neither came from bugs in the PoolManager, Uniswap v4's central contract. The failures came from application and hook code. We analyzed dozens of audit findings to isolate seven ways hooks break, and created a checklist for keeping these bugs out of production. https://blog.trailofbits.com/2026/07/30/building-secure-uniswap-v4-hooks/#infosec #DeFi #smartcontracts
blog.trailofbits.com
2
0
1
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 4mo ago

Go's fuzzer can't solve path constraints, fuzz typed inputs, or catch data races and goroutine leaks.

gosentry is our fork of the Go toolchain that brings a LibAFL engine in Rust, Nautilus grammar fuzzing, struct-aware mutation, and race/leak detection into `go test -fuzz`.

Same harness, stronger engine. We already used it to disclose 4 bugs in Optimism and Revm. https://blog.trailofbits.com/2026/05/12/go-fuzzing-was-missing-half-the-toolkit.-we-forked-the-toolchain-to-fix-it./

blog.trailofbits.com
7
1
8
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago

RE: @pypi@fosstodon.org

4 billion downloads a day run through @pypi@fosstodon.org. A missing permission check let any org member invite new owners. One of 14 findings from our second audit.

fosstodon.org
9
0
6
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 6mo ago

93% recall vs 50% for baseline prompts. Our new dimensional-analysis plugin for Claude Code doesn’t ask the LLM to find bugs. It annotates your codebase with dimensional types, then flags mismatches mechanically. Tested against real audit findings. https://blog.trailofbits.com/2026/03/25/try-our-new-dimensional-analysis-claude-plugin/

blog.trailofbits.com
11
1
3
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 6mo ago

Thousands of CEOs said AI had no impact on productivity. We use AI to catch 200 bugs/week where we used to find 15, and generate $8M per sales rep.

95% of the company pushed back when we started. At unprompted, Dan Guido explains how our 140-person team went AI-native.
https://www.youtube.com/watch?v=kgwvAyF7qsA

8
1
7
1
Open post
Trail of Bits @trailofbits@infosec.exchange
· 7mo ago

New tool release! Linux memory forensics requires external debug symbols that precisely match your kernel version, symbols rarely installed on production systems and often missing after updates.mquire eliminates this dependency entirely by extracting BTF type information and Kallsyms symbol addresses directly from the memory dump. Works on kernel 4.18+ with BTF enabled.
https://blog.trailofbits.com/2026/02/25/mquire-linux-memory-forensics-without-external-dependencies/

blog.trailofbits.com
11
0
10
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 6mo ago

We open-sourced the system we built to make Trail of Bits AI-first. A six-step playbook for embedding AI into how your team actually works, not just what tools they have access to.

In 8 weeks we went from 5% to 67% Claude Code co-authorship on merged PRs across 59 contributors and 35 repos, from security engineers to PMs to sales. All through systematized adoption any exec can copy.
https://blog.trailofbits.com/2026/03/31/how-we-made-trail-of-bits-ai-native-so-far/

How we made Trail of Bits AI-native (so far)
The Trail of Bits Blog

How we made Trail of Bits AI-native (so far)

We had 5% buy-in and 95% resistance. A year later, AI-augmented auditors are finding 200 bugs a week on the right engagements. Here’s the six-part operating system we built, open sourced, and are giving away.

7
0
1
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 6mo ago

Before its launch, we audited WhatsApp's Private Processing TEEs and found 8 high-severity issues (patched). The enclaves yielded to injected config files, unmeasured ACPI tables, spoofed firmware levels, and stale attestation reports.

TEE security is only as good as the implementation details. Four lessons and the full report: https://blog.trailofbits.com/2026/04/07/what-we-learned-about-tee-security-from-auditing-whatsapps-private-inference/

What we learned about TEE security from auditing WhatsApp
The Trail of Bits Blog

What we learned about TEE security from auditing WhatsApp

Our audit of WhatsApp’s new “Private Inference” feature shows that trusted execution environments (TEEs) aren’t a silver bullet.

7
0
7
1
Open post
Trail of Bits @trailofbits@infosec.exchange
· 2mo ago
Both Black Hat keynotes this year are about AI and vulnerability research: "The End of Rare" and "Vulnerability Research in the Agentic Age." Our entire company restructured around AI a year ago. Select engagements went from 15 bugs a week to 200. In just the past two months we found 1,000+ issues in cURL, Python, Go, and other open-source projects. We'll be in Vegas this week. Book time: https://meetings.hubspot.com/trailofbits/blackhat-defcon-scheduling #BHUSA #DEFCON
meetings.hubspot.com
1
0
2
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago

Our C/C++ code review challenge closes April 17.

The new Testing Handbook chapter covers memory safety, integer errors, type confusion, kernel modules, Windows usermode, and seccomp sandbox escapes through manual code review.

Analyze the vulnerable programs, explain how to exploit them, and submit a writeup. First 10 correct entries win swag.

https://trailofbits.com/c-whats-wrong-challenge/

trailofbits.com
5
0
4
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 7mo ago

Before launch, Perplexity hired us to test the security of Comet, their AI browser assistant. We demonstrated how four prompt injection techniques could extract users' private information from Gmail. https://blog.trailofbits.com/2026/02/20/using-threat-modeling-and-prompt-injection-to-audit-comet/

blog.trailofbits.com
8
0
3
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 7mo ago

Carelessness versus craftsmanship in cryptography
Two popular AES libraries (aes-js and pyaes) provide dangerous default IVs that lead to key/IV reuse vulnerabilities affecting thousands of projects. One maintainer dismissed the issue, while strongSwan's maintainer exemplified proper security response by comprehensively fixing the vulnerability in their VPN management tool.
https://blog.trailofbits.com/2026/02/18/carelessness-versus-craftsmanship-in-cryptography/

blog.trailofbits.com
8
0
10
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 8mo ago

How to run Claude in YOLO mode safely: Use our devcontainer for full file and network isolation. https://github.com/trailofbits/claude-code-devcontainer

Not isolated enough? We're also sharing dropkit, our custom CLI for quickly accessing DigitalOcean droplets for security testing and research tasks https://github.com/trailofbits/dropkit

Nearly all of our 140 employees use Claude Code daily, and most in YOLO mode. Our devcontainer and dropkit are key linchpins for how we make this safer.

github.com
9
0
4
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago

"You can write exploits for software that exists in only one configuration that one company has. And you can do it on the fly." —CEO Dan Guido in The Verge on how AI collapses the cost of finding bugs. https://www.theverge.com/ai-artificial-intelligence/915660/mythos-script-kiddies-hackers-attack-cybersecurity-ai

Attack of the killer script kiddies
The Verge

Attack of the killer script kiddies

“It’s now or never. There’s a tidal wave coming.”

4
0
3
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 8mo ago

We open-sourced 17 Claude skills!

Think of Claude skills like Neo's uploads. Install a plugin, and Claude gains the capability in seconds. But we weren't satisfied with an AI plugin that vibes its way to an occasional bug. Our CEO and engineers built skills across the spectrum to see how far AI-assisted security can go.
https://github.com/trailofbits/skills

GitHub

GitHub - trailofbits/skills: Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows

Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows - trailofbits/skills

9
0
8
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago

When Claude reasons about code, it reasons about lists, but the questions that actually matter are graph questions.

We just open-sourced Trailmark, a library that parses source code into a call graph using tree-sitter and rustworkx across 17 languages.

8 Claude skills built on its API. On Ed448, one classified 73% of surviving mutants as equivalent. Flat lists can't see that. https://blog.trailofbits.com/2026/04/23/trailmark-turns-code-into-graphs/

Trailmark turns code into graphs
The Trail of Bits Blog

Trailmark turns code into graphs

Trailmark turns source code into a security-analysis graph, powering eight Claude Code skills for blast radius, taint propagation, and mutation test triage.

4
2
2
1
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago
Boosted by @cstross@wandering.shop
If you market a machine that “cooks for you,” a chef will never buy it. This is called identity threat, one of the four reasons why people resist adopting AI. Reframed: The machine doesn't cook for you. It makes you a faster, more efficient chef. Our CEO Dan Guido's full playbook on how we went from 95% resistance to 80-95% weekly Claude usage within a year: https://blog.trailofbits.com/2026/03/31/how-we-made-trail-of-bits-ai-native-so-far/
How we made Trail of Bits AI-native (so far)
The Trail of Bits Blog

How we made Trail of Bits AI-native (so far)

We had 5% buy-in and 95% resistance. A year later, AI-augmented auditors are finding 200 bugs a week on the right engagements. Here’s the six-part operating system we built, open sourced, and are giving away.

4
2
5
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago

30 readers took our C/C++ challenge. Some solved the Linux warmup, but nobody cracked the Windows driver bug. Even LLM-assisted submissions came up short.

The walkthrough explains both, including the Windows escalation from local DoS to kernel code execution.

Best 10 submissions are still getting swag. If you won, we'll be in contact.
https://blog.trailofbits.com/2026/05/05/c/c-checklist-challenges-solved/

blog.trailofbits.com
3
2
2
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 6mo ago

99.86% of 73K+ MBA expressions, simplified. No previous tool could handle all four types.

CoBRA is a new open-source tool that covers linear, semi-linear, polynomial, and mixed MBA obfuscation through 36 specialized passes managed by a worklist orchestrator.

For linear MBAs (the most common), it evaluates on Boolean inputs to fingerprint structure and reconstruct the simplest equivalent. Outputs verified via Z3 or random-input spot checks. https://blog.trailofbits.com/2026/04/03/simplifying-mba-obfuscation-with-cobra/

blog.trailofbits.com
4
0
1
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago

RE: @ostifofficial@fosstodon.org

libVLC powers VLC media player, which has been downloaded more than 6 billion times. Our audit produced structural improvements, not just bug fixes. HTTPS for self-update and build dependencies, three new fuzzing harnesses for URL, CSS, and JSON parsing. More in the report.

fosstodon.org
3
0
2
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago

The fastest way to get a team to adopt AI is to make them put in reps. We run hackathons as a forcing function.

2-3 day sprints, one objective. Last time, we told every engineer to use Claude Code in bypass permissions mode. It's now the default for our org.

The full playbook: https://blog.trailofbits.com/2026/03/31/how-we-made-trail-of-bits-ai-native-so-far/

How we made Trail of Bits AI-native (so far)
The Trail of Bits Blog

How we made Trail of Bits AI-native (so far)

We had 5% buy-in and 95% resistance. A year later, AI-augmented auditors are finding 200 bugs a week on the right engagements. Here’s the six-part operating system we built, open sourced, and are giving away.

3
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago

"Human plus LLM is vastly vastly better than either one alone."

Our Blockchain Engineering Director Ben Samuels explains why security auditors aren't going anywhere.

2
0
3
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 8mo ago

Our team had 375+ pull requests merged into 90+ open-source projects in 2025. From the Rust compiler to PyPI Warehouse to Sigstore, these contributions strengthen the infrastructure devs rely on daily.

Key contributions include:
* rekor-monitor is now production-ready with identity monitoring for Rekor v2
* 20+ Clippy lints merged, including implicit_clone improvements
* pyca/cryptography gained a new ASN.1 API
* PyPI Warehouse now supports project archival

https://blog.trailofbits.com/2026/01/30/celebrating-our-2025-open-source-contributions/

blog.trailofbits.com
4
0
1
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 8mo ago

New Trail of Bits skill: insecure-defaults
Detect insecure default configurations, hardcoded credentials, and fail-open security patterns. https://github.com/trailofbits/skills/tree/main/plugins/insecure-defaults

github.com
4
1
2
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 7mo ago

We open-sourced 10 new Claude Code skills from our internal repository.

Including:
agentic-actions-auditor finds security vulnerabilities in GitHub Actions workflows where attacker-controlled input reaches AI agents running with elevated CI permissions.

let-fate-decide draws Tarot cards using cryptographic randomness when your prompt is too vague for a real plan.

git-cleanup categorizes your accumulated branches and worktrees and walks you through safe deletion with gated confirmation.

https://github.com/trailofbits/skills/

GitHub

GitHub - trailofbits/skills: Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows

Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows - trailofbits/skills

3
0
1
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago

Most companies use AI to do the same work slightly faster. We call that level one adoption. Companies at level three do fundamentally different work. We're somewhere between level two and level three, and it took us a year to get there.

80-95% of our team use Claude weekly. We have 94 plugins containing 201 skills, 84 specialized agents, 29 commands, 125 scripts, and 414+ reference files encoding domain expertise.

The full six-step playbook we used to get there:
https://blog.trailofbits.com/2026/03/31/how-we-made-trail-of-bits-ai-native-so-far/

How we made Trail of Bits AI-native (so far)
The Trail of Bits Blog

How we made Trail of Bits AI-native (so far)

We had 5% buy-in and 95% resistance. A year later, AI-augmented auditors are finding 200 bugs a week on the right engagements. Here’s the six-part operating system we built, open sourced, and are giving away.

2
2
1
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 8mo ago

TEE security breaks down in predictable ways. In our December webinar, we showed exactly where.
Jules Drean from Tinfoil walked through their threat model, covering repositories, hardware configurations, and CVM images. Our security engineers, Paul Bottinelli and Tjaden Hess, dug into vulnerabilities they've found in production TEE deployments.

Watch the full recording: https://watch.getcontrast.io/register/trail-of-bits-top-tee-bugs-you-should-fix-before-your-audit?utm_source=socials

watch.getcontrast.io
3
0
5
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 7mo ago

How do you rebuild a security consultancy around AI without breaking what works? Our CEO, Dan Guido, talks systems, feedback loops, and what it actually takes to go AI-native at [un]prompted on March 4th at 9:10 AM https://unpromptedcon.org/

unpromptedcon.org
2
0
2
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 7mo ago

What if the compiler itself flagged your bugs? Blockchain Engineer, Kevin Valerio, is in Tokyo for SECCON 14 to show how Go’s IR can be modified to catch deterministic bug classes.
If you're attending, Kevin will present from 14:20-14:40 (GMT+9) https://www.seccon.jp/14/ep260228.html

SECCON14 電脳会議 2026.2.28(sat)-3.1(sun)
seccon.jp

SECCON14 電脳会議 2026.2.28(sat)-3.1(sun)

情報セキュリティをテーマに多様な競技を開催する情報セキュリティコンテスト SECCON。2026年2月28日(土)-3月1日(日)の2日間行われる「SECCON14 電脳会議」の情報ページです。

2
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago

We submitted SequenceHash to C2SP. It's a new cryptography spec that prevents a common class of bugs by safely combining multiple inputs into a single hash with any hash function.

Think TupleHash, generalized so it works on top of SHA-256, BLAKE2, or any underlying hash function. The draft is open for review on C2SP, part of our ongoing contributions to open cryptographic standards. https://c2sp.org/sequencehash

c2sp.org
1
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 8mo ago

Today's software signatures may not survive tomorrow's quantum computers.
Over the past two years, we collaborated with the Sigstore community to build controlled cryptographic agility into the ecosystem with a centralized algorithm registry, configurable restrictions, and Go implementations of post-quantum algorithms LMS and ML-DSA to prove it's future-ready. https://blog.trailofbits.com/2026/01/29/building-cryptographic-agility-into-sigstore/

blog.trailofbits.com
2
0
2
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago

Our sales team's AI Maturity Matrix. Scored from 0-3, defining what AI-enabled work looks like at each level.

Adoption is a ladder. Every team has clear levels, clear expectations, a clear path up, and real consequences for staying stuck.

Every org's matrix should look different. Copy the system, not the specifics.
https://blog.trailofbits.com/2026/03/31/how-we-made-trail-of-bits-ai-native-so-far/

How we made Trail of Bits AI-native (so far)
The Trail of Bits Blog

How we made Trail of Bits AI-native (so far)

We had 5% buy-in and 95% resistance. A year later, AI-augmented auditors are finding 200 bugs a week on the right engagements. Here’s the six-part operating system we built, open sourced, and are giving away.

1
1
1
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 6mo ago

We saw high coverage mask a fund-draining vulnerability, and caught it with mutation testing. We built the tools to make this routine.

MuTON and mewt introduce bugs, run tests, and find what coverage misses. MuTON supports TON languages. mewt covers Solidity, Rust, Go, and more.
https://blog.trailofbits.com/2026/04/01/mutation-testing-for-the-agentic-era/

blog.trailofbits.com
1
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 6mo ago

Adding token A to token B in a DeFi formula is as meaningless as adding meters to seconds. Different dimensions, meaningless result.

Physicists learn this on day one. Smart contract developers rarely think about it, but the same rules apply to on-chain arithmetic.

During an audit, we caught a function passing decimals where assets were expected. Dimensional analysis spotted it instantly. https://blog.trailofbits.com/2026/03/24/spotting-issues-in-defi-with-dimensional-analysis/

blog.trailofbits.com
1
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 7mo ago

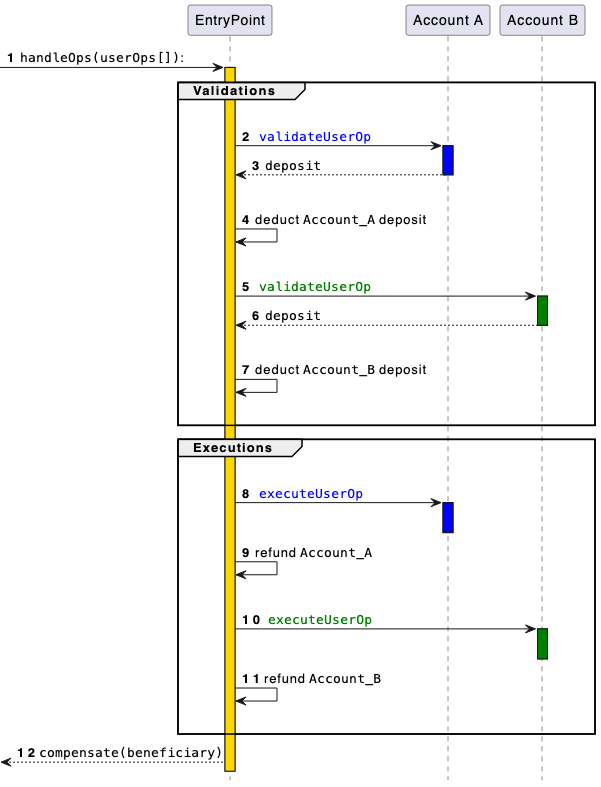
A single bug in an ERC-4337 smart account can be as catastrophic as leaking a private key.

We've audited dozens of smart accounts and found six vulnerability patterns that consistently reappear across codebases.

If you're working with smart accounts, each pattern includes safe code examples so you can reference them for your own implementation: https://blog.trailofbits.com/2026/03/11/six-mistakes-in-erc-4337-smart-accounts/

Six mistakes in ERC-4337 smart accounts
The Trail of Bits Blog

Six mistakes in ERC-4337 smart accounts

After auditing dozens of ERC‑4337 smart accounts, we’ve identified six vulnerability patterns that frequently appear.

1
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 7mo ago

We're sponsoring RE//verse in Orlando this week. Sam Sharps, Kyle Elliott, and Julius Alexandre will be there. Come find them if you want to talk reverse engineering or binary analysis. https://re-verse.io/

re-verse.io
1
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 2mo ago
Every Rust bug we submitted through Patch the Planet came from one engineer who ran a variant-analysis pipeline using Codex's /goal. A separate discovery run uncovered two potential high-severity privilege-escalation bugs in Keycloak's SAML component. Over the past few weeks, our engineers independently converged on three techniques that get the most out of /goal. We wrote them down, with prompts included: https://blog.trailofbits.com/2026/07/28/how-we-use-goal-to-find-bugs-in-patch-the-planet/#infosec #rustlang #llm
blog.trailofbits.com
0
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 3mo ago
1.2 billion downloads ran through pyca/cryptography last month. Nearly every Python app that touches crypto depends on it. If it doesn't ship post-quantum primitives, the Python ecosystem can't migrate. We helped add ML-DSA (FIPS 204) for signatures and ML-KEM (FIPS 203) for key exchange to the library. Install and migration details in the blog. https://blog.trailofbits.com/2026/06/30/shipping-post-quantum-cryptography-to-python/
Shipping post-quantum cryptography to Python
The Trail of Bits Blog

Shipping post-quantum cryptography to Python

We added post-quantum cryptography support to pyca/cryptography, the eleventh most-downloaded Python package on PyPI, putting quantum-resistant ML-KEM and ML-DSA algorithms one pip install away for the entire Python ecosystem.

0
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 5mo ago

libFuzzer is in maintenance mode. We added LibAFL support to Ruzzy so Ruby devs and security researchers can run their next fuzzing campaign without harness modifications.

Adding LibAFL support to Ruzzy took longer than expected. We took detours in ELF file internals, .init_array DSO sections, SanitizerCoverage interceptors, lazy vs. eager loading, and Ruby C extensions. https://blog.trailofbits.com/2026/04/29/extending-ruzzy-with-libafl/

blog.trailofbits.com
0
1
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 2mo ago
Agentic AI headlines Black Hat's keynotes and DEF CON's main stage next week, and it's a topic we've been researching for years. We've hijacked multi-agent systems with one web page, pulled Gmail data from Perplexity's Comet via prompt injection, and built image-scaling attacks invisible to humans but not models. All documented on blog.trailofbits.com. We'll be in Vegas Aug 4-6. If you're around, we'd love to chat: https://meetings.hubspot.com/trailofbits/blackhat-defcon-scheduling #infosec #aisecurity
meetings.hubspot.com
0
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 2mo ago
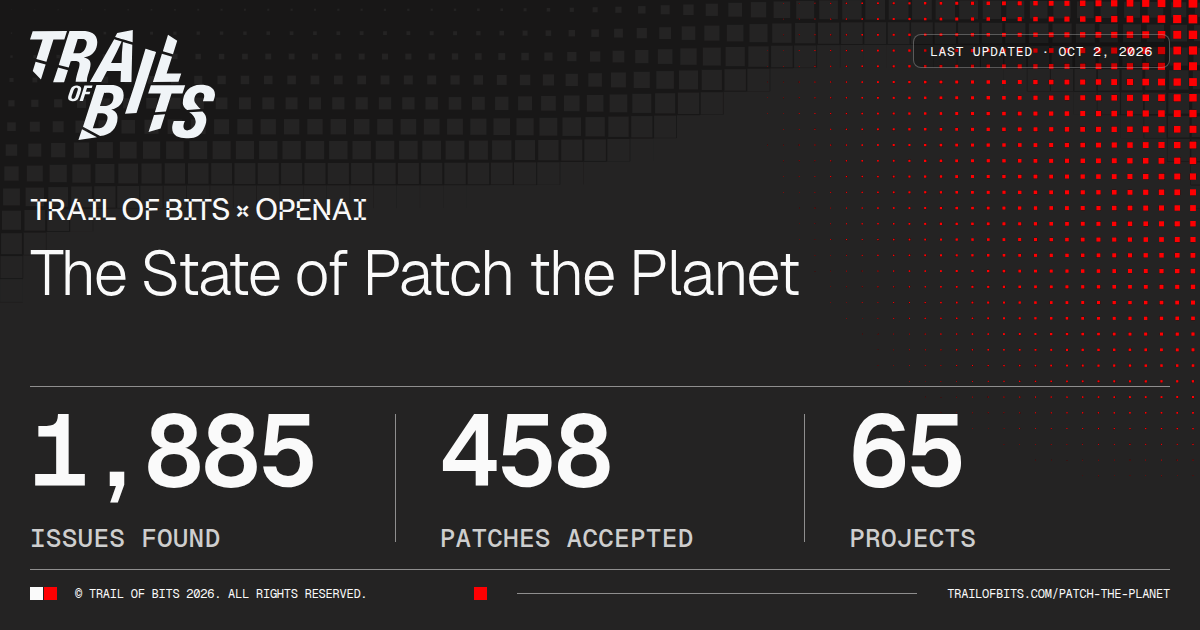
Patch the Planet update: 1,137 issues found (+279 since July 20), 866 awaiting a patch, 125 fixes open upstream, 146 merged across 46 open-source projects. https://trailofbits.com/patch-the-planet/dashboard/ #infosec #opensource
Dashboard · Patch the Planet · Trail of Bits
Trail of Bits

Dashboard · Patch the Planet · Trail of Bits

Live view of the Patch the Planet initiative: issues identified, patches shipped, and projects onboarded.

0
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 1w ago
MPC inside a Trusted Execution Environment (TEE) adds defense in depth, but the two make different bets on trust. MPC spreads trust across independent parties, while TEEs concentrate it in the hardware manufacturer and its attestation infrastructure. Our new post covers what TEE attestation can and can't fix in MPC deployments, the pitfalls we see most often in audits, and how to combine the two without undermining either. https://blog.trailofbits.com/2026/09/25/dont-let-tees-break-your-mpc/ #infosec #cryptography #TEE
Don
The Trail of Bits Blog

Don

Combining threshold signature schemes with trusted execution environments (TEEs) can strengthen MPC deployments, as long as you treat the TEE as a defense-in-depth layer rather than a substitute for a sound protocol.

0
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 7mo ago

Today at 12:55 PM MT on the Future Llama stage at ETH Denver, our CEO, Dan Guido, opens the hood on how he made Trail of Bits AI-native.

0
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 2mo ago
858 potential bugs found, 595 awaiting patches, 120 fixes open upstream, 143 merged. Patch the Planet's latest numbers are now on a public dashboard that covers 41 codebases, including curl, OpenSSL, Keycloak, containerd, and kubernetes-client. The 13 CVEs assigned so far include a high-severity nginx bug (CVE-2026-42530) and findings in curl, aiohttp, go-jose, and cryptography. Every accepted fix links to its upstream PR. https://trailofbits.com/patch-the-planet/dashboard #opensource #security
Dashboard · Patch the Planet · Trail of Bits
Trail of Bits

Dashboard · Patch the Planet · Trail of Bits

Live view of the Patch the Planet initiative: issues identified, patches shipped, and projects onboarded.

0
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 3mo ago
Mewt grades your test suite by sabotaging your code. Each change that doesn't get flagged by your tests is a potential bug. Today we're expanding it to support DAML, Canton Networks' native language, with two new mutant classes for its authorization rules: controller party swap and removal. When we tried Mewt on OpenZeppelin's canton-stablecoin reference implementation, all tests were green and coverage was 100%, but four surviving mutants exposed missing test cases. https://blog.trailofbits.com/2026/07/08/mutation-testing-comes-to-daml/
Mutation testing comes to DAML
The Trail of Bits Blog

Mutation testing comes to DAML

In April we released Mewt, our open-source mutation-testing engine that finds the gaps in your test suite. Today we’re expanding it with support for DAML, the language Canton Network applications are written in.

0
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 7mo ago

We're hiring a senior technical recruiter who can own the full hiring lifecycle and build a talent pipeline. You thrive on personal connections with a knack for evaluating technical candidates across engineering and non-engineering roles.

0
0
0
0
Open post
Trail of Bits @trailofbits@infosec.exchange
· 2mo ago
What we’ve learned about testing Rust for security, now available as a Testing Handbook chapter. Inside, you'll find what Rust's guarantees don't cover, undefined behavior with Miri, property testing with proptest, Clippy lints, memory zeroization, and model checking with Kani. We also released rust-review, a Claude Code plugin for automated Rust security reviews co-built with Aptos Labs. https://blog.trailofbits.com/2026/07/13/rust-proof-your-code-with-our-new-testing-handbook-chapter/ #Rust #infosec #appsec
Rust-proof your code with our new Testing Handbook chapter
The Trail of Bits Blog

Rust-proof your code with our new Testing Handbook chapter

We’ve added a new chapter to our Testing Handbook: a comprehensive guide to security testing Rust programs.

0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 21:42:53 UTC