Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

TechNadu

@technadu@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Uncovering #Cybersecurity | Expert insights, Pro Interviews, Latest Threats & Hacking News | #InfoSec #Malware #Ransomware #Streaming #TechNews

182 Followers
30 Following
50 Posts
Joined March 18, 2025
Website::
https://www.technadu.com/
X (Twitter):
https://x.com/TechNadu
LinkedIn:
https://www.linkedin.com/company/technadu/
Facebook:
https://www.facebook.com/TechNadu
Bluesky:
https://bsky.app/profile/technadu.com
YouTube:
https://www.youtube.com/c/technadu
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

UK online safety law raises concerns.
• Privacy risks from age verification
• Expanded govt powers
• Possible VPN restrictions

https://www.technadu.com/uk-online-safety-law-concerns-raise-privacy-debate/627353/

Safety vs privacy - your take?
#InfoSec #Privacy #CyberSecurity

UK Urged to Rethink Online Safety Law Over Fears of Privacy and Internet Restrictions
TechNadu

UK Urged to Rethink Online Safety Law Over Fears of Privacy and Internet Restrictions

UK online safety law concerns grow as groups warn of privacy risks, VPN limits, and wider impact on internet access and user rights.

2
0
3
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

Russia’s VPN crackdown is now impacting core services ⚠️
• Banking outages
• E-commerce disruptions
• Messaging app restrictions
• Govt systems affected
DPI filtering causing unintended traffic blocks.

https://www.technadu.com/russia-vpn-crackdown-impacts-banking-and-online-services/627170/

#Cybersecurity #VPN #InternetPolicy

Russia’s Expanding VPN Restrictions Begin to Affect Core Digital Services
TechNadu

Russia’s Expanding VPN Restrictions Begin to Affect Core Digital Services

Russia VPN crackdown disrupts banking ecommerce and public services as restrictions expand causing outages and economic losses.

2
0
1
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

More than 185,000 accounts were reportedly exposed in a 7-Eleven breach tied to the ShinyHunters extortion campaign.
Leaked records included emails, DOBs, addresses & phone numbers connected to franchisee systems.

https://www.technadu.com/7-eleven-data-breach-exposes-over-185000-accounts-in-shinyhunters-extortion-campaign/628347/

#Cybersecurity #DataBreach #ShinyHunters

7-Eleven Data Breach Exposes Over 185,000 Accounts in ShinyHunters Extortion Campaign
TechNadu

7-Eleven Data Breach Exposes Over 185,000 Accounts in ShinyHunters Extortion Campaign

7-Eleven experienced a data breach exposing 185,300 accounts after a pay or leak extortion campaign by ShinyHunters targeted systems storing franchisee documents.

1
2
1
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

X-VPN has joined the VPN Trust Initiative (VTI) and i2Coalition to support stronger privacy, transparency, and security standards across the VPN industry.

The company says the memberships will help align with evolving best practices and safer internet initiatives.

https://www.technadu.com/x-vpn-joins-vpn-trust-initiative-and-i2coalition/628327/

#VPN #Cybersecurity #Privacy

X-VPN Joins VPN Trust Initiative and i2Coalition to Strengthen Privacy and Security Efforts
TechNadu

X-VPN Joins VPN Trust Initiative and i2Coalition to Strengthen Privacy and Security Efforts

X-VPN joins VPN Trust Initiative and i2Coalition to support stronger privacy, security, and transparency standards online.

1
0
1
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Black Lotus Labs identified “Showboat,” a Linux post-exploitation framework tied to PRC-aligned telecom targeting campaigns.

Researchers say the malware enabled persistence, proxying, remote shell execution, and maintained a 0% VirusTotal detection rate for months.

https://www.technadu.com/showboat-a-novel-linux-post-exploitation-framework-targeting-telecommunications/628291/

#Cybersecurity #Linux #Malware #ThreatIntel

Showboat: A Novel Linux Post-Exploitation Framework Targeting Telecommunications
TechNadu

Showboat: A Novel Linux Post-Exploitation Framework Targeting Telecommunications

Showboat is a novel Linux post-exploitation framework utilized by PRC-aligned actors to target global telecommunications providers.

1
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Researchers say deleted Google API keys may stay active for up to 23 minutes due to cloud propagation delays.

The issue could reportedly allow continued access to Gemini uploads, APIs, and cloud resources after key deletion.

https://www.technadu.com/google-api-keys-remain-usable-after-deletion-for-up-to-23-minutes-report-says/628304/

#Cybersecurity #CloudSecurity #GoogleCloud #APIKeys

Google API Keys Remain Usable After Deletion for up to 23 Minutes, Report Says
TechNadu

Google API Keys Remain Usable After Deletion for up to 23 Minutes, Report Says

Security researchers at Aikido found that deleted Google API keys remain active for up to 23 minutes, exposing Gemini files, BigQuery data, and risking fraudulent charges.

1
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

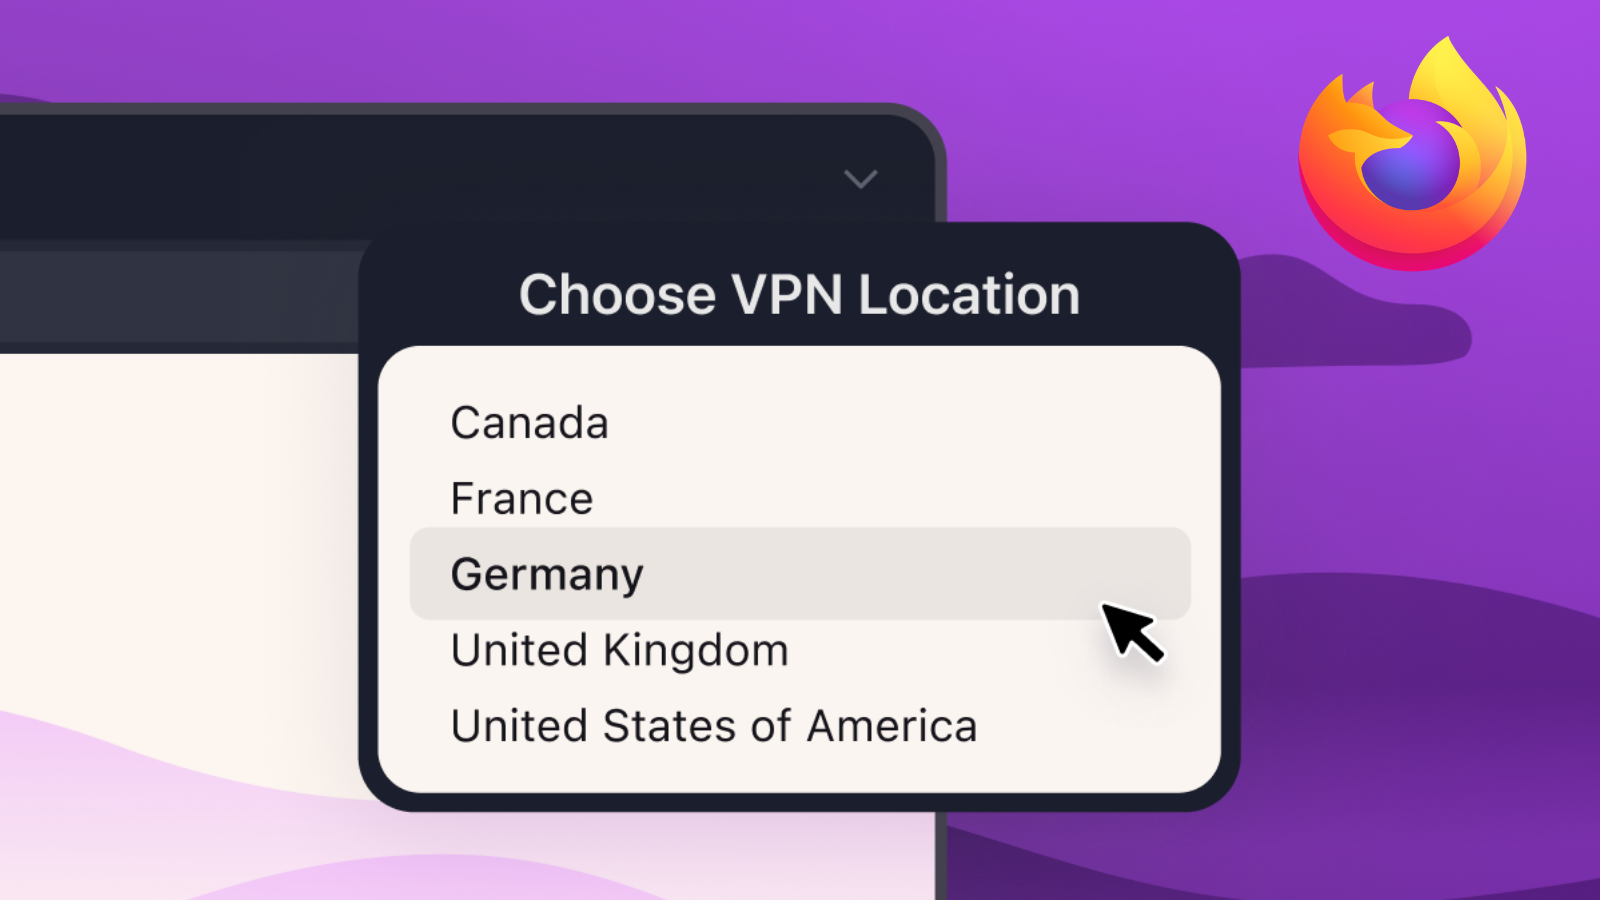
Mozilla expanded Firefox’s free built-in VPN with selectable servers in 5 countries and new mobile privacy features in Firefox 151.

The free VPN has reportedly crossed 1 million sign-ups since launch.

https://www.technadu.com/firefox-free-vpn-expansion-adds-more-global-servers/628281/

#Firefox #VPN #Privacy #Cybersecurity

Firefox Expands Its Free VPN With More Server Locations and New Mobile Features
TechNadu

Firefox Expands Its Free VPN With More Server Locations and New Mobile Features

Firefox free VPN expansion adds selectable servers, mobile features, and broader regional support in Firefox 151 update.

1
0
1
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Mullvad is rolling out fixes for a VPN fingerprinting issue that could let websites associate activity across different VPN servers through exit IP assignment patterns.

Users switching servers are advised to re-log to regenerate WireGuard keys and internal IPs.

https://www.technadu.com/mullvad-fingerprinting-issue-prompts-vpn-system-changes/628269/

#VPN #Privacy #Cybersecurity #Mullvad

Mullvad Addresses VPN Server Fingerprinting Issue That Could Link User Activity Across Servers
TechNadu

Mullvad Addresses VPN Server Fingerprinting Issue That Could Link User Activity Across Servers

Mullvad fingerprinting issue could link activity across VPN servers; provider testing new exit IP assignment protections for users.

1
0
1
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Fortinet patched two critical RCE flaws affecting FortiAuthenticator and FortiSandbox.

The vulnerabilities could allow unauthenticated command execution on exposed systems.

https://www.technadu.com/fortinet-patches-critical-rce-vulnerabilities-in-fortisandbox-and-fortiauthenticator/627847/

#CyberSecurity #Fortinet #RCE #Infosec

Fortinet Patches Critical RCE Vulnerabilities in FortiSandbox and FortiAuthenticator
TechNadu

Fortinet Patches Critical RCE Vulnerabilities in FortiSandbox and FortiAuthenticator

Fortinet released security updates for critical RCE vulnerabilities CVE-2026-44277 and CVE-2026-26083 affecting FortiAuthenticator and FortiSandbox systems.

1
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Red Hat warns that autonomous AI agents are becoming “high-privilege users that never sleep.”

As AI systems gain direct access to APIs, databases, and cloud infrastructure, security teams may face faster vulnerability discovery, unintended autonomous actions, and shrinking response windows.

https://www.technadu.com/the-risks-of-ai-agents-as-high-privilege-users-that-never-pause/627824/

#AI #CyberSecurity #InfoSec #AIAgents

The Risks of AI Agents as High-Privilege Users That Never Pause
TechNadu

The Risks of AI Agents as High-Privilege Users That Never Pause

AI agents are evolving into autonomous infrastructure actors, changing how defenders approach runtime security, risk, and privilege control.

1
0
3
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

A U.K. water utility reportedly failed to detect attackers inside its network for nearly 2 years before a Cl0p-linked ransomware breach was uncovered.

Source: Source: https://therecord.media/uk-water-company-had-hackers-lurking-for-years

The incident exposed major gaps in OT, monitoring, patching, and critical infrastructure security.
Follow @technadu@infosec.exchange

#CyberSecurity #OTSecurity #InfoSec

UK water company allowed hackers to lurk undetected for nearly two years, regulator finds
therecord.media

UK water company allowed hackers to lurk undetected for nearly two years, regulator finds

The Information Commissioner's Office (ICO) fined South Staffordshire Water £963,900 ($1.3 million) on Monday over an attack by the Cl0p ransomware group that led to the personal data of 633,887 customers and employees being published in August 2022.

1
2
2
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Google researchers say they identified the first potentially AI-generated zero-day exploit used by cybercriminals.

The exploit reportedly bypassed 2FA via a semantic logic flaw in a web admin tool.
AI-driven offensive operations are evolving rapidly.

https://www.technadu.com/google-detects-first-potentially-ai-generated-zero-day-exploit/627772/

#CyberSecurity #AI #ZeroDay #ThreatIntel

Google Detects First Potentially AI-Generated Zero-Day Exploit
TechNadu

Google Detects First Potentially AI-Generated Zero-Day Exploit

Google Threat Intelligence Group details how adversaries leverage AI for zero-day exploits, including a two-factor authentication bypass.

1
0
1
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

Attackers are abusing Google Ads and legitimate Claude.ai shared chats to spread macOS malware.
• Fake install guides
• Malicious Terminal commands
• MacSync infostealer deployed
• Browser creds & Keychain targeted

https://www.technadu.com/google-ads-and-claude-ai-shared-chats-abused-to-distribute-mac-malware/627723/

#InfoSec #CyberSecurity #macOS

Google Ads and Claude.ai Shared Chats Abused to Distribute Mac Malware
TechNadu

Google Ads and Claude.ai Shared Chats Abused to Distribute Mac Malware

Attackers are abusing Google Ads and legitimate Claude.ai shared chats to trick users into executing MacSync infostealers and other macOS malware.

1
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

Unoaerre confirmed a ransomware attack disrupting manufacturing operations.

• €3.8M ransom reportedly demanded
• Manufacturing plant evacuated
• IT systems isolated
• Data exposure investigation ongoing

https://www.technadu.com/unoaerre-ransomware-attack-disrupts-manufacturing-operations/627708/

Are manufacturing firms becoming prime ransomware targets?
#InfoSec #CyberSecurity #Ransomware

Unoaerre Ransomware Attack Disrupts Manufacturing Operations
TechNadu

Unoaerre Ransomware Attack Disrupts Manufacturing Operations

Italian jewelry manufacturer Unoaerre suffered a ransomware attack on May 10, 2026. The company refused a €3.8 million ransom as IT restoration continues.

1
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

AI dictation tools and vibe coding platforms are changing office culture fast.

Some startup leaders say future workplaces may sound “more like a sales floor” as employees increasingly talk to AI assistants instead of typing.

Would you work in a voice-first office?

Source: https://techcrunch.com/2026/05/10/get-ready-for-the-whisper-filled-office-of-the-future/

Follow @technadu@infosec.exchange for more AI updates.

#AI #FutureOfWork #TechNews

Get ready for the whisper-filled office of the future | TechCrunch
TechCrunch

Get ready for the whisper-filled office of the future | TechCrunch

How will work setups change if we spend more and more time talking to our computers?

1
0
2
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

European Commission rolls out age verification
Anonymous + ID-based
Security vs privacy debate

Source: https://commission.europa.eu/news-and-media/news/european-age-verification-app-keep-children-safe-online-2026-04-15_en

💬 Thoughts?

Follow TechNadu

#InfoSec #Privacy

European age verification app to keep children safe online
European Commission

European age verification app to keep children safe online

The European Commission President announced that the new European age verification app is technically ready and will soon be available for citizens to use.

1
1
2
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

AI is creating “ghost breaches”
• Fake incidents
• Real responses
• No compromise
Risk = narrative-driven
SOC + Comms must align

Source: https://cyberscoop.com/ai-generated-breach-narratives-ghost-threat-vector-op-ed/
💬 Thoughts?
Follow TechNadu
#InfoSec #CyberSecurity #AI

Ghost breaches: How AI-mediated narratives have become a new threat vector
CyberScoop

Ghost breaches: How AI-mediated narratives have become a new threat vector

Think your company is secure? A "ghost breach" says otherwise. Discover how AI-mediated narratives are fabricating realistic data leaks, forcing firms into high-stakes crisis responses for incidents that never happened.

1
0
1
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

IPVanish expanded its VPN network to 150+ global server locations with over 3,400 servers and nearly 1,000 RAM-only servers across 25 locations.

The provider says it aims to transition to a fully RAM-only infrastructure by 2027.

https://www.technadu.com/ipvanish-vpn-network-expands-beyond-150-locations/628264/

#VPN #Cybersecurity #Privacy #InfoSec

IPVanish Expands Global VPN Network to More Than 150 Server Locations
TechNadu

IPVanish Expands Global VPN Network to More Than 150 Server Locations

IPVanish VPN Network now spans 150+ locations worldwide with 3,400 servers, RAM-only infrastructure, and expanded capacity.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

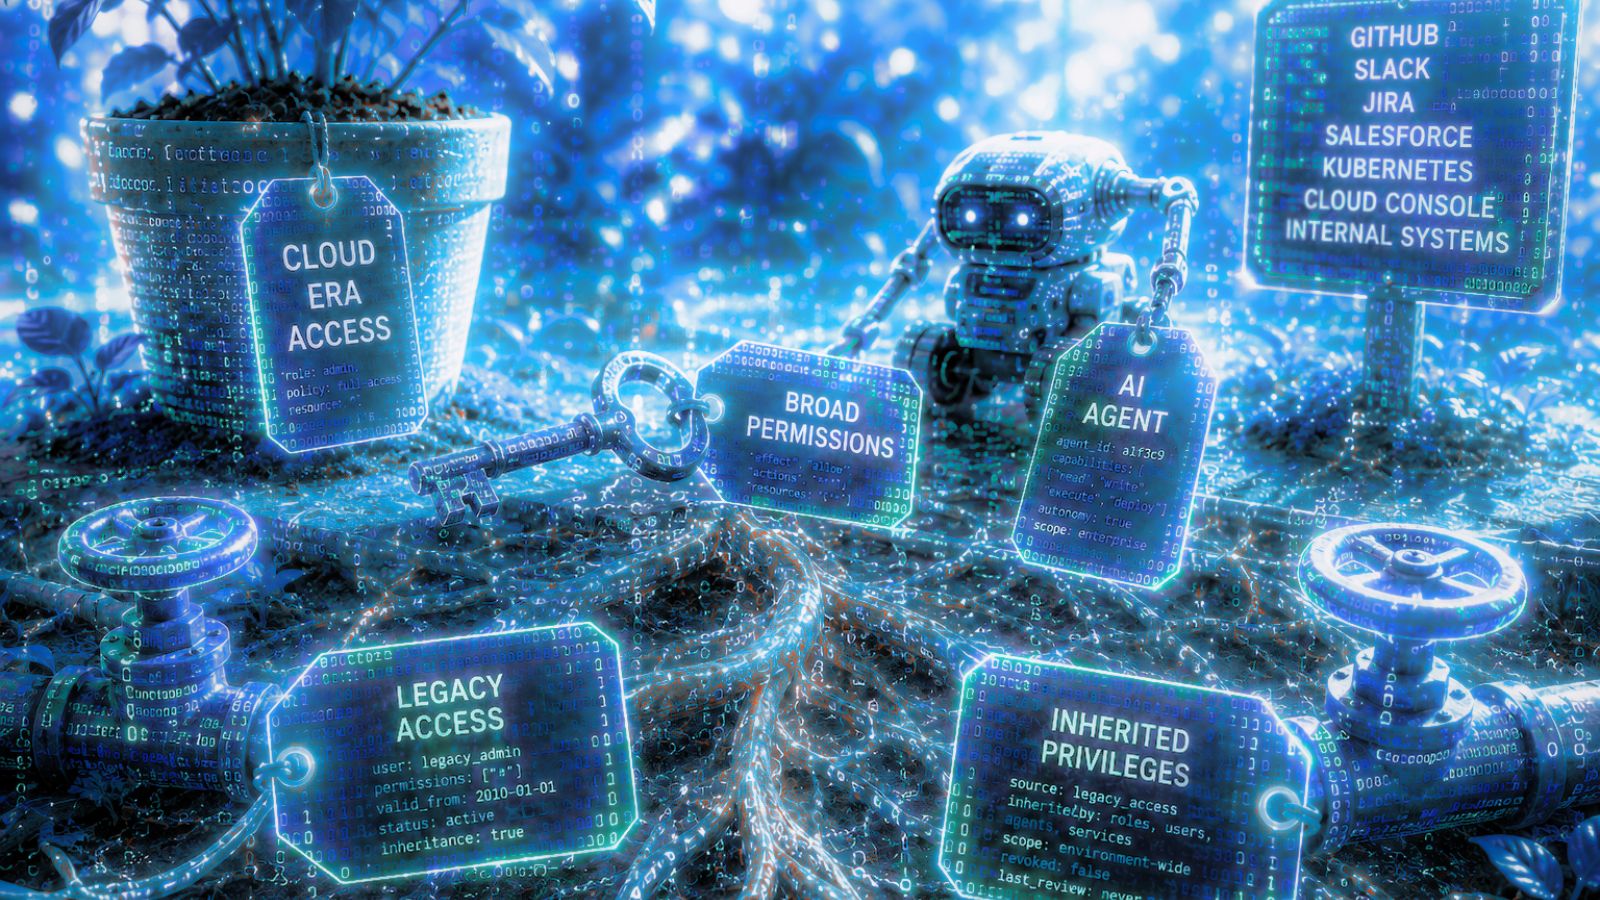
Shashwat Sehgal, CEO & Co-Founder of P0 Security, warns that AI agents are recreating the same access problems that broke early cloud security.

🔐 Broad standing permissions are returning
🔐 Visibility alone does not reduce blast radius
🔐 Runtime governance matters more than authentication

“The organizations that avoid repeating the cloud security cycle will be the ones that treat agents as a new class of privileged non-human identity from day one.”

https://www.technadu.com/ai-agents-are-recreating-the-access-problems-that-broke-early-cloud-security/628330/

#Cybersecurity #AISecurity #IdentitySecurity #CloudSecurity #AIAgents

AI Agents are Recreating the Access Problems that Broke Early Cloud Security
TechNadu

AI Agents are Recreating the Access Problems that Broke Early Cloud Security

AI agents are recreating early cloud-era access control problems as enterprises grant broad permissions across GitHub, Slack, and internal systems.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

Taiwan’s train cyber incident is putting legacy wireless infrastructure under the spotlight.

Reports suggest replay attacks and low-cost SDR tools may have contributed to the disruption.

Source: https://www.theregister.com/security/2026/05/11/taiwans-train-cyber-trauma-reveals-a-global-system-thats-coming-off-the-tracks/5237248

Critical infrastructure modernization can’t wait.
Follow @technadu@infosec.exchange for more.

#CyberSecurity #CriticalInfrastructure #SDR

theregister.com

Are we human?

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

Operation PowerOFF 🚨
• 53 domains seized
• 75K+ users targeted
• 3M+ accounts exposed

Global DDoS crackdown 👇
https://www.technadu.com/europol-ddos-crackdown-operation-poweroff-dismantles-over-50-domains-targets-75000-criminals-worldwide-secures-4-arrests/626025/

#Infosec #Cybersecurity #DDoS

Europol DDoS Crackdown: Operation PowerOFF Dismantles Over 50 Domains, Targets 75,000 Criminals Worldwide, Secures 4 Arrests
TechNadu

Europol DDoS Crackdown: Operation PowerOFF Dismantles Over 50 Domains, Targets 75,000 Criminals Worldwide, Secures 4 Arrests

Operation PowerOFF, a major Europol DDoS crackdown, dismantled DDoS-for-hire services and targeted 75,000 criminal users worldwide.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago
Replying to
@ghostsarespooky@infosec.exchange The irony isn't lost on us! True decentralization is the goal, but current relay dependencies mean the network still has "central" targets for DDoS attacks. It’s a major hurdle the team needs to clear for the protocol's credibility.
0
1
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Researchers allege Russia’s MAX messaging app may include VPN detection and surveillance-related capabilities.

RKS Global says multiple claims were supported through static code analysis, while MAX denies the accusations.

https://www.technadu.com/max-app-surveillance-claims-russia/628268/

#Cybersecurity #Privacy #VPN #Infosec

Russian Researcher Alleges MAX App Includes Surveillance Features, VPN Detection Capabilities
TechNadu

Russian Researcher Alleges MAX App Includes Surveillance Features, VPN Detection Capabilities

MAX app surveillance claims spark privacy concerns after researchers allege VPN detection, message monitoring, and data access features.

0
0
1
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Canada’s proposed Bill C-22 is drawing strong responses from VPN providers.

▪️ Windscribe may relocate HQ
▪️ Surfshark may leave the Canadian market
▪️ ExpressVPN calls encryption “non-negotiable”
▪️ NordVPN warns mandated access creates exploitable vulnerabilities

Full responses from providers:
https://www.technadu.com/canadas-bill-c-22-vpn-providers-discuss-privacy-encryption-user-impact/628316/

#CyberSecurity #VPN #Privacy #Encryption #BillC22

Canada’s Bill C-22 Raises Privacy Concerns - VPN Providers Respond
TechNadu

Canada’s Bill C-22 Raises Privacy Concerns - VPN Providers Respond

We asked NordVPN, ExpressVPN, Surfshark, IPVanish, Windscribe and other VPN providers about Canada’s proposed Bill C-22, its impact on user privacy, and what they would do if the bill becomes law.

0
1
4
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

Cyber → Physical theft is scaling
• Load board compromise
• RMM persistence
• Signed malware
• Financial + cargo targeting
$6.6B losses in 2025
Supply chain = high-value attack surface

Source: https://therecord.media/cargo-thieving-hackers-running-sophisticated-campaigns

💬 Thoughts
Follow @technadu@infosec.exchange

#InfoSec #CyberSecurity #SupplyChain

Cargo thieving hackers running sophisticated remote access campaigns, researchers find
therecord.media

Cargo thieving hackers running sophisticated remote access campaigns, researchers find

Losses from cargo theft in North America rose to $6.6 billion in 2025, driven largely by digital attacks, according to the fleet management company Geotab.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Instructure confirmed it paid a ransom to ShinyHunters after the Canvas cyberattack allegedly exposed data tied to 9,000 customers.

The incident triggered FBI warnings and a congressional investigation.

https://www.technadu.com/canvas-cyberattack-instructure-pays-shinyhunters-ransom-us-house-committee-asks-for-investigation/627843/

#CyberSecurity #Ransomware #Canvas #Infosec

Canvas Cyberattack: Instructure Pays ShinyHunters Ransom, US House Committee Asks for Investigation
TechNadu

Canvas Cyberattack: Instructure Pays ShinyHunters Ransom, US House Committee Asks for Investigation

Instructure paid a ransom to ShinyHunters after a Canvas platform data breach. Congress has announced an investigation into the incident affecting 9,000 customers.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

CloudBees survey findings:
• 81% saw more production issues tied to AI-generated code
• 67% reported increased code volume
• 54% saw higher CI/CD costs
AI adoption is accelerating, but governance and validation still appear to lag behind.
Are organizations prioritizing speed over software quality?

Source: https://devops.com/cloudbees-survey-surfaces-increase-in-production-issues-attributable-to-ai/

Follow @technadu@infosec.exchange for more cybersecurity and DevOps updates.

#AI #DevOps #CloudBees #Cybersecurity

CloudBees Survey Surfaces Increase in Production Issues Attributable to AI - DevOps.com
DevOps.com

CloudBees Survey Surfaces Increase in Production Issues Attributable to AI - DevOps.com

AI in DevOps is a double-edged sword: A new CloudBees survey finds 93% of IT leaders see productivity gains from AI, but a massive 81% report an increase in production issues due to AI-generated code. Find out more here.

0
0
1
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

Bluesky hit by DDoS
• No breach
• No data loss
• Major disruption
Availability = attack surface

Source: https://techcrunch.com/2026/04/17/its-not-just-you-bluesky-is-sorta-down/

💬 Thoughts?
Follow TechNadu

#InfoSec #DDoS

Bluesky confirms DDoS attack is cause of continued app outages | TechCrunch
TechCrunch

Bluesky confirms DDoS attack is cause of continued app outages | TechCrunch

Bluesky has been experiencing ongoing service disruptions since just before 3 a.m. ET on April 15.

0
3
0
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

Canvas outages linked to a cyberattack reportedly forced universities across the U.S. to delay final exams.

ShinyHunters claimed responsibility after allegedly breaching Instructure again.

Source: https://therecord.media/universities-forced-to-reschedule-exams-canvas-incident.
Education platforms remain high-value cyber targets.

Follow @technadu@infosec.exchange
#CyberSecurity #InfoSec #DataBreach

Multiple universities forced to reschedule final exams after Canvas cyber incident
therecord.media

Multiple universities forced to reschedule final exams after Canvas cyber incident

On Thursday, dozens of students took to social media to say they saw a message from a cybercriminal group as they navigated through Canvas, an educational platform created by Instructure that hosts teaching materials, tests, readings and more.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

Third-party breach hits Inditex 🚨
• Transaction data accessed
• Vendor compromised
• No financial data exposed

More 👇
https://www.technadu.com/zara-parent-company-inditex-reports-third-party-data-breach-affecting-transactions-database/626036/

#Infosec #Cybersecurity

Zara Parent Company Inditex Reports Third-Party Data Breach Affecting Transactions Database
TechNadu

Zara Parent Company Inditex Reports Third-Party Data Breach Affecting Transactions Database

Zara owner Inditex confirmed a data breach stemming from a third-party technology provider, which affects customer transactions.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Kaspersky’s 2026 ransomware report shows attacks declining in volume, but threat actors are becoming more sophisticated.

EDR killers, BYOVD tactics, credential theft, and encryptionless extortion are becoming more common, while post-quantum cryptography is entering ransomware workflows.

https://www.technadu.com/kaspersky-2026-ransomware-report-details-shifting-threats-as-attacks-decline-and-tactics-change/627813/

#InfoSec #Ransomware #CyberSecurity #ThreatIntel

Kaspersky 2026 Ransomware Report Details Shifting Threats, as Attacks Decline and Tactics Change
TechNadu

Kaspersky 2026 Ransomware Report Details Shifting Threats, as Attacks Decline and Tactics Change

Kaspersky's 2026 report details the rise of encryptionless extortion, post-quantum cryptography, and EDR killers among leading ransomware threat groups.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

New KEV added 🚨
CVE-2026-34197 (Apache ActiveMQ)
• Active exploitation confirmed
• High-risk entry point
KEV = patch now, not later

Source: https://www.cisa.gov/news-events/alerts/2026/04/16/cisa-adds-one-known-exploited-vulnerability-catalog

💬 How fast is your patch cycle?
Follow @technadu@infosec.exchange

#InfoSec #CyberSecurity #KEV

Cybersecurity and Infrastructure Security Agency CISA

CISA Adds One Known Exploited Vulnerability to Catalog | CISA

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

Grinex hit by $13M cyberattack 🚨
• Operations suspended
• State actor suspected
• Sanctions-linked

More 👇
https://www.technadu.com/grinex-crypto-exchange-announced-cyberattack-resulting-in-13-million-theft/626091/

#Infosec #Crypto

Grinex Crypto Exchange Announced Cyberattack Resulting in $13 Million Theft
TechNadu

Grinex Crypto Exchange Announced Cyberattack Resulting in $13 Million Theft

A severe Grinex crypto exchange cyberattack resulted in a $13.10 million theft, highlighting escalating financial cybersecurity risks for sanctioned platforms.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

CyberArk + Palo Alto Networks launch Idira for AI-era identity security. 🔐

The platform focuses on securing human, machine & agentic identities with unified PAM and governance.

Is identity becoming the primary AI attack surface?

Follow @technadu@infosec.exchange for more.

#CyberSecurity #IdentitySecurity #AI

0
0
1
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

Kingdom Market admin Alan Bill received a 16+ year sentence after pleading guilty to helping operate a major darknet marketplace tied to narcotics, malware, stolen data, fake IDs, and crypto transactions.

Another major international darknet takedown.

Source: https://therecord.media/kingdom-market-administrator-gets-16-year-sentence

Follow @technadu@infosec.exchange

#CyberSecurity #DarkWeb #InfoSec

Kingdom Market administrator given 16-year sentence
therecord.media

Kingdom Market administrator given 16-year sentence

Slovakian national Alan Bill, 33, pleaded guilty in January to a conspiracy to distribute controlled substances charge after admitting to his role in running Kingdom Market — a platform used by drug dealers and cybercriminals between March 2021 and December 2023.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

A malicious Checkmarx Jenkins AST plugin was reportedly deployed using credentials stolen in the Trivy supply-chain attack.

The rogue plugin bypassed the normal release pipeline and contained credential-stealing malware tied to TeamPCP.

https://www.technadu.com/checkmarx-jenkins-ast-plugin-compromised-by-teampcp-using-credentials-stolen-in-the-trivy-supply-chain-attack/627794/

#CyberSecurity #SupplyChainSecurity #DevSecOps

Checkmarx Jenkins AST Plugin Compromised by TeamPCP Using Credentials Stolen in the Trivy Supply Chain Attack
TechNadu

Checkmarx Jenkins AST Plugin Compromised by TeamPCP Using Credentials Stolen in the Trivy Supply Chain Attack

Checkmarx warns of a rogue Jenkins AST plugin that delivers credential-stealing malware following TeamPCP's breach of GitHub repositories via the Trivy attack.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

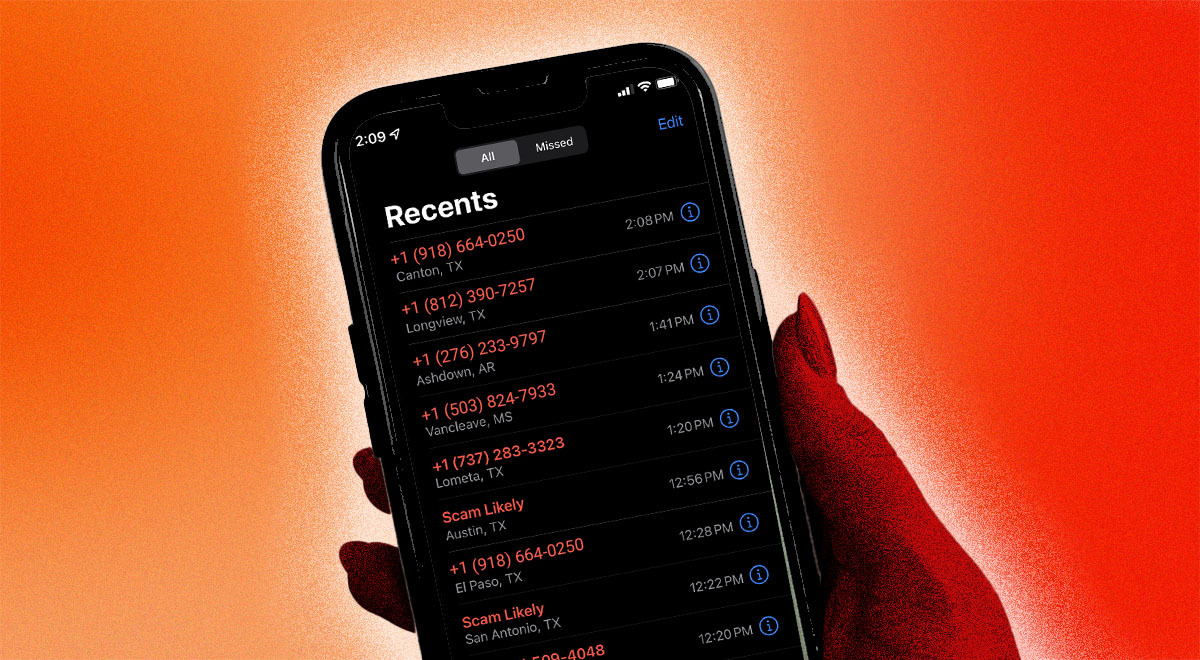
Researchers say fake Android apps promising access to call logs and WhatsApp records reportedly reached 7.3M+ downloads before removal.

The apps allegedly generated completely fake data while charging users subscription fees.
Curiosity-driven mobile scams remain highly effective.

Source: https://cybernews.com/security/fake-call-logs-apps-android-users-fraud/

Follow @technadu@infosec.exchange for more.

#CyberSecurity #Android #MobileSecurity

Millions of Android users tricked into paying for fake call logs
Cybernews

Millions of Android users tricked into paying for fake call logs

Researchers found fraudulent apps on Google Play that claim to provide the call history “for any number.” They had been downloaded more than seven million times before being taken down.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago
Replying to
@simonzerafa@infosec.exchange Dwelling for two years isn't just a oversight; it's a structural failure in visibility. It really highlights the "Death Star" level of technical debt many utilities are carrying. When you’re dealing with legacy OT systems that were never meant to be online, you end up with a massive attack surface that’s almost impossible to patch without breaking something critical.
0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Cloud Atlas APT campaigns targeting Russia & Belarus are leveraging phishing, CVE-2018-0802, SSH tunnels, and a new “PowerCloud” tool that exfiltrates data into Google Sheets.

https://www.technadu.com/cloud-atlas-apt-targets-russia-and-belarus-government-and-diplomatic-entities-with-powercloud-tool/628312/

#CyberSecurity #ThreatIntel #APT #InfoSec #Malware

Cloud Atlas APT Targets Russia and Belarus Government and Diplomatic Entities with PowerCloud Tool
TechNadu

Cloud Atlas APT Targets Russia and Belarus Government and Diplomatic Entities with PowerCloud Tool

Kaspersky attributes pervasive SSH tunnel activity in Russia and Belarus to the Cloud Atlas group, utilizing new tools like PowerCloud alongside ReverseSocks and Tor.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Spanish court rejects LaLiga’s request to fine NordVPN over IPTV blocking compliance claims.

The dispute is intensifying concerns around overblocking after reports of disruptions affecting platforms like Cloudflare, GitHub, Docker & Vercel in Spain.

https://www.technadu.com/nordvpn-blocking-dispute-faces-new-spanish-court-ruling/628323/

#Cybersecurity #VPN #DigitalRights

Spanish Court Refuses LaLiga’s Request to Fine NordVPN Over IPTV Blocking Dispute
TechNadu

Spanish Court Refuses LaLiga’s Request to Fine NordVPN Over IPTV Blocking Dispute

NordVPN blocking dispute expands after Spanish court rejected LaLiga fines over anti-piracy measures and IP-level overblocking concerns.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

Researchers say fake Android apps promising access to call logs and WhatsApp records reportedly reached 7.3M+ downloads before removal.

The apps allegedly generated completely fake data while charging users subscription fees.
Curiosity-driven mobile scams remain highly effective.

Source: https://cybernews.com/security/fake-call-logs-apps-android-users-fraud/

Follow @technadu@infosec.exchange for more.
#CyberSecurity #Android #MobileSecurity

Millions of Android users tricked into paying for fake call logs
Cybernews

Millions of Android users tricked into paying for fake call logs

Researchers found fraudulent apps on Google Play that claim to provide the call history “for any number.” They had been downloaded more than seven million times before being taken down.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Texas is suing Netflix over alleged user tracking and data sharing practices involving advertisers and data brokers.

The lawsuit claims Netflix tracked viewing habits, location data, devices, and kids’ profile activity without proper transparency.

Source: https://therecord.media/texas-sues-netflix-over-data-practices-surveillance

Follow @technadu@infosec.exchange
#Privacy #InfoSec #CyberSecurity

Texas sues Netflix over alleged data practices that create ‘surveillance machinery’ without user consent
therecord.media

Texas sues Netflix over alleged data practices that create ‘surveillance machinery’ without user consent

In addition to fines, Texas is asking a judge to prevent Netflix from illegally collecting and sharing user data and to mandate that the company no longer use autoplay by default on kids’ profiles.

0
0
1
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Sophos reports that 71% of orgs faced identity-related breaches last year, with average costs reaching $1.64M.

Weak API keys, service accounts, and AI agents are now major ransomware entry points.

https://www.technadu.com/sophos-2026-report-details-escalating-security-threats-identity-security-breaches-cost-1-6-million/627836/

#CyberSecurity #IdentitySecurity #Ransomware #Infosec

Sophos 2026 Report Details Escalating Security Threats: Identity Security Breaches Cost $1.6 Million
TechNadu

Sophos 2026 Report Details Escalating Security Threats: Identity Security Breaches Cost $1.6 Million

The Sophos State of Identity Security 2026 report surveys 5,000 IT leaders, detailing NHI vulnerabilities, ransomware links, and $1.64 million breach costs.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Anthropic’s Claude Mythos Preview reportedly uncovered 10K+ high/critical zero-days during Project Glasswing.

Cloudflare, Mozilla, Cisco, Microsoft, Apple & Google were linked to the initiative.

Big question:
Can defenders patch fast enough in the AI era?

Source: https://cybersecuritynews.com/anthropics-claude-mythos-preview-0-days/

Follow @technadu@infosec.exchange for more threat intel & AI security updates.

#Cybersecurity #AI #ZeroDay #ThreatIntel #AISecurity

cybersecuritynews.com
0
0
2
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

Cloud security ≠ failing
It’s hitting human limits
• Exploits in hours
• Identity sprawl
• Manual remediation bottleneck

Future:
Humans set guardrails
Machines respond

Source: https://www.sysdig.com/blog/sysdig-2026-cloud-native-security-and-usage-report

💬 Agree?
Follow @technadu@infosec.exchange

#InfoSec #CloudSecurity #AI

Cloud security has hit its human limits: Key takeaways from the 2026 Cloud-Native Security and Usage Report | Sysdig
sysdig.com

Cloud security has hit its human limits: Key takeaways from the 2026 Cloud-Native Security and Usage Report | Sysdig

Cloud security has reached human limits. Discover key findings from the 2026 Sysdig report and why machine-speed defense is the future.

0
0
1
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Canadian authorities arrested alleged KimWolf botnet admin “Dort” in connection with a DDoS-for-hire operation that reportedly infected 1M+ IoT devices and launched 25,000+ attacks.

Source: https://www.technadu.com/canadian-administrator-arrested-following-kimwolf-ddos-botnet-takedown/628296/

#Cybersecurity #DDoS #Botnet #IoT

Canadian Administrator Arrested Following KimWolf DDoS Botnet Takedown
TechNadu

Canadian Administrator Arrested Following KimWolf DDoS Botnet Takedown

U.S. authorities charge Jacob Butler with operating the KimWolf DDoS botnet following his arrest in Canada. The IoT botnet infected over a million devices.

0
0
1
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

CVE-2026-41940 is under active mass exploitation.

Researchers say threat group “Mr_Rot13” is exploiting the critical cPanel flaw to steal credentials, deploy webshells, and gain persistent access across hosting infrastructure.

2,000+ attacking IPs observed globally.

https://www.technadu.com/cve-2026-41940-vulnerability-in-cpanel-exploited-to-steal-credentials/627803/

#CyberSecurity #ThreatIntel #cPanel

CVE-2026-41940 Vulnerability in cPanel Exploited to Steal Credentials
TechNadu

CVE-2026-41940 Vulnerability in cPanel Exploited to Steal Credentials

QiAnXin XLab details how the Mr_Rot13 threat group exploits CVE-2026-41940 in cPanel to deploy backdoors, steal credentials, and gain administrator access.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 5mo ago

OT malware ZionSiphon targets water systems 🚨
• Alters chlorine & pressure
• ICS protocol scanning
• USB propagation

Details 👇
https://www.technadu.com/zionsiphon-malware-threatens-israeli-water-systems-attempting-to-sabotage-chlorine-levels-and-pressure/626046/

#Infosec #OTSecurity

ZionSiphon Malware Threatens Israeli Water Systems, Attempting to Sabotage Chlorine Levels and Pressure
TechNadu

ZionSiphon Malware Threatens Israeli Water Systems, Attempting to Sabotage Chlorine Levels and Pressure

Darktrace's OT malware analysis of ZionSiphon highlights a threat designed to compromise Israeli water systems and critical infrastructure cybersecurity.

0
0
0
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

Müzeyyen Gökçen Arslan Tapkan of Black Kite says organizations still confuse compliance with actual security.

⚠️ Vendors can pass audits while exposing live risk
⚠️ Attackers rank vendors by exposure paths, not spend
⚠️ AI is worsening noise and confidence problems in cyber datasets

“Saying HITL in TPCRM is easy. Designing for it, vendor by vendor, signal by signal, decision by decision, this is the real work.”

https://www.technadu.com/why-attackers-understand-supply-chains-better-than-companies/628246/

#CyberSecurity #TPRM #SupplyChainSecurity #AI #Compliance

Why Attackers Understand Supply Chains Better Than Companies 
TechNadu

Why Attackers Understand Supply Chains Better Than Companies 

Black Kite Director of Data Research Müzeyyen Gökçen Arslan Tapkan explains why compliance creates false confidence, and vendors become risky.

0
0
1
0
Open post
TechNadu @technadu@infosec.exchange
· 4mo ago

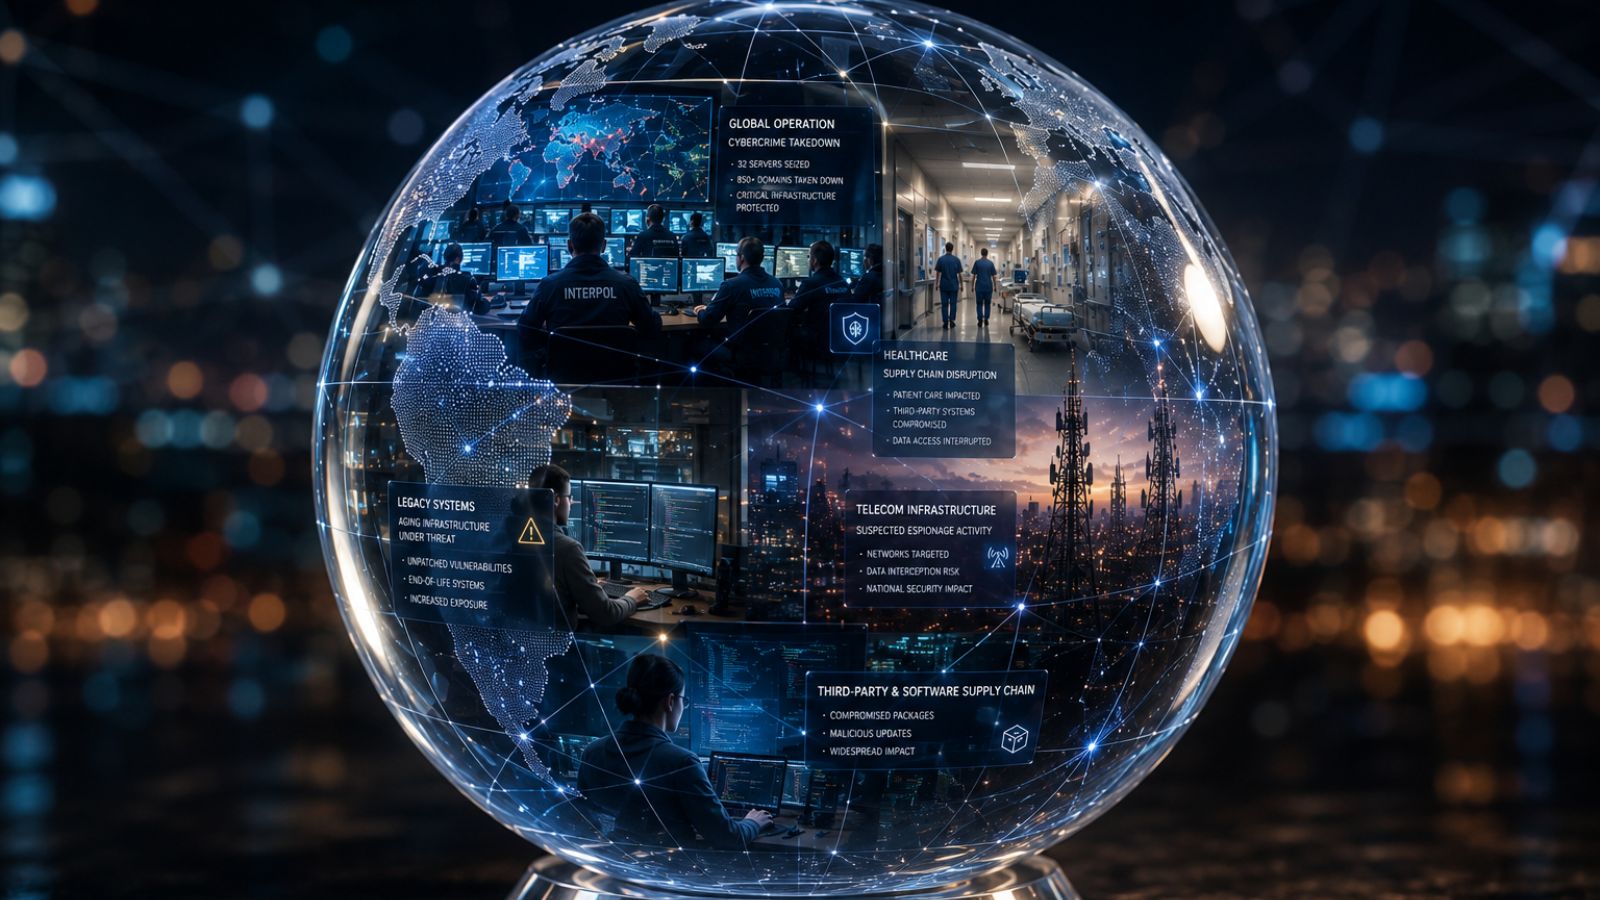
Major cybercrime operations were dismantled this week, including malware-signing services, DDoS botnets, phishing infrastructure, and criminal VPN networks.

At the same time, researchers warned about AI-driven exploitation, poisoned VS Code extensions, Linux telecom malware, and healthcare data breaches.

https://www.technadu.com/cybersecurity-roundup-defenders-score-major-wins-against-cybercrime-networks-while-legacy-risks-deepen/628319/

#CyberSecurity #InfoSec #ThreatIntel #Ransomware

Cybersecurity Roundup: Defenders Score Major Wins Against Cybercrime Networks While Legacy Risks Deepen
TechNadu

Cybersecurity Roundup: Defenders Score Major Wins Against Cybercrime Networks While Legacy Risks Deepen

Cybersecurity roundup covering major law enforcement crackdowns on cybercrime networks, healthcare disruptions, legacy system risks and more.

0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service
elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite
j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 07:18:41 UTC