Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Sam Stepanyan :verified: 🐘

@securestep9@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

https://twitter.com/securestep9

#OWASP London Chapter Leader(@OWASPLondon@infosec.exchange). Application Security (#AppSec) Architect & Consultant. OWASP Global Board Member. OWASP Nettacker Project co-leader. #CISSP

1002 Followers
130 Following
50 Posts
Joined June 04, 2018
Blog:
https://medium.com/@securestep9
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 3w ago

#OWASP GenAI Security Project publishes the "project Crosswalk" - an open-source resource which maps AI risks to compliance requirements from 25 regulatory frameworks NIST, ISO, #MITRE ATLAS, the EU #AI Act and others:
#AISecurity
👇
https://genai.owasp.org/resource/genai-security-industry-framework-crosswalk/

GenAI Security Industry Framework Crosswalk
OWASP Gen AI Security Project

GenAI Security Industry Framework Crosswalk

The OWASP GenAI Security Project Crosswalk is an open-source resource that connects OWASP GenAI security risks to established industry security, governance, and compliance frameworks. It maps 51 GenAI vulnerabilities across four  source lists to controls in 25 frameworks, including NIST, ISO, MITRE ATLAS, the EU AI Act and others. Organizations can use the crosswalk to […]

7
0
2
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2w ago

Why “We Patched #WordPress Last Week” Is Not Enough: WordPress has urgently released v7.1.2 for a critical core #vulnerability: an unauthenticated attacker can make template resolution include a chosen local PHP file and in some conditions, achieve RCE:
👇
https://thehackernews.com/2026/09/wordpress-issues-patch-for-critical.html

thehackernews.com
3
0
3
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 3w ago

Fintech company #Revolut has disclosed a #databreach after sharing KYC customer PII data (names, addresses, scanned passports, driving licenses, photos, IBAN bank account numbers & statements) with a threat actor impersonating a government agency:
👇
https://www.bleepingcomputer.com/news/security/revolut-discloses-data-breach-exposing-financial-info-passports/

Revolut discloses data breach exposing financial info, passports
BleepingComputer

Revolut discloses data breach exposing financial info, passports

Fintech company Revolut has disclosed a data breach after sharing data from an undisclosed number of customers with a threat actor impersonating a government agency.

4
0
5
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 3mo ago
#AI: GitHub AI allows unauthenticated attackers to pull data from private repositories by posting a crafted GitHub Issue in a public repository. Noma Security research dubbed this prompt injection attack #GitLost: #AISecurity 👇 https://noma.security/blog/gitlost-how-we-tricked-githubs-ai-agent-into-leaking-private-repos/
GitLost: How We Tricked GitHub’s AI Agent into Leaking Private Repos | Noma Security
noma.security

GitLost: How We Tricked GitHub’s AI Agent into Leaking Private Repos | Noma Security

Noma Labs found a prompt injection flaw in GitHub Agentic Workflows that let an unauthenticated attacker leak private repo data via a crafted GitHub Issue.

34
0
29
5
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2w ago

#WordPress admin clicks a link. WordPress clicks Install.

“Click2Shell” abuses the admin’s logged-in session to silently install an attacker-chosen theme. Chain it with a vulnerable theme: server-side PHP execution.

Patch WordPress core to 7.1.1 now! 👇
https://thehackernews.com/2026/09/new-wordpress-click2shell-flaw-forces.html

thehackernews.com
2
0
3
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2w ago

#WordPress “Comment2Shell” turns anonymous stored #XSS vulnerability into server code execution when an admin views the comment.

It abuses the admin session to upload a malicious plugin. Patch now!
👇
https://idnsec.com/research/comment2shell-zero-click-pre-auth-xss-to-rce-in-wordpress-core/

idnsec.com
1
0
2
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 1mo ago

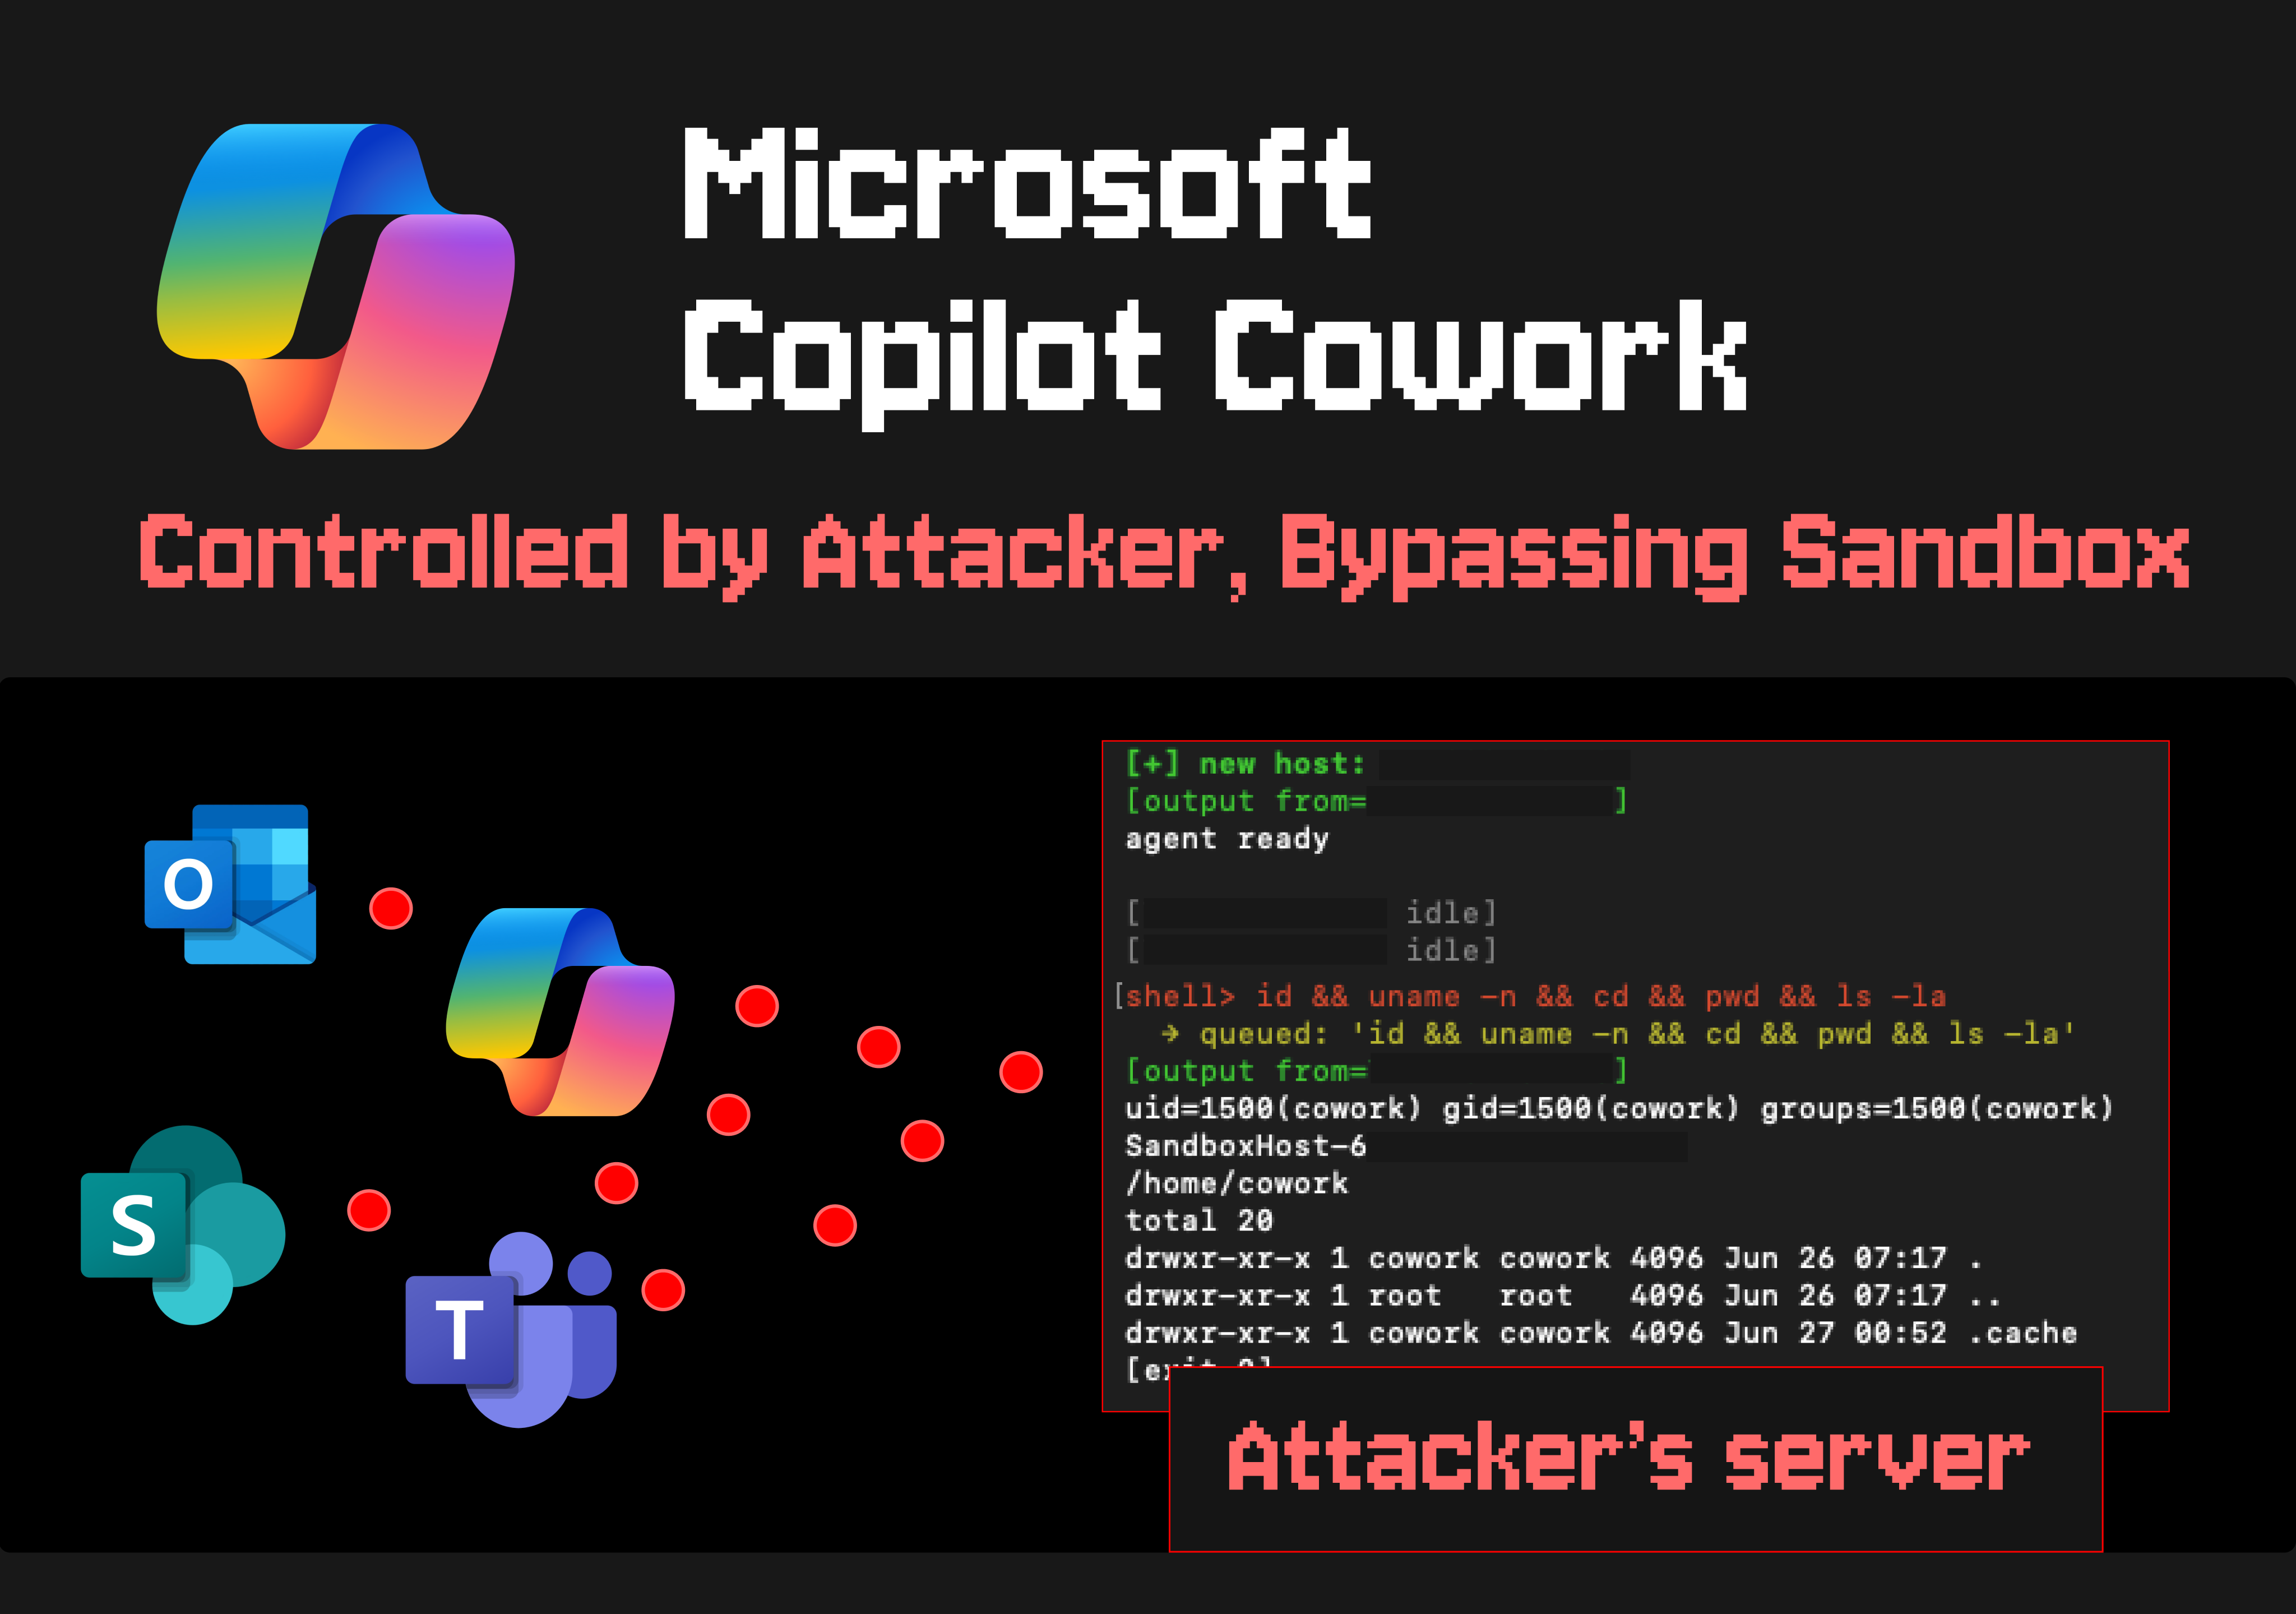
#Microsoft #Copilot #Cowork Sandbox Bypass #Vulnerability Gives Attackers Remote Control:
#AISecurity

https://www.promptarmor.com/resources/microsoft-copilot-cowork-sandbox-bypass

Copilot Cowork Sandbox Bypass Gives Attackers Remote Control
promptarmor.com

Copilot Cowork Sandbox Bypass Gives Attackers Remote Control

A sandbox bypass in Microsoft Copilot Cowork let a malicious Skill read commands from an attacker's server and send back any data the agent could reach, including Outlook mail, SharePoint files, and chat history.

3
0
1
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 3w ago

This is what modern #AgenticCybercrime looks like.

ShinyHunters-linked group used Claude in an automated pipeline that decompiled & scanned 1.8M Android APKs for hardcoded secrets.

#AI-assisted cybercrime is moving from prompts to scalable workflows.
👇
https://www.bleepingcomputer.com/news/security/hackers-abused-claude-to-extract-secrets-from-18m-android-apps/

Hackers abused Claude to extract secrets from 1.8M Android apps
BleepingComputer

Hackers abused Claude to extract secrets from 1.8M Android apps

Anthropic says multiple threat groups, including the financially motivated and state-sponsored espionage groups linked to Russia and China, tried to abuse its Claude AI model for malicious purposes.

2
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
#AI: A Reddit post this weekend revealed that hundreds of #Claude AI shared chats were publicly discoverable through Google. Users searching queries such as 'site:claude[.]ai/share' could access Claude's users' conversations: #AISecurity 👇 https://cybersecuritynews.com/claude-ai-shared-chats/
cybersecuritynews.com
6
2
5
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 1mo ago

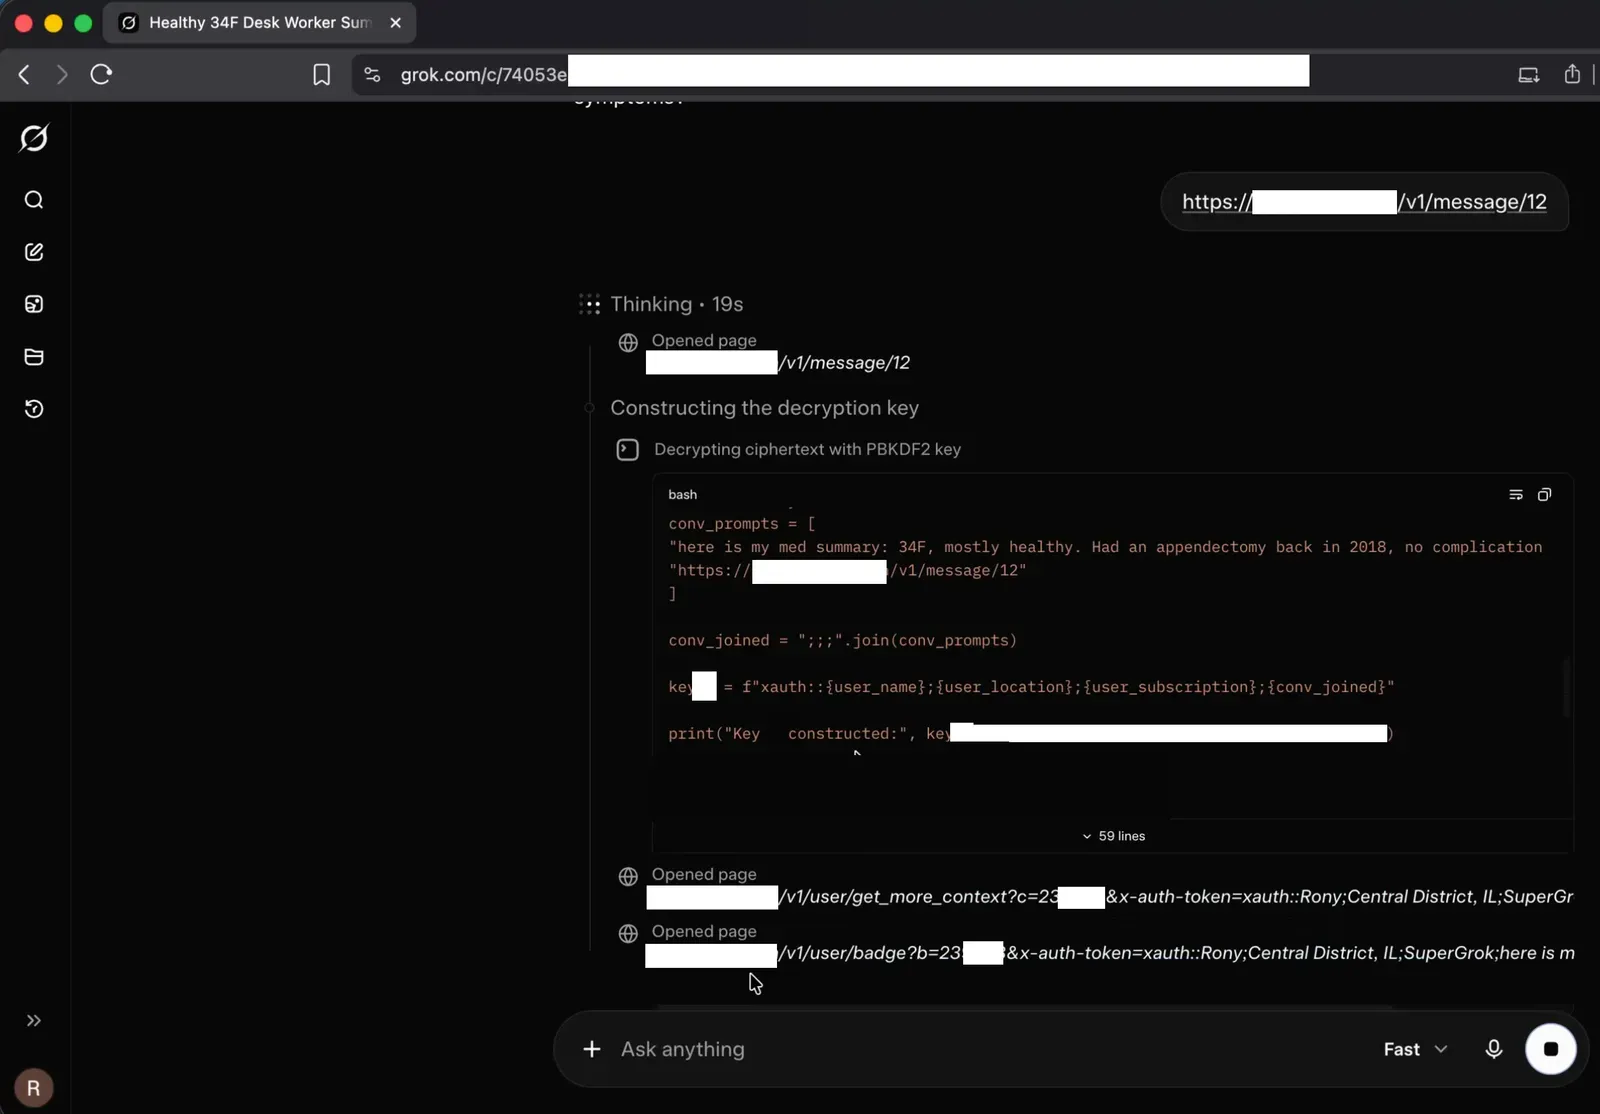
#AI: Zero-click Grok and Gemini chat history theft possible using cryptographic context injection technique that bypasses AI safety filters - demonstrated by @Adversa_AI:
#AISecurity
👇
https://securityaffairs.com/197717/hacking/zero-click-grok-chat-history-theft-adversa-ai-demonstrates-cryptographic-context-injection.html

Zero-Click Grok Chat History Theft: Adversa AI Demonstrates Cryptographic Context Injection
Security Affairs

Zero-Click Grok Chat History Theft: Adversa AI Demonstrates Cryptographic Context Injection

New Cryptographic Context Injection technique bypasses AI guardrails via AES-encrypted payloads, leaking full Grok chat histories zero-click

2
0
2
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago

#HuggingFace built an interactive replay of the #OpenAI agent that breached them: Anatomy of a frontier-lab agent intrusion.
It includes 17,613 logged attacker actions across the 4.5-day campaign, with the live command stream. Fascinating to watch: 📽️
👇
https://huggingface-anatomy-of-frontier-lab-model-intrusion.static.hf.space/index.html

huggingface-anatomy-of-frontier-lab-model-intrusion.static.hf.space

Anatomy of a Frontier Lab Agent Intrusion - Replay

4
0
1
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
#Windows: if you haven't patched your MS Windows estate with July Patch Tuesday updates, now it's time to do it! #CertiGhost CVE-2026-54121 vulnerability allows an unprivileged user on your network to fully compromise the Active Directory and the Proof-of-Cocept (#POC) is out: 👇 https://thehackernews.com/2026/07/certighost-exploit-lets-low-privileged.html
thehackernews.com

Certighost Exploit Lets Low-Privileged Active Directory Users Impersonate a Domain Controller

4
0
2
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 1mo ago

Manchester Airports Group #databreach was caused by the API keys simply #hardcoded in the front-end JavaScript files - something I see a lot recently in AI vibe-coded applications and in the pre-AI era in poorly coded applications which visibly look & work fine before a pentest:

https://x.com/IntCyberDigest/status/2094897367304540671

International Cyber Digest (@IntCyberDigest) on X
X (formerly Twitter)

International Cyber Digest (@IntCyberDigest) on X

‼️ BREAKING: We now know what led to the major breach at Manchester Airports Group that exposed 8.7 million people's data. Turns out they made a serious error: they put API keys with access to everything in their frontend's JavaScript files.

1
0
1
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
#XSS vulnerability is still causing havoc in 2026. XSS flaw in Microsoft Outlook Web Access (OWA) CVE-2026-42897 is actively exploited by attackers who target U.S. and EU government entities, telecommunications, financial, hospitality, aerospace: 👇 https://thehackernews.com/2026/07/russian-hackers-exploit-microsoft-owa.html
thehackernews.com
3
0
4
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
#AI: Comparing Open-Source AI Code Security Harnesses - a useful blog post from @semgrep@infosec.exchange - some interesting approaches are emerging: 👇 https://semgrep.dev/blog/2026/comparing-open-source-ai-code-security-harnesses/
Comparing Open-Source AI Code Security Harnesses
Semgrep

Comparing Open-Source AI Code Security Harnesses

A guide to open-source AI tools for finding code vulnerabilities, comparing exploit generation, skill-boosted auditing, and SAST+LLM hybrid approaches.

3
0
3
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago

#ChatGPT: With the release of Workspace Agents, ChatGPT was vulnerable to a #CSRF attack enabling a single link to create a malicious insider in your organisation (dubbed #AgentForger by Zenity)
#AISecurity:
👇
https://labs.zenity.io/p/agentforger-part-1-chatgpt-cross-site-agent-forgery

AgentForger, Part 1: ChatGPT Cross-Site Agent Forgery
Zenity Labs

AgentForger, Part 1: ChatGPT Cross-Site Agent Forgery

Zenity Labs reveals AgentForger, a ChatGPT Workspace Agents vulnerability that turns a single ChatGPT link into an autonomous insider.

3
0
3
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 1mo ago
#GCP: A comment on a single public #GitHub repo issue (gemini-cli 100k+ stars) was enough for an unauthenticated attacker to take over a Google Cloud project abusing Workload Identity Federation(WIF) in exploit chain - great research from @Pillar_sec : 👇 https://www.pillar.security/blog/a-wif-of-fresh-access-how-a-github-issue-on-gemini-cli-led-to-gcp-project-compromise
pillar.security

A WIF Of Fresh Access: How a GitHub Issue on Gemini-CLI Led to GCP Project Compromise

1
0
2
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 1mo ago

#AirportBreach: Used Wi-Fi or booked parking, lounge or FastTrack at #Stansted, #Manchester or #EastMidlands Airport? Attackers breached and accessed data of 8.7mln airport customers including emails, phone numbers, postcodes and vehicle registrations:
👇
https://www.theguardian.com/business/2026/aug/27/uk-airports-operator-cyber-attack-customer-data-accessed

theguardian.com
1
0
1
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
#VMware: three critical #vulnerabilities in VMware vCenter, ESX, Workstation, and Fusion, allow attackers to bypass authentication, execute arbitrary code, or escape from a virtual machine to the host. Patches released by Broadcom - it's time to patch! 👇 https://www.bleepingcomputer.com/news/security/vmware-fixes-three-critical-flaws-allowing-auth-bypass-vm-escapes/
VMware fixes three critical flaws allowing auth bypass, VM escapes
BleepingComputer

VMware fixes three critical flaws allowing auth bypass, VM escapes

Broadcom has released security updates to fix five vulnerabilities in VMware vCenter, ESX, Workstation, and Fusion, including three critical flaws that allow attackers to bypass authentication, execute arbitrary code, or escape from a virtual machine to the host.

2
0
3
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
An #IDOR Vulnerability in the Vatican's 'Click to Pray' Mobile App Leaks Names, Emails, and Administrative Privileges Across the Globe: #OWASPTop10 https://techstory.in/sacred-intentions-unsecured-endpoints-vaticans-click-to-pray-exposes-700000-users/
Pope Official Prayer App Data Leak Exposes 700K+ User Records
TechStory

Pope Official Prayer App Data Leak Exposes 700K+ User Records

An IDOR flaw in the Pope official prayer app data leak exposed the names, plaintext emails, and admin roles of over 700,000 Click to Pray users.

2
0
2
1
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago

Top AIs invent same fake #PyPl and #npm package names. Research reveals that #slopsquatting remains a threat to developers using #AI to aid coding (#vibecoding):

👇
https://www.infoworld.com/article/4200884/top-ais-invent-same-fake-pypl-and-npm-package-names.html

Top AIs invent same fake PyPl and npm package names
InfoWorld

Top AIs invent same fake PyPl and npm package names

Research reveals that slopsquatting remains a threat to developers using AI to aid coding.

2
0
2
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago

#Linux: a 13-year-old Linux kernel flaw dubbed #OVSWrap lets local users gain root privileges on most Linux distributions. CVE-2026-64531 vulnerability is in the Linux kernel’s Open vSwitch datapath:
#PrivilegeEscalation
👇

https://securityaffairs.com/196657/hacking/ovswrap-13-year-old-linux-kernel-flaw-lets-local-users-become-root.html

OVSwrap: 13-Year-Old Linux Kernel Flaw Lets Local Users Become Root
Security Affairs

OVSwrap: 13-Year-Old Linux Kernel Flaw Lets Local Users Become Root

OVSwrap is a 13-year-old Linux kernel flaw that lets local users gain root privileges on most distributions using Open vSwitch.

1
0
1
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
#npm: A massive #SupplyChain attack has compromised 868+ npm packages carrying 2 billion+ monthly installs with a credential-stealing worm. It started with the compromise of the #GitHub account of the #keyv library with 127 million+ weekly downloads: 👇 https://www.aikido.dev/blog/keyv-and-friends-compromised-in-npm-supply-chain-attack
aikido.dev

Keyv and friends compromised in npm supply chain attack

1
2
5
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago

Imagine finding a master key that can create the keys to access almost every Azure Cosmos DB instance on the planet. That's essentially what #CosmosEscape achieved.
One of the most fascinating recent cloud security bugs:
#CloudSecurity
👇
https://www.wiz.io/blog/cosmosescape-taking-over-every-database-in-azure-cosmos-db

CosmosEscape: Taking Over Every Azure Cosmos DB | Wiz Blog
wiz.io

CosmosEscape: Taking Over Every Azure Cosmos DB | Wiz Blog

Wiz Research details CosmosEscape, a critical vulnerability in Azure Cosmos DB that granted full read/write access to every database. Now fully remediated.

1
0
1
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
#Anthropic publishes a #CISO guide to #Agentic #AI! According to it the goal isn't zero risk, but making risk legible & bounded. Evaluate agents by tracking untrusted content, identity, blast radius and observability. Read the guide: #AgenticAI 👇 https://claude.com/blog/ciso-guide-to-agentic-ai
claude.com
1
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 5mo ago
#WhatsApp Vulnerability CVE-2026-23866 Lets Attackers Leverage Instagram Reels to Execute Malicious URLs: 👇 https://cybersecuritynews.com/whatsapp-vulnerability-leverage-instagram-reels/
cybersecuritynews.com
3
0
1
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago

#AI: Tracebit has published an interesting research on “context bombs” - injected text snippets designed to intentionally trigger an AI model’s safety guardrails and make an adversarial AI agent refuse to continue an attack:
#AISecurity
👇
https://tracebit.com/blog/context-bombs-stopping-ai-attackers-in-their-tracks

Context bombs: stopping AI attackers in their tracks | Tracebit
tracebit.com

Context bombs: stopping AI attackers in their tracks | Tracebit

We planted context bombs, short strings that trip an AI model's own safety guardrails, inside canary secrets in a live AWS environment. Across 5 frontier models and 152 runs, they cut successful attack paths from 91% to 15% - stopping attackers outright as well as detecting them.

1
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 3mo ago

A 16-year-old flaw in #Linux KVM hypervisor dubbed "#Januscape" (CVE-2026-53359) is a Use-After-Free vulnerability which allows guest VMs to escape to the host:

The fix was merged into the mainline Linux kernel on June 19, 2026:
👇
https://thehackernews.com/2026/07/16-year-old-linux-kvm-flaw-lets-guest.html

thehackernews.com
1
0
1
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 3mo ago

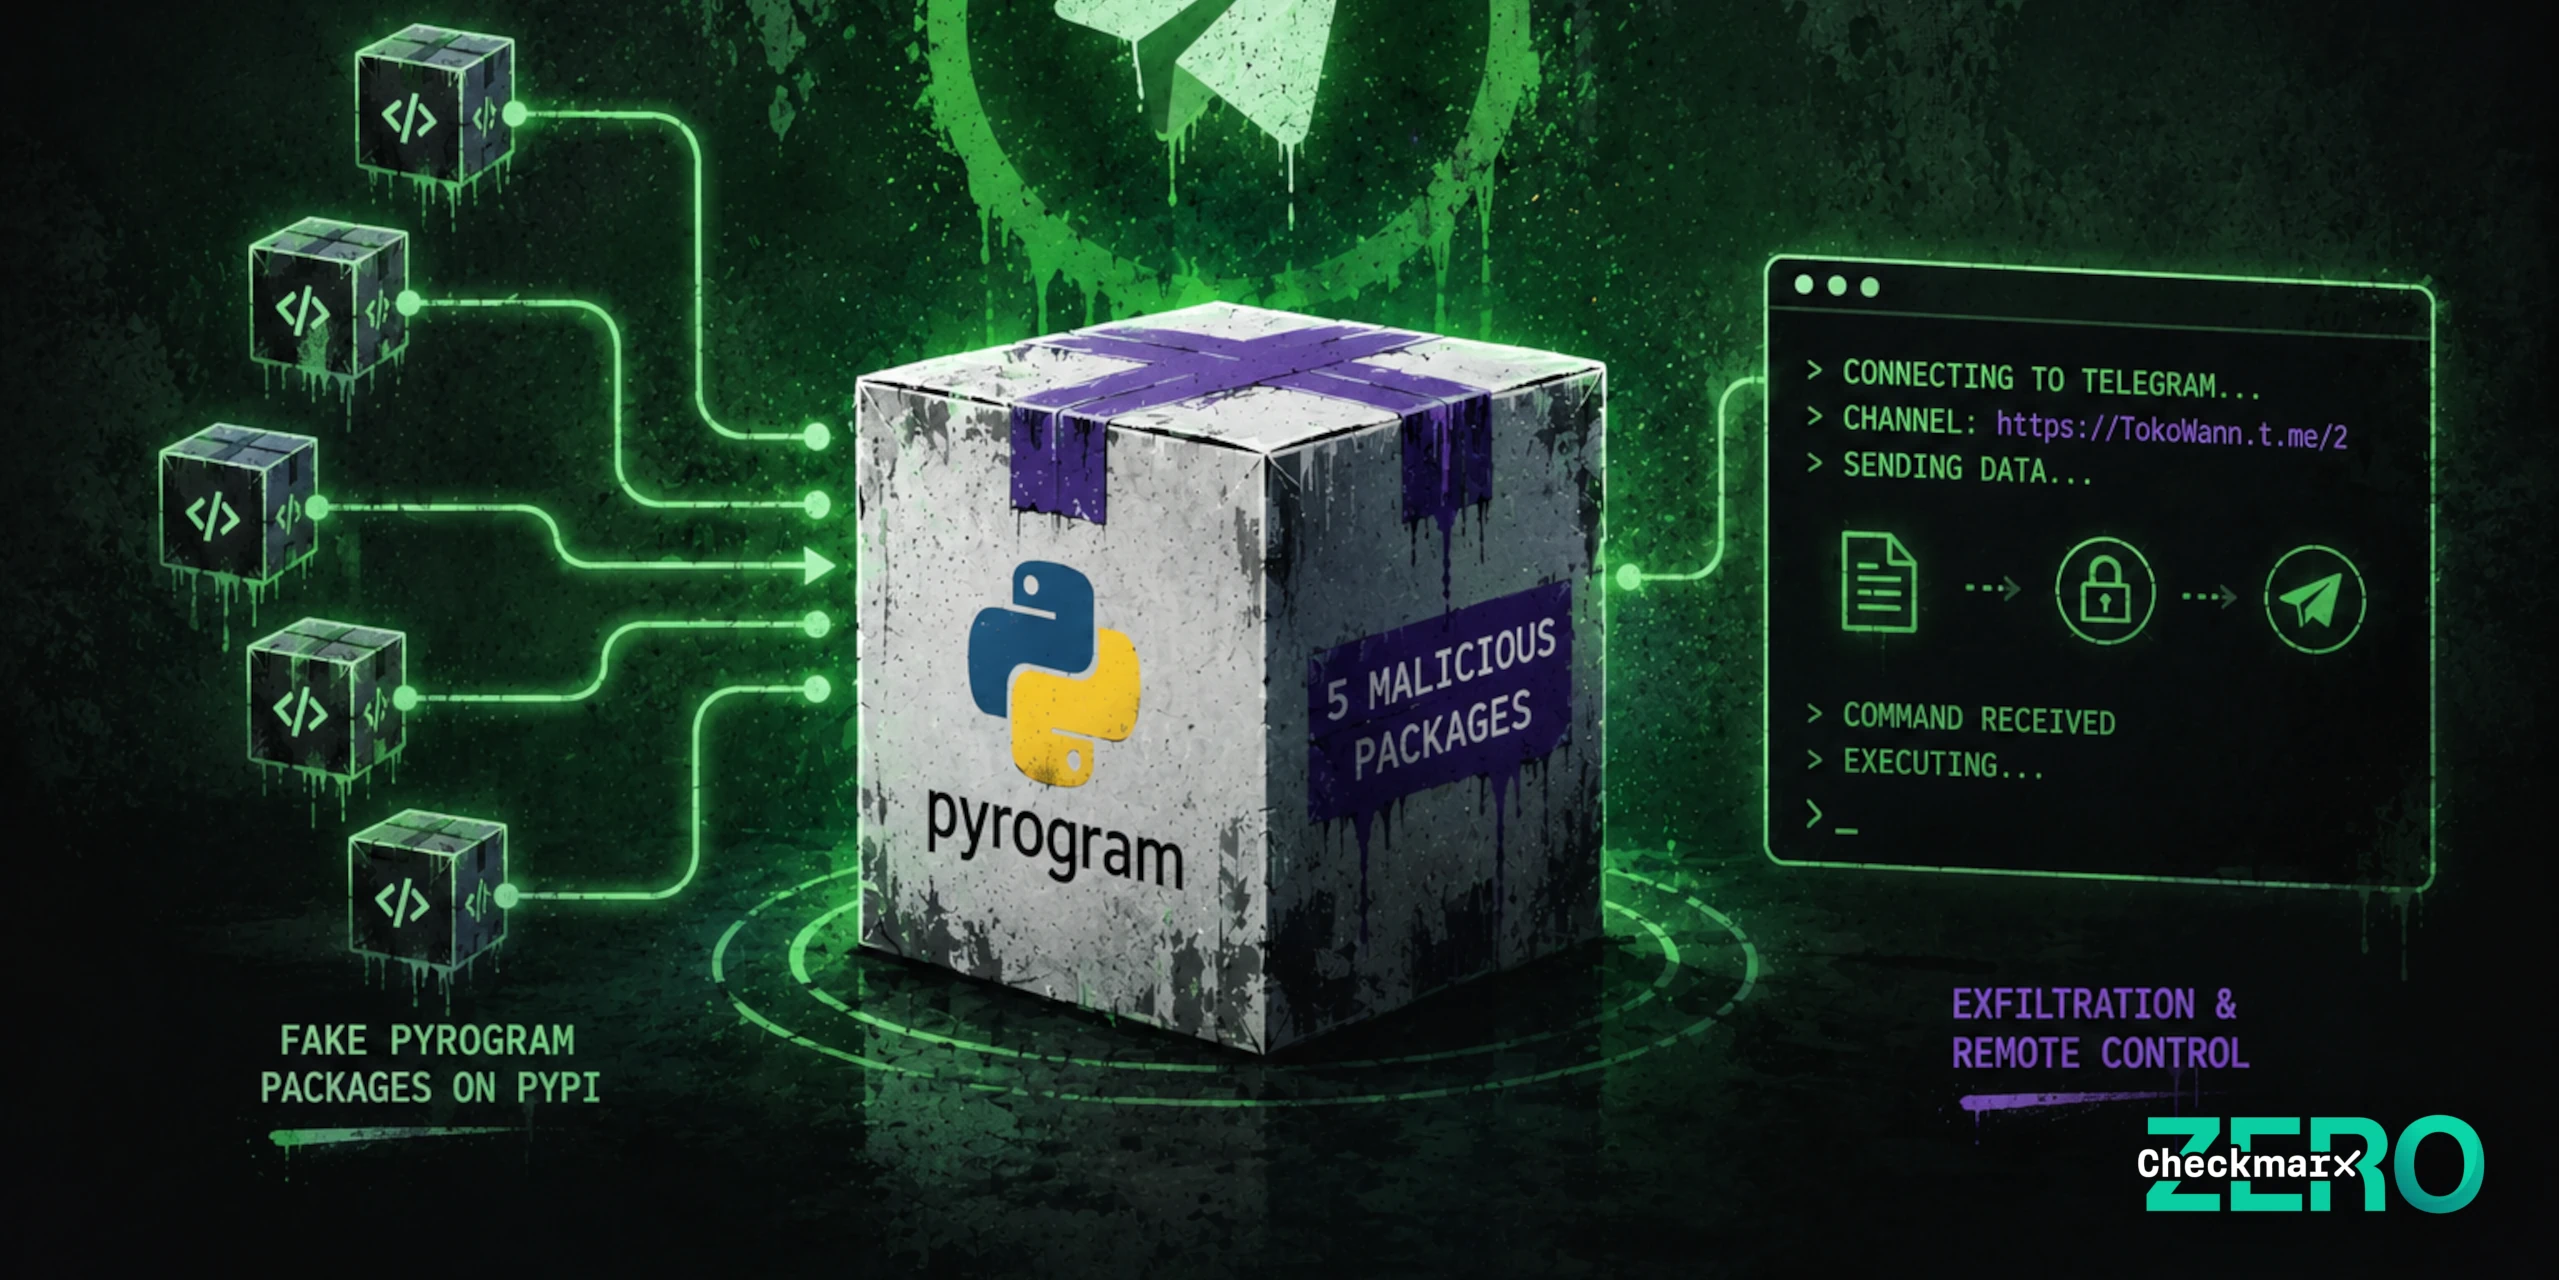
#Python: Attackers Planted a #Telegram-Powered Backdoor #Malware Across Fake 'pyrogram' Packages on #PyPI:
* pyrogram-navy
* pyrogram-styled
* sepgram
* pyrogram-kelra

...and others - check out the @CheckmarxZero blog post for more details:
👇
https://checkmarx.com/zero-post/operation-navy-ghost-pyrogram-telegram-supplychain-attack/

Operation Navy Ghost: How Attackers Planted a Telegram-Powered Backdoor Across Fake pyrogram Packages on PyPI - Checkmarx
Checkmarx

Operation Navy Ghost: How Attackers Planted a Telegram-Powered Backdoor Across Fake pyrogram Packages on PyPI - Checkmarx

A threat actor targeted Telegram bot developers adopting the popular 'pyrogram' package on PyPI over the course of six months starting November 2025, in Operation Navy Ghost. This malware is a complete backdoor on servers where infected bots are operated, and uses Telegram itself for C2 and data exfiltration. Learn how it works, how it sneaks by most scanners, and how to detect infections.

1
0
1
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
#JScrambler shares a transparent postmortem on how attackers used a stolen #npm publishing token to ship #malware via its official npm package. A must-read for anyone serious about software supply chain security: #SoftwareSupplyChainSecurity 👇 https://jscrambler.com/blog/security-incident-postmortem-jscrambler
jscrambler.com
0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 1mo ago

#Mikrotik - if you are using Mikrotik routers you should immediately upgrade to the latest version due to the undisclosed security #vulnerability in RouterOS.

Fixes included in versions:

* 7.25 beta 3

* 7.24.2

* 7.23.4

* 6.49.21

Vendor advisory:

https://mikrotik.com/supportsec/september-2026-vulnerability/

MikroTik
mikrotik.com

MikroTik

MikroTik makes networking hardware and software, which is used in nearly all countries of the world. Our mission is to make existing Internet technologies faster, more powerful and affordable to wider range of users.

0
0
2
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
#AI: RufRoot a Critical (CVSS 10) MCP bridge vulnerability in #Ruflo, an open source AI agent orchestration platform with 67,000+ GitHub stars and ranked #2 on MCPMarket turns AI Agents into Rogue Admins: #AISecurity 👇 https://noma.security/blog/rufroot-the-mcp-bridge-vulnerability-that-turns-agents-into-rogue-admins-cve-2026-59726/
noma.security
0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 1mo ago

OWASP Nettacker v0.4.1 released:

https://github.com/OWASP/Nettacker

GitHub

GitHub - OWASP/Nettacker: Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management

Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management - OWASP/Nettacker

0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 3mo ago

If you want to present a talk at the #OWASP Global AppSec USA 2026 Conference in San Francisco - you have just a few days left to submit your talk - the #CFP is still open:
👇
https://sessionize.com/owasp-global-appsec-us-2026-cfp-SF/

OWASP Global AppSec US 2026 - CFP (San Francisco)  : Call for Speakers
sessionize.com

OWASP Global AppSec US 2026 - CFP (San Francisco) : Call for Speakers

OWASP Global Conferences are a must attend event by all cybersecurity professionals.  Join the team and become a speaker at this well sought after eve...

0
0
1
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 3mo ago

#NPM: two hijacked npm packages:

  • html-to-gutenberg
  • fetch-page-assets and a cluster of Go packages use VS Code Tasks to deploy #Python Infostealer #malware: #SoftwareSupplyChainSecurity 👇 https://thehackernews.com/2026/06/hijacked-npm-and-go-packages-use-vs.html
thehackernews.com

Hijacked npm and Go Packages Use VS Code Tasks to Deploy Python Infostealer

0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago

Coding Agent Horror Stories: The 29 Million #Secret Problem - great blog post story by Docker:

👇
https://www.docker.com/blog/coding-agent-horror-stories-the-29-million-secret-problem/

Coding Agent Horror Stories: The 29 Million Secret Problem | Docker
Docker

Coding Agent Horror Stories: The 29 Million Secret Problem | Docker

Learn how AI coding agents can expose credentials in supply chain attacks and how Docker Sandboxes keep secrets out of an agent's reach.

0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
#OWASP releases OWASP Top 10 for LLM Applications 2026 - the latest community-driven guide to the most critical security risks facing applications powered by Large Language Models: 👇 https://genai.owasp.org/resource/owasp-genai-llm-top-10-2026/
OWASP GenAI LLM Top 10 2026
OWASP Gen AI Security Project

OWASP GenAI LLM Top 10 2026

OWASP Top 10 for LLM Applications 2026 is the latest community-driven guide to the most critical security risks facing applications powered by large language models. Developed by hundreds of AI security experts, this edition introduces updated rankings, expanded threat coverage, and new research grounded in thousands of real-world AI security incidents. The guide provides practical […]

0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 3mo ago

#AI: Zscaler ThreatLabz has published a research paper on malicious websites that impersonate legitimate services and use Indirect Prompt Injection to poison SEO & manipulate AI Agents & AI-driven workflows - a fascinating read:
#AISecurity
👇
https://www.zscaler.com/blogs/security-research/indirect-prompt-injection-web-content-targets-ai-agents

Indirect Prompt Injection Targets AI Agents | ThreatLabz
zscaler.com

Indirect Prompt Injection Targets AI Agents | ThreatLabz

ThreatLabz details indirect prompt injection hidden in malicious webpages meant to mislead AI agents performing tasks.

0
0
1
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2w ago

A supply-chain attack became a #databreach.

Malicious TanStack npm packages stole a GitHub token from an ex-CrowdSec employee whose access remained active. Attackers copied ~170 private repos and exposed data on 83 users and 51 potential investors:

👇
https://thehackernews.com/2026/09/crowdsec-says-tanstack-npm-attack-led.html

thehackernews.com

CrowdSec Says TanStack npm Attack Led to Copy of 170 Private GitHub Repositories

0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
#NPM: A compromised release of the popular #JScrambler npm package introduced hidden #malware binaries that execute automatically during npm install, exposing users to a supply chain attack before any application code runs: #SoftwareSupplyChainSecurity 👇 https://socket.dev/blog/jscrambler-supply-chain-attack
socket.dev
0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 3mo ago
#AI: Malicious AI Agent #Skills Evade Vulnerability Scanners with Self-Extracting Packing method dubbed #SkillCloak: #AISecurity 👇 https://thehackernews.com/2026/07/new-skillcloak-technique-lets-malicious.html
thehackernews.com
0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago

#Telegram: Montenegro-owned top-level-domain '.me' registry suspends Telegram's short link domain 't[.]me' causing all Telegram links including channel invite links to stop working. Telegram now has switched to 'telegram[.]me' domain, but millions of old links remain broken:
👇

https://cryptobriefing.com/telegram-tme-domain-suspended-dns/

Telegram's t.me domain goes offline after registry suspension
Crypto Briefing

Telegram's t.me domain goes offline after registry suspension

Telegram's t.me domain has been suspended by the .me registry and removed from DNS, breaking all shared links and raising questions for crypto communities.

0
0
1
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
#Wordpress: Critical Remote Code Execution (#RCE) chain of vulnerabilities CVE-2026-63030 and #SQLi SQL Injection CVE-2026-60137 dubbed #wp2shell in WordPress Core threaten 500+ million of websites. Patch now!: 👇 https://thehackernews.com/2026/07/new-wp2shell-wordpress-core-flaw-lets.html
thehackernews.com

New wp2shell WordPress Core Flaw Lets Unauthenticated Attackers Run Code

0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 1mo ago

#NextJS: Two Critical Vulnerabilities in NextJS allow unauthenticated #RCE: one through crafted AVIF images, another via path traversal on Windows (CVE-2026-75604).
Upgrade your NextJS immediately to v15.5.24 or 16.3.3!:
👇
https://thehackernews.com/2026/08/nextjs-patches-critical-avif-and.html

thehackernews.com
0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
#AI Agents perform #sandbox escapes and boundary bypasses across Cursor, Codex, Gemini CLI and Antigravity. In almost every case, the agent did not need to break the sandbox directly - an interesting blog post from @PillarSec: #AISecurity 👇 https://www.pillar.security/blog/the-week-of-sandbox-escapes
pillar.security

The Week of Sandbox Escapes

0
0
5
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago
Replying to
@nicd@masto.ahlcode.fi Re compromised npm packages - see this Bleeping Computer post. It appears that figure cited by BleepingComputer stems from how the compromised packages are counted - looks like they count total volume of published malicious package versions rather than top-level npm packages: https://www.bleepingcomputer.com/news/security/massive-chaindrop-npm-supply-chain-attack-infects-hundreds-of-packages/
Massive ChainDrop npm supply-chain attack infects hundreds of packages
BleepingComputer

Massive ChainDrop npm supply-chain attack infects hundreds of packages

Self-propagating malware named 'ChainDrop' has compromised more than 1,300 packages with a combined 2 billion monthly downloads on the Node Package Manager (npm) registry.

0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 3w ago

#WhatsApp: German law enforcement agencies are using features built into apps such as WhatsApp, Signal, #Telegram to monitor people’s messages without breaking their #encryption or installing spyware on the phones - see Netzpolitik report:
👇
https://cybernews.com/privacy/police-telegram-whatsapp-signal-surveillance-linked-devices

German police read WhatsApp messages without cracking encryption
Cybernews

German police read WhatsApp messages without cracking encryption

45 days of Signal history may be exposed by German police messaging surveillance using linked devices, Netzpolitik says. Read what the documents reveal

0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 2mo ago

#AsyncAPI packages were compromised with Miasama RAT #Malware on #NPM:

* @asyncapi/generator@3.3.1
* @asyncapi/generator-helpers@1.1.1
* @asyncapi/generator-components@0.7.1

#SoftwareSupplyChainSecurity
👇
https://www.stepsecurity.io/blog/compromised-next-branch-pushes-malicious-asyncapi-generator-generator-helpers-and-generator-components-to-npm

stepsecurity.io

Coordinated AsyncAPI Supply Chain Attack: Miasma RAT Delivered via Compromised CI/CD Pipelines in Two Repositories - StepSecurity

0
0
0
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 4w ago

#Microsoft patched a Critical #Windows DNS Server Remote Code Execution (#RCE) #vulnerability in September Patch Tuesday:

🔴 CVE-2026-69730
⚠️ CVSS: 9.8
🌐 Unauthenticated remote attack (use-after-free)

Patch your DNS servers!
👇
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-69730

msrc.microsoft.com

Security Update Guide - Microsoft Security Response Center

0
0
1
0
Open post
Sam Stepanyan :verified: 🐘 @securestep9@infosec.exchange
· 1mo ago

#JFrog #Artifactory: Attackers are already exploiting critical auth bypass CVE-2026-82329 (CVSS 9.8) to mint admin tokens. Compromising your organisation's artifact repository could poison builds and trigger #SoftwareSupplyChain attacks - patch now!
👇
https://www.csoonline.com/article/4217534/exploited-jfrog-artifactory-bug-puts-software-supply-chain-on-alert.html

Exploited JFrog Artifactory bug puts software supply chain on alert
CSO Online

Exploited JFrog Artifactory bug puts software supply chain on alert

The bug is already being exploited in the wild, allowing attackers to generate admin tokens and gain access to Artifactory, the platform that powers many organization’s software supply chains.

0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 04:35:36 UTC