#bugbounty
32 posts · Last used 21d
Celebrating a major personal milestone this week: my first CVE on an Apple product.
#IndieSec #Cybersecurity #InfoSec #BugBounty
🎪 PRE-FULL DISCLOSURE — wallabag Android — CVSS 9.3 Critical
Code execution on the device, data theft, propagation to other applications. Without the user doing a thing.
CAN-2026-2035994 — GHSA-c6w6-mrjg-3rvx
The Wallabag Circus is back in prime time.
The first magic trick, in front of over a thousand spectators: disappearing. Without publicly responding to an explicit request to coordinate on fixing what was coming. Clear question, zero answers.
The second act: downgrading an 8.5 to a 5.4 — in the very same message where they confirmed the server executes arbitrary requests. (Guess there was no calculator on hand?)
Grand finale: making me disappear too. A ban from the project's channel, in the very same reply asking for more proof. The practical effect is identical to saying "I don't want to hear it."
Despite everything, I gave them another chance. Read the screenshots. *"I haven't done the full disclosure of this second finding yet. Because I am a more honest person than you. I am still giving you an opportunity that you do not deserve."*
Nothing. All in vain. So now the circus is back. And this time, it's a 9.3 act.
#infosec #cybersecurity #vulnerability #XSS #RCE #Android #zeroday #bugbounty #CVE #opensource #appsec #websecurity #responsibleDisclosure #coordDisclosure
What Happened to HackerOne?
HackerOne has changed significantly from the bug bounty platform many researchers knew in the late 2010s.
Its current direction is increasingly centered around Hai, AI-assisted triage, vulnerability validation, agentic testing, continuous testing and CTEM.
But the question isn't simply whether HackerOne uses AI. It's how researcher submissions, security intelligence and AI-driven workflows fit together, and what that means for the role and value of human vulnerability researchers.
I dug into HackerOne's history, funding, Live Hacking Events, pricing shift, AI architecture, researcher-data controversy and current product strategy.
https://thecybersecguru.com/analysis/what-happened-to-hackerone/
#HackerOne #BugBounty #InfoSec #CyberSecurity #AppSec #VulnerabilityResearch #AISecurity #CybersecurityResearch #EthicalHacking #Pentesting #AgenticAI #CTEM #SecurityResearch #BugBountyHunters #ApplicationSecurity
XS-Leaks steal data the same-origin policy swears it protects. SOP hides response contents, not response behavior. This issue covers error-event oracles, frame counting via window.length, the single global socket pool that turns any browser into a stopwatch, and cache probing (terjanq leaked private Google emails this way). Blind injection, cross-origin, against a site you cannot read. https://www.kayssel.com/newsletter/issue-62/
#InfoSec #CyberSecurity #WebSecurity #BugBounty #AppSec #XSLeaks
Welcome to the age of AI-mediated dehumanization and abuse. Ethical hackers will also be replaced by AI agents. Will it end in a machine-versus-machine apocalypse? Or will the internet become a barren, dark wasteland filled with digital ghosts? I saw this coming and quit bug bounty a long time ago; now it's impossible to ignore.
#hackerone #bugbounty #ethicalhacking #infosechttps://blog.teknogeek.io/posts/what-happened-to-hackerone/
🤖 Practical lessons from deploying AI securely at scale
📝 When I first started working on enterprise AI security initiatives, I expected the biggest challen...
https://www.csoonline.com/article/4205710/practical-lessons-from-deploying-ai-securely-at-scale.html
📰 CSO Online
#AI #BugBounty
In an upgradeable proxy, the funds live in the proxy and the logic is swappable. Own the pointer, own everything. This issue covers delegatecall storage collisions (Audius), uninitialized implementations (Wormhole's other bug), UUPS selfdestruct bricking (Parity froze 513k ETH), and the 2025 mempool bots front-running initialize() on fresh proxies. Plus slither-check-upgradeability to catch it. https://www.kayssel.com/newsletter/issue-61/
#InfoSec #CyberSecurity #Web3 #SmartContracts #BugBounty #DeFi
Platforma HackerOne wprowadza obowiązkową weryfikację tożsamości w programach Bug Bounty https://sekurak.pl/platforma-hackerone-wprowadza-obowiazkowa-weryfikacje-tozsamosci-w-programach-bug-bounty/ #Wbiegu #Bugbounty #Hackerone #Hacking #Weryfikacja
Platforma HackerOne wprowadza obowiązkową weryfikację tożsamości w programach Bug Bounty
Platformy HackerOne raczej nie trzeba przedstawiać nikomu, kto interesuje się cyberbezpieczeństwem. To właśnie za jej pośrednictwem wielu hakerów zgłasza wykryte podatności, w zamian za co, oprócz uznania, otrzymują nagrody pieniężne. TLDR: Do tej pory istniała możliwość otrzymania nagrody, bez potrzeby ujawniania tożsamości. Stosując się jednak do obowiązujących regulacji, zwłaszcza tych...
#WBiegu #Bugbounty #Hackerone #Hacking #Weryfikacja
https://sekurak.pl/platforma-hackerone-wprowadza-obowiazkowa-weryfikacje-tozsamosci-w-programach-bug-bounty/
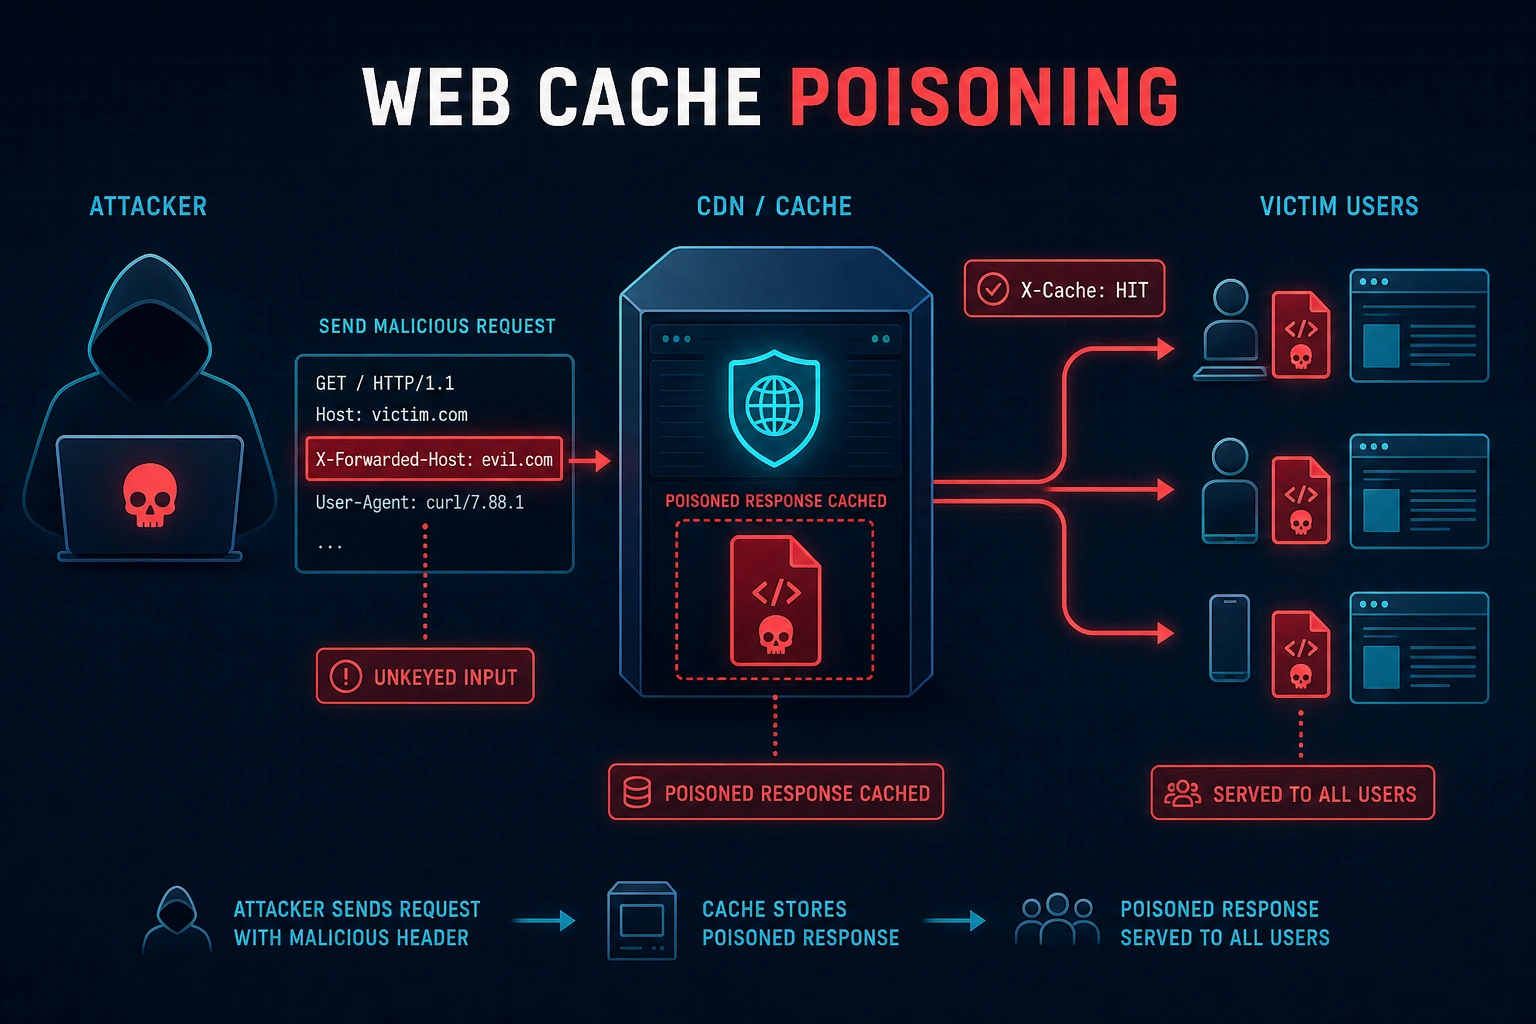
📢 How Web Cache Poisoning works — Complete Guide | Bug Bounty Course Day 29 of 60
Master web cache poisoning bug bounty 2026. Unkeyed headers, Vary header abuse, cache buster techniques, Burp Suite detection and real HackerOne payout examples.
🔗 https://securityelites.com/day-29-web-cache-poisoning-bug-bounty/
#ageheader #applicationsecurity #bugbounty
Found critical vulns in Lovense (the biggest sex toy company) affecting 11M+ users. They ignored researchers for 2+ years, then fixed in 2 days after public exposure. 🤦
What I found:
- Email disclosure via XMPP (username→email)
- Auth bypass (email→account takeover, no password)
History of ignoring researchers:
- 2017: First recorded case of someone reporting XMPP email leak.
- 2022: Someone else reports XMPP email leak, ignored
- Sept 2023: Krissy reports account takeover + different email leak via HTTP API, paid only $350
- 2024: Another person reports XMPP email leak AND Account Takeover vuln, offered 2 free sex toys (accepted for the meme)
- March 2025: I report account takeover + XMPP email leak, paid $3000 (after pushing for critical)
- Told me fix for email vuln needs 14 months because "legacy support" > user security (had 1-month fix ready)
- July 28: I go public
- July 30: Both fixed in 48 hours
Same bugs, different treatment. They lied to journalists saying it was fixed in June, tried to get me banned from HackerOne after giving permission to disclose.
News covered it but my blog has the full technical details: https://bobdahacker.com/blog/lovense-still-leaking-user-emails/
#InfoSec #BugBounty #ResponsibleDisclosure #Security #Vulnerability #IoT #cybersecurity
----------------
🛠️ Tool
===================
open·kritt is an open-source, self-hosted security research platform that orchestrates AI agents to find vulnerabilities in code. Rather than pointing a model at an entire repository and hoping for results, it breaks research into focused, well-defined tasks, runs them in parallel across AI agents, and combines output into validated, prioritized findings.
How it works
The core approach is decomposition. Full-repository scans with a single LLM prompt tend to produce noisy, unfocused results. open·kritt chains focused prompts into reusable security research playbooks (workflows). Each workflow defines a sequence of targeted analysis steps. Agents run these steps in parallel, and results are merged with automatic de-duplication and custom severity ranking.
Key capabilities
• Workflow builder: Chain focused prompts into reusable security research playbooks
• Scan execution: Analyze remote or local repositories and dependencies using Codex or Claude Code
• Finding validation: Post-scripts verify issues, build proofs of concept, produce reports
• Result prioritization: Custom severity rankers, consistent finding schema, automatic de-duplication
• Model flexibility: Bring your own model access via Codex, OpenAI, Anthropic, or OpenRouter
Technical details
The stack runs on Docker with Docker Compose, requiring Node.js 20 or newer. The CLI is repository-local with no separate install step. Default ports bind to 127.0.0.1, and the backend ships without application authentication. The documentation explicitly advises keeping the stack private.
Tool-enabled agents run as root inside disposable job containers, with writable repository copies and direct internet access. This allows agents to install tools, compile targets, run tests, and build proofs of concept. The threat model documentation recommends running open·kritt on a dedicated Docker host or VM, especially when scanning untrusted code.
Background
The Kritt team built this from real security research. Under the researcher name Blockian, they earned over $1,500,000 in bug-bounty payouts across platforms including Immunefi and HackenProof. open·kritt is the open-source version of the internal tool behind that work.
Limitations
No application-level authentication by default. Agents run as root in containers with internet access, requiring isolation awareness. The tool has not been independently verified for this writeup.
🔹 openkritt #tool #AI #vulnerability #bugbounty
🔗 Source: https://github.com/Kritt-ai/open-kritt
🙏 New Blog Post
The Pope's official prayer app has an IDOR that lets anyone pull user data for all 719,517 accounts. One GET request per user. No auth check.
What's exposed:
Email addressesNamesCountryDate of birth (they call it "borned_date" lol)Account role (it's "PRAYER" for everyone, obviously)
Also found:
Signup endpoint returns the email verification token in the response body, so you can verify accounts without accessing the inboxTheir verification emails fail their own domain's authentication requirements
Reported January 3rd. Emailed 9 people. A journalist also contacted them. Zero responses. Still live six months later. Vow of silence I guess.
Full writeup: https://bobdahacker.com/blog/click-to-pray
#InfoSec #BugBounty #ResponsibleDisclosure #IDOR #Security #CyberSecurity #Privacy #DataExposure #ClickToPray #Vatican #APISecurity
GitHub updates its bug bounty program on July 27, cutting public payouts while moving maximum rewards to an invite-only VIP program.
#GitHub #BugBounty #Cybersecurity #InfoSec #SoftwareSecurity
https://meterpreter.org/github-bug-bounty-payouts/?utm_source=mastodon&utm_medium=jetpack_social
GitHub baut sein Bug-Bounty-Programm um: Neues VIP-Modell und feste Prämien
m Zentrum der Reform steht eine engere Zusammenarbeit mit Sicherheitsforschern sowie eine klarere Struktur bei der Vergütung gemeldeter Schwachstellen.
https://www.all-about-security.de/github-baut-sein-bug-bounty-programm-um-neues-vip-modell-und-feste-praemien/
#github #bugbounty
new writeup: three bugs in vinext's alpha, cloudflare's next.js reimplementation that one engineer built with an AI model in about a week for roughly $1,100 in tokens.
the good one: vinext checks middleware matchers against the path with the i18n locale prefix still on it, then strips the locale when it resolves the route. /fr/dashboard misses /dashboard/:path*, the auth middleware never runs, and the router serves /dashboard anyway.
also a middleware header allowlist that is really a merge, and reflected XSS via unescaped attribute names in the next/head serializer. reported in february, cloudflare fixed all three.
https://moltenbit.net/posts/three-bugs-in-cloudflares-vinext-alpha/
#infosec #appsec #cloudflare #nextjs #bugbounty #cybersecurity #security
Discover how the new GitHub bug bounty program impacts researchers. The platform replaces floating ranges with fixed payouts and a lucrative VIP tier.
#GitHub #BugBounty #Cybersecurity #Infosec #VIPProgram
https://securityonline.info/github-bug-bounty-program/?utm_source=mastodon&utm_medium=jetpack_social
🤖 OpenAI scored an own goal with HuggingFace attack, showing how ...
📝 OPINION OpenAI ...
https://www.theregister.com/ai-and-ml/2026/07/23/openai-scored-an-own-goal-with-huggingface-attack-showing-how-open-chinese-models-are-winning/5276699
📰 www.theregister.com - Articles
#AI #BugBounty
Restructuring GitHub's bug bounty program
https://github.blog/security/next-chapter-restructuring-githubs-bug-bounty-program/
#HackerNews #Tech #BugBounty
🔍 The between-reports problem: why security teams miss what attackers see
📝 What you will learn Why faster discovery and higher volume can still leave teams blind be...
https://www.intigriti.com/blog/business-insights/why-security-teams-miss-what-attackers-see
📰 Intigriti
#CVE #BugBounty