Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Volexity :verified:

@volexity@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Volexity is a cybersecurity firm founded by the pioneers of memory forensics. Volexity delivers transformative solutions & services to governments & organizations worldwide, increasing enterprise visibility & facilitating rapid intrusion detection.

671 Followers
6 Following
7 Posts
Joined November 16, 2022
Website:
https://www.volexity.com
Blog:
https://www.volexity.com/blog
Twitter:
https://twitter.com/Volexity
LinkedIn:
https://www.linkedin.com/company/volexity
Open post
Volexity :verified: @volexity@infosec.exchange
· 2mo ago
@volexity@infosec.exchange has published details on a recent incident response investigation involving the exploitation of multiple #0day vulnerabilities in SonicWall SMA 1000 series appliances. Volexity attributes this activity to a threat actor it tracks as UTA0533, with the earliest signs of compromise dating back to June 22, 2026. SonicWall has released patches (versions 12.4.3-03453 and 12.5.0-02835) following their July 14 public disclosure. Organizations using affected SMA 1000 series devices should upgrade immediately. Read our full technical breakdown, including the vulnerability workflow, malware analysis, and IOCs: https://www.volexity.com/blog/2026/07/17/proxying-to-compromise-sonicwall-secure-mobile-access-0-day-exploitation/ #dfir #memoryforensics #threatintel
Proxying to Compromise: SonicWall Secure Mobile Access 0-day Exploitation
Volexity

Proxying to Compromise: SonicWall Secure Mobile Access 0-day Exploitation

In early July 2026, Volexity was engaged to perform an incident response investigation where it discovered a threat actor had successfully compromised multiple of the customer's SonicWall Secure Mobile Access (SMA) VPN appliances through a chain of multiple zero-day exploits in the devices. The initial compromise was discovered after suspect authentication and lateral movement attempts were observed from the SonicWall SMA devices.

1
0
0
0
Open post
Volexity :verified: @volexity@infosec.exchange
· 41mo ago

The @volexity@infosec.exchange #threatintel team continues to see various #threatactors using Microsoft OneNote (.one) files to distribute #malware, sometimes password-protecting them to avoid analysis. We have updated our one-extract tool to support password-encrypted notebooks: https://github.com/volexity/threat-intel/tree/main/tools/one-extract.

#dfir

infosec.exchange

Infosec Exchange

12
0
13
0
Open post
Volexity :verified: @volexity@infosec.exchange
· 2mo ago
@volexity@infosec.exchange is heading to Las Vegas! Members of our leadership, development, engineering & threat intelligence teams will be on site August 4–6. If you would like to connect to discuss the latest in #DFIR, #memoryforensics, or the current threat landscape, let us know when you’d like to meet: https://www.volexity.com/contact/meet-up-in-vegas/
Schedule a Meeting with Volexity in Las Vegas
Volexity

Schedule a Meeting with Volexity in Las Vegas

If you would like to schedule time with members of Volexity's leadership, development, engineering, or threat intelligence teams to learn more about our recent investigations and next-generation memory forensics, please fill out the contact form. Suggest the dates/times you’d like to connect, and we will be in touch.

0
0
0
1
Open post
Volexity :verified: @volexity@infosec.exchange
· 2mo ago
@volexity@infosec.exchange is hiring!   Join a team that develops concrete solutions to the most challenging real-world problems. Whether your focus is bringing new products to market or delivering cybersecurity services to customers worldwide, the work you do here helps real people and moves the industry forward.   See how you can plug in: https://www.volexity.com/company/careers/   #dfir #hiring #memoryforensics #threatintel #cybersecurity
Careers
Volexity

Careers

Join a team where your contributions will have an impact on cybersecurity & develop concrete solutions to the most challenging real-world cyber problems.

0
0
0
0
Open post
Volexity :verified: @volexity@infosec.exchange
· 2mo ago
RE: https://infosec.exchange/@volexity/116958370224493580 Heading to Las Vegas next week? Connect with our team to discuss the latest in #DFIR, #memoryforensics, active threat actor campaigns we're tracking, and more! Let us know when you'd like to meet: https://www.volexity.com/contact/meet-up-in-vegas/
Open quoted post
Quoting
Volexity :verified:
@volexity@infosec.exchange
@volexity@infosec.exchange is heading to Las Vegas! Members of our leadership, development, engineering & threat intelligence teams will be on site August 4–6. If you would like to connect to discuss the latest in #DFIR, #memoryforensics, or the current threat landscape, let us know when you’d like to meet: https://www.volexity.com/contact/meet-up-in-vegas/
Open quoted post
infosec.exchange

Volexity :verified:: "@volexity is heading to Las Vegas! Members of our…" - Infosec Exchange

0
0
0
0
Open post
Volexity :verified: @volexity@infosec.exchange
· 2w ago
Following @volexity@infosec.exchange’s September 9 blog post on two Chinese APT actors chaining 0-days in Chrome (CVE-2026-85046, CVE-2026-87491) & Windows (CVE-2026-85880), Volexity discovered another threat actor, UTA0565, had been using the same exploits on Sept 3-4, 2026, while they were still unpatched.   UTA0565 used multiple fake websites, posing as media organizations and an NGO, to run a more customized version of the exploit framework than previously documented instances. The payload delivered was a new custom malware family, CLEANGULP, obfuscated using control flow flattening.   Full details and IOCs can be found here: https://www.volexity.com/blog/2026/09/21/mind-the-patch-gap-part-2-fake-websites-used-to-deploy-chrome-windows-0-day-exploits/   #DFIR #threatintel
Mind the (Patch) Gap, Part 2: Fake Websites Used to Deploy Chrome & Windows 0-Day Exploits
Volexity

Mind the (Patch) Gap, Part 2: Fake Websites Used to Deploy Chrome & Windows 0-Day Exploits

On September 9, 2026, Volexity published a blog post detailing the simultaneous use of multiple chained zero-day exploits in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Microsoft Windows (CVE-2026-85880) by two different Chinese advanced persistent threat (APT) actors. Shortly after that blog post was published, Volexity discovered additional campaigns—this time from a third Chinese threat actor, tracked by Volexity under the alias UTA0565—that used the same chained exploits on September

0
0
0
0
Open post
Volexity :verified: @volexity@infosec.exchange
· 1w ago
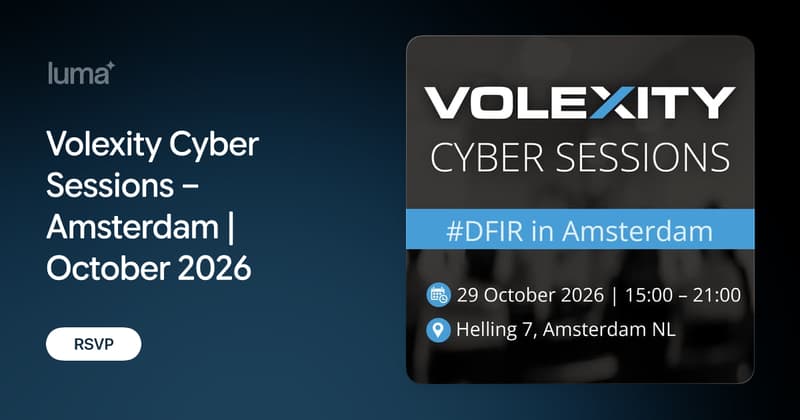
State-aligned threat actors continue to evolve their operations and infrastructure tactics. Feike Hacquebord will be speaking at our upcoming Volexity Cyber Sessions in Amsterdam (October 29) about APT campaigns by Russia-, China-, and DPRK-aligned actors targeting Europe in 2026. Feike will examine China-aligned residential proxy networks built on compromised IoT devices, DPRK-aligned operations run from static Russian IP addresses and hundreds of VPS servers, and a decade of Pawn Storm (APT28/Fancy Bear) activity. He will also explain how domestic Chinese AI capabilities have reduced China-aligned actors' dependence on frontier Western models. Seating is limited. Register now to secure your spot: https://luma.com/0qtkw49c #dfir #threatintel #apt
Volexity Cyber Sessions – Amsterdam | October 2026 · Luma
luma.com

Volexity Cyber Sessions – Amsterdam | October 2026 · Luma

Join Us in Amsterdam We are excited to announce our first Volexity Cyber Sessions meetup in Amsterdam! Seating is limited for this in-person event. Register…

0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 21:08:41 UTC