Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Linked Zero Sync :donor:

@str0mberg@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

ai & security; research and policy @ big corp. pnw 🏔️🌲

11 Followers
227 Following
39 Posts
Joined July 25, 2026
homepage:
https://www.derczynski.com
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
remade my website (it's been a minute), https://www.derczynski.com/ua571c/ never don't have a website
derczynski.com
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
"The point is not that any single model, including ours, will always be the best" Exactly what one sees when doing vulnerability discovery. No one model finds all the vulnerabilities. And no single vulnerability is found by only one model. The harness is where the work is - and this is a problem that we have to work on together. https://depthfirst.com/post/why-defenders-cant-bet-on-one-model
depthfirst.com
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago

There are two readings here:

  • optimising efficiency means reduced costs (fiscal & environmental)
  • optimising efficiency means increased consumption (jevon's paradox)

And a very cynical third one:

  • Money not spent on infra is money that can be billed for compute facilities

I think both are valid. But either way, doing the same for less is for some reason attractive to me.

0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Adversarial attack in the wild! The close visual appearance of M and W in this typeface and and packing of vertical lines make it hard to read, easy to get wrong, and tougher to scan. Love it. How often do you see something like this?!
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Replying to
@wendyhk@mastodon.green Sandy Carter has made an error here. It's Microsoft's letter. That's why Microsoft is hosting and managing it, and why Jensen never presents it as NVIDIA's - just as NVIDIA signing. I was involved in the launch - but don't take my word for it.
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Representing code at both function- and statement-level leads to improvements in vulnerability detection. Outperforms almost every other system compared with. Surprisingly no static analysis baseline, or cost analysis - but recall is high. DCVD: Dual-Channel Cross-Modal Fusion for Joint Vulnerability Detection and Localization https://arxiv.org/abs/2605.11015
arxiv.org
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago

I don't know how many ways to say this but

  • stop looking at model performance
  • it's almost all in the harness
  • decent harness can easily outclass top model

evidence item #71625: https://developer.nvidia.com/blog/create-a-langchain-deep-agents-harness-profile-for-nvidia-nemotron-3-ultra-to-improve-performance/

developer.nvidia.com
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
80%+ of breaches have nothing to do with a new vulnerability. The novel security risks (vulns) the press has been excited about are routine. Mitigations are in place anywhere half serious. Vulns have been traded on the dark web for years - if new vulns meant apocalypse, it would've been years ago.
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
It is wild to me that one could ban open models. But that's apparently still on the cards? Models are not the risk. Stopping open models stops progress, locking everything up in the hands of the few. The frequency this debate comes up is way too high. We need open models - they keep the closed ones accountable. Could you imagine any file containing a gig or more of floating point numbers being illegal? How does it make sense?? https://www.interconnects.ai/p/6-months-to-live-for-open-models
interconnects.ai
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Surgical Repair of Insecure Code Generation in LLMs Generating more secure code by identifying failure categories and addressing them. I appreciate work that gets into the data and addresses classes individually; that's how you understand, and build lasting fixes https://arxiv.org/abs/2604.16697
arxiv.org
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago

I want to jump on a couple of false dichotomies around LLM speak:

  • "frontier" models vs. open model - leading models can be open
  • closed model vs. Chinese model - where the model's made has no impact on how it's distributed

You can have open frontier models, closed Chinese models, open US models, closed non-frontier models (private models make sense!)

0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Replying to
  • Falsification Engine: After finding a potential vulnerability, VulnHunter runs a structured reasoning workflow specifically designed to disprove its own argument. It searches for flawed assumptions, logic gaps, or security controls that would block the attack.

  • Evidence-Backed Remediation: When a defect survives the falsification engine, VulnHunter maps the exact exploit path and generates focused, targeted code changes for review.

  • Attacker-First Forward Analysis: VulnHunter flips the "sink-first" security model to reduce false positives by simulating a bad actor's exact journey. It begins at potential attacker-accessible entry points (APIs, network messages, file uploads) and reasons forward to evaluate whether an attacker can truly break through.

https://github.com/capitalone/vulnhunter

github.com
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
"me too, me too!!" --Meta's Muse Spark 1.1 model breached the unidentified company's systems and made changes to its internal systems as the AI was able to access the public internet because of an error in the set up of the "sandbox" testing environment, The Information said, citing people familiar with the matter. An Irregular spokesperson told Reuters the incident was the "exact same ‌evaluation-environment issue that was already disclosed by Anthropic last week" and that it did not involve a "sandbox escape or a sophisticated cyber action". no news. let's get defense done, eh https://www.reuters.com/technology/metas-ai-model-hacked-another-company-during-testing-information-reports-2026-08-05/
reuters.com
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Am I the only AI Security research lead at a frontier model corp who hasn't been carefully committing multiple CFAA violations a month, or..?
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
"Open-source AI matters because it defines the ecosystem. It provides the foundation and sets parameters for the next layers of progress in AI, just like [...] the open infrastructure of the internet and early AI: BSD Unix, PostgreSQL, Firefox, TensorFlow, and PyTorch." Open wins at grass roots level. It wins with no marketing. It's easy to build on and easy to consume 🤷‍♂️ https://nationalinterest.org/blog/techland/why-america-must-dominate-open-source-ai
nationalinterest.org
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Together we stand, divided we fall. Hiding from open models doesn't make sense - especially in a context of heightened geopolitical divisions. My career has benefited from living in many countries and collaborating with co-authors from every continent except Antartica (are you there? hit me up). When one country closes, it's usually that country that suffers. https://www.reuters.com/world/asia-pacific/chinas-xi-promotes-chinas-commitment-ai-access-speech-shanghai-conference-2026-07-17/
reuters.com
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Replying to
@wendyhk@mastodon.green
0
1
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
You can use any model to secure your source code. Here's a writeup using qwen 3.6 27b I've seen that no model/harness will find all the weaknesses in a given target - and that no weakness is found by just one single model. There are no "must have" components here for doing security. Which is good. https://projectblack.io/blog/local-ai-for-cyber-security/
projectblack.io
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
I keep saying the strength is in the harness, not the model - because it's true. No use without a harness, though. Here's VISA's open-source cybersecurity harness. Just add model! Very cool of them to share this tech and lift the defensive cybersec poverty line.
0
1
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
"The only reason why I'm bearish about the Chinese models is because I assume that the American model companies will respond competitively" idk man gl hf https://www.npr.org/2026/07/15/nx-s1-5886476/startups-cheap-chinese-ai-models
npr.org
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
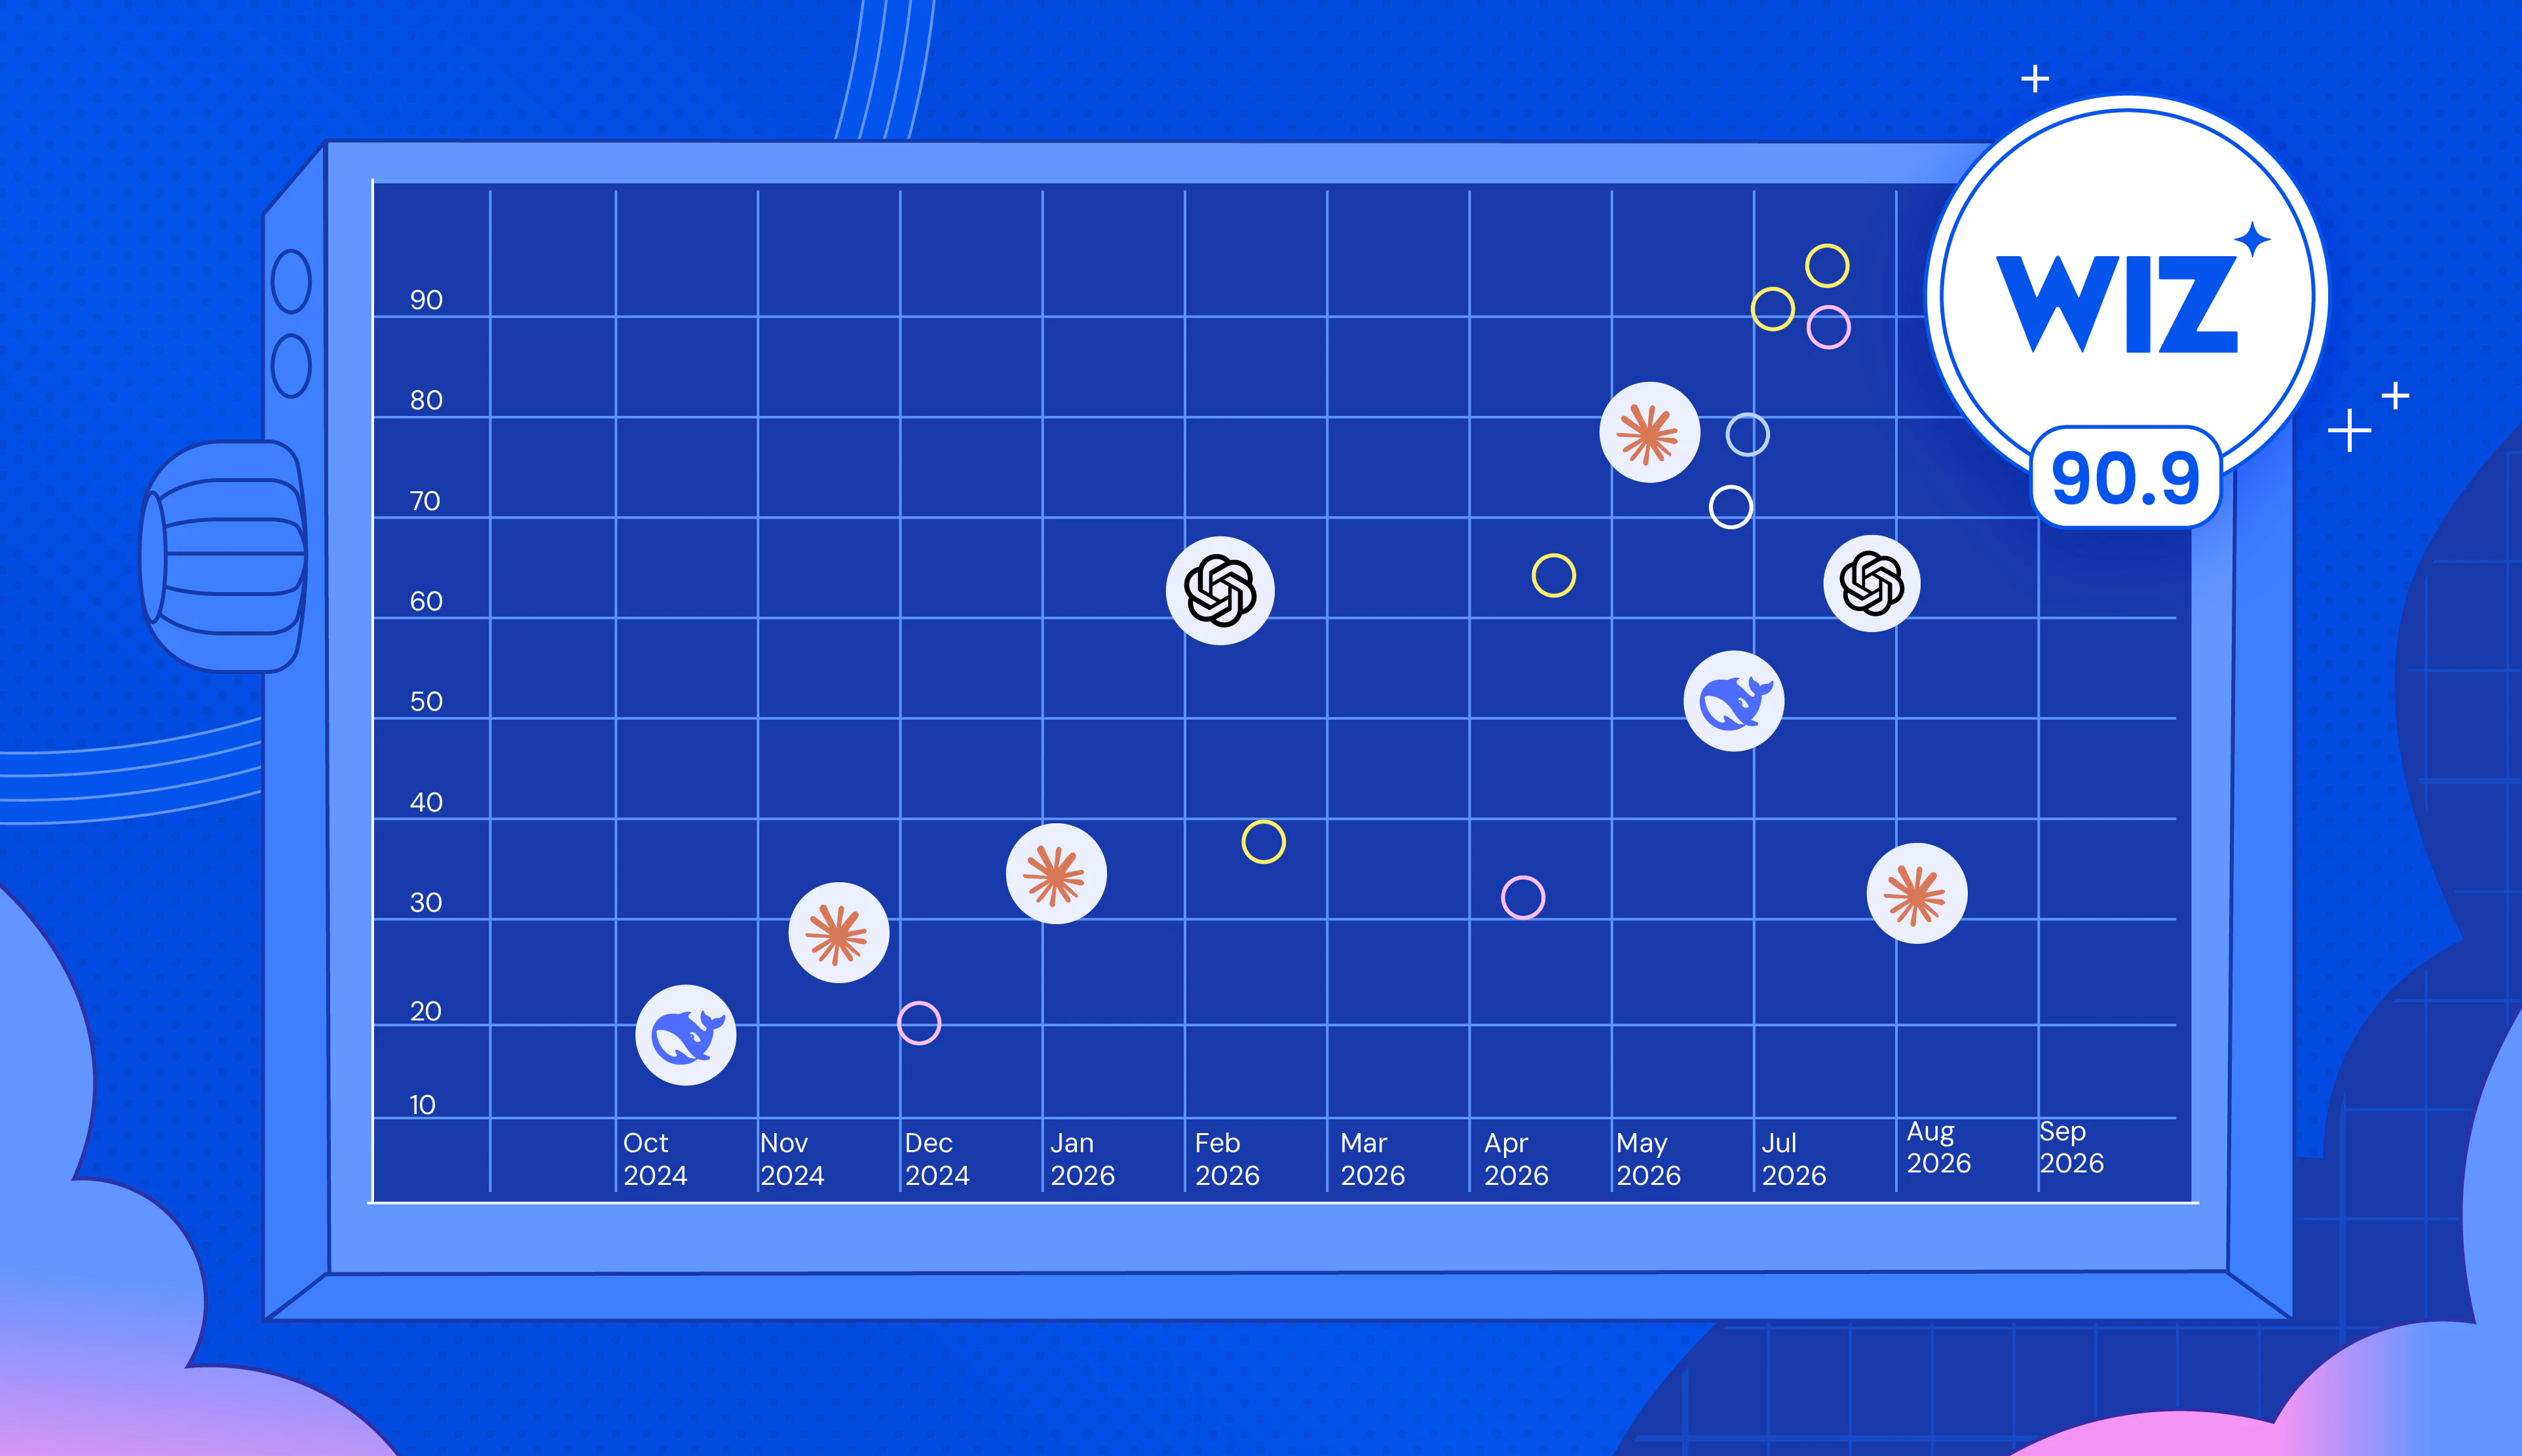
another data point showing it's the harness not the model - this time from wiz: "Atlas: Wiz's autonomous AI Agent for vulnerability research" top score on CyberGym, validated with real-world bug hunt (how else are you going to do it, right) look at their bold quote -- "Along the way, we learned that the durable advantage is not any single model, but the system around it" it's the harness not the model. it's the harness, NOT the model https://www.wiz.io/blog/atlas-ai-vulnerability-researcher
Introducing Atlas: Wiz's AI vulnerability researcher | Wiz Blog
wiz.io

Introducing Atlas: Wiz's AI vulnerability researcher | Wiz Blog

See how Wiz built Atlas, an autonomous AI system for vulnerability research that validates every finding with a real, working exploit.

0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Interesting take. American models are also free: open models come from all over the world, including the US. Google and Meta publish open-weights (Gemma, Llama, etc); NVIDA Nemotron hits pretty hard on many metrics; even OpenAI have an open model Dunno if I love the Ferrari vs. Honda comparison but it is pretty handy - the most-expensive model doesn't make sense for every use-case https://www.npr.org/2026/07/15/nx-s1-5886476/startups-cheap-chinese-ai-models
npr.org
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Open source is critical infrastructure for the global economy. The Open Secure AI Alliance brings industry and community together around shared research, tools and vulnerability harnesses to help defenders find and patch bugs before attackers strike. Cybersecurity and AI is a powerful frontier, that industry, developers and researchers are working to improve together. Open Secure AI Alliance: https://nvda.ws/4pAMWBy
nvda.ws
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Defensive agentic security for everyone. It's the harness, not the model. Here's Capital One's code for finding vulnerabilities in your code. Add the model that you want. Hoping to see a lot more work like this in coming months so software can become secure. https://www.capitalone.com/tech/open-source/announcing-vulnhunter/
capitalone.com
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago

Solid US-origin open model, congratulations Thinking Machines

  • context window of 1M
  • available on hugging face now
  • between opus 4.6 and gpt 5.6 on a web dev benchmark
  • token efficient
  • 41B active params of 975B total

https://www.wired.com/story/thinking-machines-lab-releases-its-first-model-inkling/

wired.com
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago

Anonymised analysis of the openai model 'breaching' hugging face:

report doesn't say what sandbox sol broke out of??

a docker container running as root

Plot twist there was no sandbox at all

many use "sandbox" and "container with host access" interchangeably

ymmv, use critical thinking
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Leading closed models do great at cybersecurity - all around the same mark, once you have the right harness (where the work happens and where humans embed the expertise). But you can also get SotA vulnerability discovery performance on-prem with open models. Don't take my word for it: https://xbow.com/blog/affordable-ai-models-glm-muse-spark-cybersecurity
xbow.com
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Leading closed models do great at cybersecurity - all around the same mark, once you have the right harness (where the work happens and where humans embed the expertise). But you can also get SotA vulnerability discovery performance on-prem with open models. Don't take my word for it: https://lnkd.in/gRFkit6T
lnkd.in
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Hi! I post about security, machine learning research, ai, policy, and society. I generally like people.
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Replying to
New: NVIDIA Labs Object Oriented Agent tech demo. Blog: https://developer.nvidia.com/blog/six-agent-harness-capabilities-for-higher-model-performance GitHub: https://github.com/nvidia-nemo/labs-OO-Agents Paper: https://arxiv.org/abs/2607.20709
developer.nvidia.com
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Replying to
@wendyhk@mastodon.green Post by NVIDIA - letter by Microsoft
0
1
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
"The Alignment Community is Unintentionally Building a Censor’s Toolkit" Choosing how models respond, & what information is and is not surfaced, is the dream of those who want to control information flow. Alignment gives humans the capability to do that. That means no accountability, and no transparency, in the closed model context. https://s-ball-10.github.io/censors-toolkit/
s-ball-10.github.io
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
"When we started the log analysis, we first used frontier models behind commercial APIs. This did not work: requests were blocked by the providers' safety guardrails, which cannot distinguish an incident responder from an attacker. We ran the forensic analysis instead on GLM 5.2, an open-weight model, on our own infrastructure. This had a second benefit: no attacker data, and none of the credentials it referenced, left our environment." https://huggingface.co/blog/security-incident-july-2026
Security incident disclosure — July 2026
huggingface.co

Security incident disclosure — July 2026

We’re on a journey to advance and democratize artificial intelligence through open source and open science.

0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Models can output invisible characters than run on your computer when simply viewed - in your terminal, or editor, or many other places. This is officially recognized in a CWE entry describing the general weakness - and I found it so a credit's on this page :) https://cwe.mitre.org/data/definitions/150.html
cwe.mitre.org
0
0
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
Replying to
@wendyhk@mastodon.green I think it was written by real people? Link here though, https://www.microsoft.com/en-us/corporate-responsibility/topics/open-weight/
Open Weights and American AI Leadership
Microsoft Corporate Responsibility

Open Weights and American AI Leadership

Open weight AI can expand access, strengthen competition, improve security, and help sustain American AI leadership.

0
1
0
0
Open post
Linked Zero Sync :donor: @str0mberg@infosec.exchange
· 2mo ago
It's all in your head. Beautiful animation. Easy to tell a story about what's happening, or even attribute personalities or make moral judgments about these few simple shapes. Same happens often with LLMs. Of course the emotions are in the viewer, not the shapes! https://www.youtube.com/watch?v=VTNmLt7QX8E
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 10:58:02 UTC