Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Adrian —dangerously-skip-permissions Sanabria

@sawaba@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

🎙️ Enterprise Weekly Podcast
🤝 Founder @bsidesknoxville@infosec.exchange
🗣️ Faculty @IANS_Security
🕵️ Security Research
🍳 Cooking
⛰️ Hiking
🏎️ F1

"I rant with data!"

2013 Followers
296 Following
50 Posts
Joined November 04, 2022
🤝 BSides Knoxville:
https://bsidesknoxville.com
🎙️ Enterprise Security Weekly:
https://securityweekly.com/esw
📚️ Cybersecurity Canon:
https://cybercanon.org
💣️ Destroyed by Breach Dataset:
https://docs.google.com/spreadsheets/d/15CTPcgZQenWKDLDTQ2ibveUM4i7Of_n20TzdTi23xcg/edit?usp=sharing
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3d ago
I needed AI to express my experience at Washington Dulles airport I have seriously never encountered so many escalators at one time, and I've been in probably over 100 airports
3
2
1
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 4w ago
Replying to
@GossiTheDog@cyberplace.social I’ve been advising enterprises to focus more on patching routinely and closing gaps with unmanaged assets, rather than putting effort into patching faster or more frequently after all, ransomware is one of the most disruptive things you can do to a business, but patching is not far behind
6
1
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2w ago
Replying to
@GossiTheDog@cyberplace.social If you use MoveIT Transfer and you’re not watching software updates like a hawk, I wouldn’t want to see what the rest of your infrastructure looks like 😬
2
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3w ago
Rick Howard and I get to interview some famous cybersecurity authors this week at the Open Source Security Summit! Super excited I get to interview @JosephMenn@infosec.exchange about Cult of the Dead Cow. This is a hall-of-fame book and a surreal read for me, having been around for some of the events mentioned and interacted with some of the folks mentioned. It's a virtual event and free to attend, so come check it out Thursday morning! #opensourcesecuritysummithttps://opensourcesecuritysummit.com/
opensourcesecuritysummit.com
2
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@hacks4pancakes@infosec.exchange it is rough out there. I haven't had a mentee in a while and I'm not sure how much I could help them in this job market.
13
2
2
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
PSA Nothing makes us feel older than downloading a .ics file and manually importing it into Google Calendar. Please stop making us do this.
16
2
2
1
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@hacks4pancakes@infosec.exchange having an intern is a bit of an experiment, but if it works out, this is how I'm going to mentor going forward, I'm literally going to hire and pay people to do research for me to get them started in cyber
12
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Heck, even my Mastodon DMs are wild
11
0
2
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@hacks4pancakes@infosec.exchange well, I take that back - I DO have an intern and he's doing really well, may already have a lead on a full time job at a security startup, but he's a bit of a unicorn - he got all his certs before he finished high school and now he's building threat intel tools
9
1
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Happy to share that I will be speaking at BSides Las Vegas this year! My talk is "Destroyed by Breach: Corporate casualties of cybersecurity failures" Common Ground, Tuesday 10:00-11:00, Florentine F I'll be at Black Hat and DEF CON as well. Let me know if you want to meet up!
9
0
1
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3w ago
Replying to
@wendynather@infosec.exchange hope you had some time for coxinha as well!
1
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3w ago
Replying to
@taviso@social.sdf.org except this Cisco vuln is due to SQL injection! Something that everyone knew how to fix over TWENTY years ago.
1
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to on mastodon.social
@Viss@mastodon.social @cR0w@infosec.exchange Hear me out What if we ENCRYPTED the drone? With quantum encryption Would people still be able to hear it?
4
3
1
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
This week on Enterprise Security Weekly: O'Shea Bowens explores MCP from a network security lensJeremiah Grossman drops a serious truth bomb - the evidence doesn't support all the fervor around AI vulnerability discoveryIn the news, we discuss the future of AI model use and the HuggingFace breach We went a little long on this one, but I think it was well worth it. https://www.youtube.com/watch?v=Em3FoAU4AE8

Exploring AI Network Protocols; Vulnerability Truths and Guarantees; and the News - ESW #469

3
0
1
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 1mo ago
Behold my restraint All these gadgets could have come with me to #hackersummercamp but I left them home because I have so much restraint
1
1
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
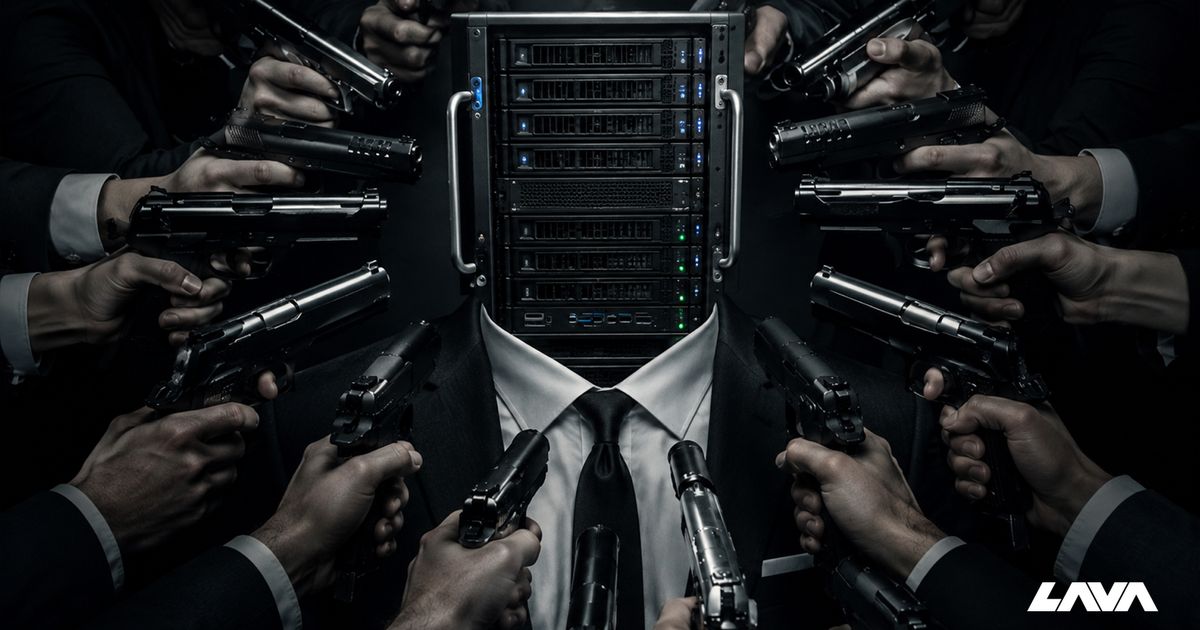
WTAF is the image on this blog post??? Who in corporate marketing thought this was a good image to use? https://lavahq.io/research/bmc-exposure-alert
How We Hacked Thousands of Data Centers in Minutes Using a 20-Year-Old Vulnerability
Lava

How We Hacked Thousands of Data Centers in Minutes Using a 20-Year-Old Vulnerability

A 20-year-old vulnerability gave us access to bare-metal servers - and a foothold in the no man’s land of data center infrastructure.

1
1
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@theorangetheme@en.osm.town @Viss@mastodon.social @cR0w@infosec.exchange haha, see what you did there
1
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago

I don't often visit general news or local news websites, but the headlines out there are wild, y'all

1
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago

This voiceover artist nails one of the most annoying trends in cybersecurity right now

https://www.instagram.com/reel/Da_K-z8hdsW/?igsh=MXMxMWVjamQ1NjlreA==

instagram.com
1
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@GossiTheDog@cyberplace.social I don’t know why they’d be worried- they’re marketing it as an AI laptop and there is no AI benchmarking in the review
1
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@Javvad@infosec.exchange tell them the whole world wasn’t in HD yet
1
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@josephcox@infosec.exchange you had one job
1
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@Javvad@infosec.exchange oh shit, I have a collection of hundreds of old computer software boxes, mostly games… new project
1
2
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@wendynather@infosec.exchange Legend has it that his long-time guitar tech caught the guitar, BTW, and handed it to Oprah, who was in the audience.
1
1
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@wendynather@infosec.exchange The story behind this is AMAZING Centers around Prince not getting a spot on Rolling Stone's top 100 guitarists of all time list https://www.guitarplayer.com/news/prince-while-my-guitar-gently-weeps-solo-act-of-revenge
guitarplayer.com
1
4
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3w ago
Replying to
My friend Stephen Hilt, a researcher at Trend, always has some interesting research to share. Words of the Wicked: How Language Divides and Unites Cybercriminals gives a rare look into how language influences groups and communities of cybercriminals. https://www.youtube.com/watch?v=83nDf9MeDNo

Stephen Hilt - Words of the Wicked

0
1
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2w ago
I don't need AGI, I just need an AI agent smart enough to understand that: a podcasting task goes in the podcasting projectit should be assigned to me, because there's no one else to assign it to
0
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3w ago
Replying to
A Fortinet flaw that entered the exploited catalog on September 9 had carried its identifier since February 2025. A ha! A Fortinet flaw! We’re talking about vulnerabilities! Finally, a shred of context. The Fortinet vulnerability “entered the exploited catalog” <- maybe we’re talking about CISA KEV? Maybe CHQ has its own catalog? Maybe it’s in the Structural Conditions Registry? I’ve got to make a lot of assumptions here, but the next bit mentions an identifier from Feb 2025. The only explanation I can think of is that there’s a Fortinet vulnerabilities with a CVE coined in Feb 2025, but is just now getting actively exploited. So we’re talking about a 19 month gap between disclosure and exploitation? Nineteen months separate the reservation of the identifier from federal confirmation of exploitation, and this board's published test was twelve. Ah ha, yes! 19 months. We’re onto something. I have no idea what “this board’s published test was twelve” means. The rule ran, and the rating moved. I have no idea.
0
1
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@flyingpenguin@infosec.exchange people act like the AI is a toddler and we should applaud when it puts away one of its 17 toys and says it cleaned up its room
0
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3w ago
Replying to
My friend and mentor, @wendynather@infosec.exchange, keynoted the event and also sat front row for my talk - always lovely to have support in the front row! Her keynote, Brother can you spare a token explores how AI affects the security poverty line. https://www.youtube.com/watch?v=mzEotI8a2I0

Wendy Nather - Brother, Can You Spare A Token?

0
3
1
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@vor@lgbtqia.space @protonprivacy@mastodon.social I'm aware, it is one of the three calendars I actively use and have to sync together
0
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3w ago
Replying to
Let’s break down this first paragraph. CHQ maintains ratings on a standing set of structural security conditions. CHQ is the website. Okay. What is a standing set of structural security conditions? I have no idea. Why does the set need to be standing? Why are the conditions structural? Couldn’t you just say “CHQ maintains ratings on a set of security conditions?” Is AI trying to ‘juice’ the token use here so you needlessly pay extra? Each rating reflects the current maturity and confirmation of a condition, not a forecast. Nobody said it was a forecast, why so defensive? So we’ve got ratings that are based on maturity and confirmation that some condition is in some unmentioned state? Conditions carry their permanent identifiers from the public CHQ Structural Conditions Registry, where dated definitions and falsification criteria are maintained. Ah, conditions carry permanent identifiers from the public registry. So you’re telling us that each condition, of which there could be several it sounds like, gets an identifier. Like 0001, 0002, 0003? Why is this important for us to know? Why even mention this? It’s more useful to know that there is a Structural Conditions Registry, where definitions and criteria are maintained. I have no idea what this means, but hey, the definitions are DATED! The report leads with what changed; the full board follows. This page is the report? Or is the report elsewhere? Is the report in the Structural Conditions Registry? And the report tells us what changed? The full board follows? Board of what? Reports? Conditions? Criteria? Conditions? Did I already say Conditions? What are words, even? It isn’t until TWO PARAGRAPHS LATER that we find the words “a Fortinet flaw” strung together. Our first clue as to what the topic for this whole post (newsletter? article? report? board?) is. I’m actually impressed. This whole thing reads like a Monty Python sketch where the goal is to make something as unreadable as possible.
0
3
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@flyingpenguin@infosec.exchange the most dangerous game energy
0
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@wendynather@infosec.exchange if we have a chance in Vegas, we should raise a glass to all our respective little weirdos
0
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3w ago
Replying to
I cannot go further. Just the title and first 3 paragraphs exhausted me. There’s no context for the topic, or for features of the website it is referring to. It just assumes you know what it knows. It’s like your 5 year old getting home from their first day at Kindergarden trying to tell you all 350 things that happened that day, in no particular order, after consuming a bag full of pixie sticks. It isn’t using recognizable industry terms for common things. It isn’t consistent with the terms it is using. It includes extra words and details that are completely unnecessary, they only serve to make the reading more difficult. It’s clearly talking about vulnerabilities, but there are no CVEs present. There is clearly some structure around this registry and the ratings, but it provides no guide, explanation, or links to additional information that might shed some light on what any of this means. Is this superintelligence? Is this AGI? Is this why we’re laying people off? IS THIS YOUR GOD, AI-FIRST BUSINESSES? Did someone really pay for tokens to generate this?
0
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3w ago
Replying to
@adamshostack@infosec.exchange @sambowne@infosec.exchange hahaha, about time
0
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3w ago
Replying to
@taviso@social.sdf.org it was over a decade ago, here's the link if you want to feel super old and tired along with me https://projectzero.google/2016/06/how-to-compromise-enterprise-endpoint.html
How to Compromise the Enterprise Endpoint
projectzero.google

How to Compromise the Enterprise Endpoint

Posted by Tavis Ormandy.Symantec is a popular vendor in the enterprise security market, their fla...

0
1
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3w ago
Replying to
There are many more that I missed the day of the event and look forward to checking out now that they're all published! @BSidesKnoxville@www.youtube.com Follow @bsidesknoxville@infosec.exchange here and on YouTube!
YouTube

BSides Knoxville

Share your videos with friends, family, and the world

0
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@jerry@infosec.exchange I am a little concerned about what happens when someone points claude.
0
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 1w ago
Replying to
@g@irrelephant.co hey, but shrink was down 4.2% last month!
0
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2w ago
Replying to
We ended up going! Delayed because of weather and we went in at half time.
0
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3w ago
Replying to
Friend and repeat BSides Knoxville speaker Chris Craig delighted me with his presentation, titled Stacking the Deck. It was not only chock full of useful, actionable information on how to use AI for offensive security and how he builds harnesses, but was also highly successful in using a deck-building game metaphor. Not only was the metaphor fun, Chris decided that instead of using AI-generated images for his slides, he'd draw them himself, which was chef's kiss for me. I wish more people put this level of thought and love into the talks they give. https://www.youtube.com/watch?v=I4CuKbP0oo4

Christopher Craig - Stacking the Deck

0
2
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@adamshostack@infosec.exchange invite that opens directly in your calendar of choice or send a calendar invite to my email
0
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 3w ago
Replying to
OKAY. Next paragraph. SC-2026-006 · Exploitation Precedes Defender Awareness: rating under review after the criterion supporting this cycle's scheduled upgrade failed construct validation. The upgrade action is voided. Prior state, STRENGTHENING, stands. I got nothing. Why is STRENGTHENING in all caps, like it is one of several selectable states? How would I know this? Who scheduled what upgrade? What criterion failed construct validation? FML, let’s move on to the next paragraph.
0
2
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2d ago
Replying to
@itisiboller@infosec.exchange ooof, hope you had comfortable shoes
0
0
0
0
Open post
Adrian —dangerously-skip-permissions Sanabria @sawaba@infosec.exchange
· 2mo ago
Replying to
@lcamtuf@infosec.exchange I think I have it too Nothing but regret
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 19:05:37 UTC