Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

lazarusholic

@lazarusholic@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

a big fan of lazarus. You can find me on http://t.me/lazarusholic , https://lazarus.day.

90 Followers
0 Following
50 Posts
Joined November 09, 2022
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Alert to Countries, Companies, and Other Entities Regarding North Korean IT Workers" published by USFBI. #Sanctions, #ITWorker https://www.ic3.gov/CSA/2026/260731.pdf
ic3.gov
1
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"ClickFix, EtherHiding & a DPRK Wallet Trail" published by Allsecure. #ContagiousInterview, #ClickFix, #UNC5342, #EtherHiding https://www.allsecure.io/blog/clickfix-etherhiding-dprk-wallet
ClickFix, EtherHiding & a DPRK Wallet Trail
AllSecure

ClickFix, EtherHiding & a DPRK Wallet Trail

A routine web search led to a macOS malvertising campaign chaining ClickFix social engineering, blockchain-hosted C2 via EtherHiding, a 157-wallet infostealer, and a malicious Chrome extension, with its deployment infrastructure funded by 464.80 ETH withdrawn one way from a KuCoin hot wallet.

1
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Two Joyfill npm Beta Releases Compromised to Deliver DEV#POPPER Remote Access Trojan" published by Socket. #SupplyChain, #NPM, #DevPopper, #OmniStealer https://socket.dev/blog/joyfill-npm-beta-releases-compromised
socket.dev
1
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Inside a DPRK BlueNoroff ClickFix Kit" published by Jumpsec. #Phishing, #Bluenoroff, #NukeSped, #Cloudzy, #Telegram, #ClickFix https://www.jumpsec.com/guides/inside-a-dprk-bluenoroff-clickfix-kit
Inside a DPRK BlueNoroff ClickFix Kit | JUMPSEC
JUMPSEC

Inside a DPRK BlueNoroff ClickFix Kit | JUMPSEC

JUMPSEC researchers analyse an active BlueNoroff phishing kit used to impersonate Zoom and Microsoft Teams meetings, revealing source code, infrastructure, malware delivery and victim targeting techniques.

1
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"ORO Hack Post-Mortem: The Sapphire Sleet Intrusion" published by ORO. #Cryptocurrency, #Phishing, #SapphireSleet, #ORO https://x.com/oroagents/status/2079371018880041257
ORO (@oroagents) on X
X (formerly Twitter)

ORO (@oroagents) on X

ORO Hack Post-Mortem: The Sapphire Sleet Intrusion

1
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 3mo ago
"New Gaslight malware uses prompt injection to evade AI analysis" published by Moonlock. #macOS, #Telegram, #T1082, #T1059006, #T1059004, #T1057, #T1555001, #Gaslight https://moonlock.com/gaslight-malware-evades-ai-analysis
moonlock.com
1
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"2026년 6월 APT 공격 동향 보고서(국내)" published by Ahnlab. #Trend, #LNK https://asec.ahnlab.com/ko/94593
2026년 6월 APT 공격 동향 보고서(국내) - ASEC
ASEC

2026년 6월 APT 공격 동향 보고서(국내) - ASEC

2026년 6월 APT 공격 동향 보고서(국내) ASEC

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"2026 Threat Hunting Report" published by CrowdStrike. #Trend, #StardustChollima, #FamousChollima https://www.crowdstrike.com/en-us/resources/reports/threat-hunting-report
CrowdStrike.com

CrowdStrike 2026 Threat Hunting Report | CrowdStrike

Learn how adversaries weaponize trust across AI, identity, and cloud to accelerate evasive cyber threats. Download the report now.

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 3mo ago

"2026 Mid-year Blockchain Security and AML Report" published by Slowmist. #Trend, #MoneyLaundering, #Lazarus https://slowmist.medium.com/slowmist-2026-mid-year-blockchain-security-and-aml-report-75e0862179ef

slowmist.medium.com
0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"국가배후 해킹조직의 우리 국민·기업 해킹 공격 주의 권고" published by KRCERT. #Phishing, #Wateringhole https://krcert.or.kr/kr/bbs/view.do?bbsId=B0000133&pageIndex=1&nttId=72144&menuNo=205020
보안공지 > 알림마당 :  KISA 보호나라&KrCERT/CC
krcert.or.kr

보안공지 > 알림마당 : KISA 보호나라&KrCERT/CC

보안공지 > 알림마당 : KISA 보호나라&KrCERT/CC

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Weekly Intelligence Report – 10 Jul 2026" published by Cyfirma. #Trend, #SupplyChain, #GitHub, #FamousChollima, #PolinRider https://www.cyfirma.com/news/weekly-intelligence-report-10-jul-2026
Weekly Intelligence Report - 10 Jul 2026 - CYFIRMA
CYFIRMA

Weekly Intelligence Report - 10 Jul 2026 - CYFIRMA

Ransomware In Focus CYFIRMA Research and Advisory Team would like to highlight ransomware trends and insights gathered while monitoring various...

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
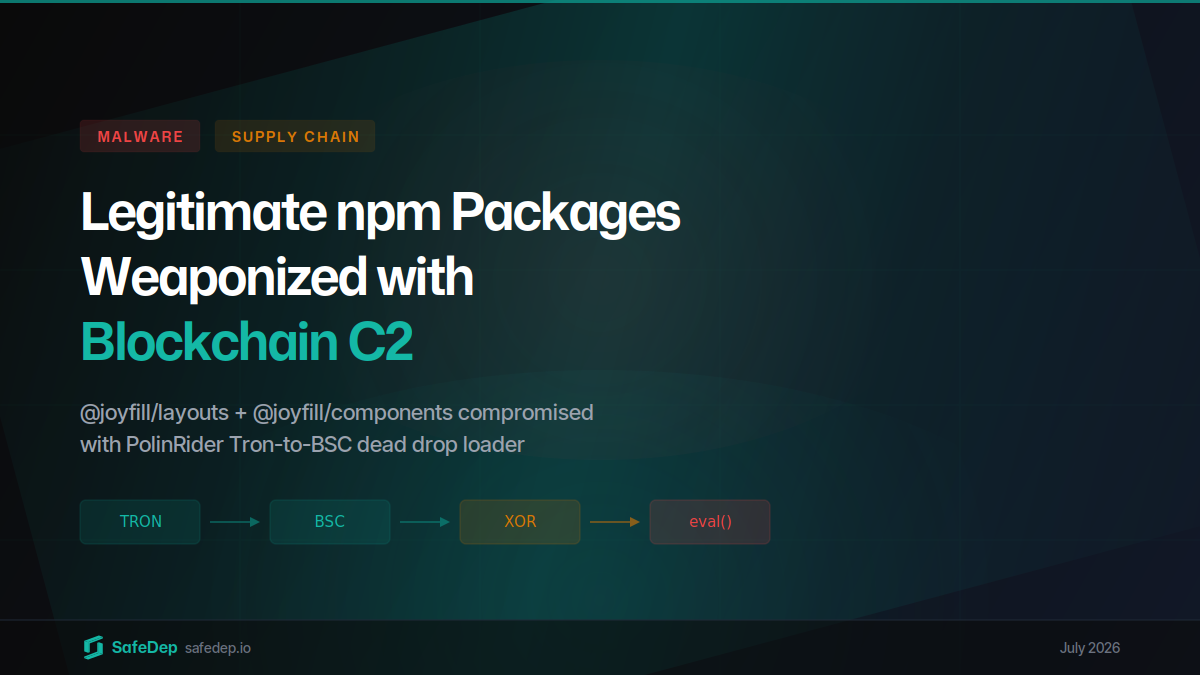
"Joyfill npm Packages Compromised with Blockchain C2 Loader" published by SafeDep. #SupplyChain, #NPM, #PolinRider, #Joyfill https://safedep.io/joyfill-npm-blockchain-c2-supply-chain
Joyfill npm Packages Compromised with Blockchain C2 Loader
SafeDep - Real-time Open Source Software Supply Chain Security

Joyfill npm Packages Compromised with Blockchain C2 Loader

Malicious beta versions of @joyfill/components and @joyfill/layouts published on July 28, 2026 carried the PolinRider blockchain dead drop loader inside their…

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 3mo ago
"PolinRider: North Korea-Linked Supply Chain Campaign Expands Across Open Source Ecosystems" published by Socket. #SupplyChain, #OmniStealer, #PolinRider https://socket.dev/blog/polinrider-north-korea-linked-supply-chain-campaign-expands
socket.dev
0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Grupo Lazarus: Análise Completa dos hackers da Coreia do Norte" published by AscenCripto. #Cryptocurrency, #Lazarus https://ascencriptonewsletter.substack.com/p/grupo-lazarus-analise-completa-dos
🟠Grupo Lazarus: Análise Completa dos hackers da Coreia do Norte
ascencriptonewsletter.substack.com

🟠Grupo Lazarus: Análise Completa dos hackers da Coreia do Norte

Como a Coreia do Norte transformou o roubo de criptoativos em política de Estado: dos assaltos via SWIFT ao recorde de US$ 1,5 bilhão da Bybit

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 3mo ago
"디지털자산 크로스 체인 보안 위협 분석" published by FSI. #Cryptocurrency, #Harmony, #AxieInfinity, #OrbitBridge, #MoneyLaundering, #Lazarus, #KelpDAO https://www.fsec.or.kr/bbs/detail?menuNo=244&bbsNo=11990
fsec.or.kr

금융보안원

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"DPRK’s Famous Chollima Deploys RATs Through ClickFake Job Interviews" published by SOCRadar. #FamousChollima, #ClickFix, #GolangGhost, #PylangGhost https://socradar.io/blog/dprk-clickfake-pylangghost-golangghost-rats/
DPRK’s Famous Chollima Deploys RATs Through ClickFake Job Interviews
SOCRadar® Cyber Intelligence Inc.

DPRK’s Famous Chollima Deploys RATs Through ClickFake Job Interviews

SOCRadar Threat Research Unit analyze the latest ClickFake Interview campaign, a North Korean social engineering operation that targets cryptocurrency...

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 3mo ago

"H1 2026 Crypto Hacks Reach Record High as Losses Fall Below USD 1 Billion" published by Trmlabs. #Cryptocurrency, #DeFi, #DriftProtocol, #KelpDAO https://www.trmlabs.com/resources/blog/h1-2026-crypto-hacks-reach-record-high-as-losses-fall-below-usd-1-billion

trmlabs.com

H1 2026 Crypto Hacks Reach Record High as Losses Fall Below USD 1 Billion  | TRM Labs

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"합동 사이버 보안 권고문 기술 분석 보고서(워터링홀 공격)" published by ENKI. #Wateringhole, #ADS, #Copperhedge https://www.enki.co.kr/media-center/blog/joint-cybersecurity-advisory-watering-hole-malware-analysis
합동 사이버 보안 권고문 기술 분석 보고서(워터링홀 공격)  | 엔키화이트햇
enki.co.kr

합동 사이버 보안 권고문 기술 분석 보고서(워터링홀 공격) | 엔키화이트햇

합동 사이버 보안 권고문 기술 분석 보고서(워터링홀 공격)

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Updated Cyber Threat Actor Naming System" published by Google. #Neptune https://cloud.google.com/blog/topics/threat-intelligence/updated-cyber-threat-actor-naming-system/
Updated Cyber Threat Actor Naming System | Google Cloud Blog
Google Cloud Blog

Updated Cyber Threat Actor Naming System | Google Cloud Blog

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"North Korean IT Workers: How DPRK infiltrates remote hiring" published by Opsek. #Cryptocurrency, #ITWorker https://blog.opsek.io/north-korean-it-workers-remote-hiring/
North Korean IT Workers: How DPRK infiltrates remote hiring
Opsek Blog

North Korean IT Workers: How DPRK infiltrates remote hiring

North Korea's fake IT workers have infiltrated hundreds of companies. How the DPRK scheme works, how big it is and how they are using American facilitators to grow even bigger

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"June 2026 Threat Trend Report on APT Attacks (South Korea)" published by Ahnlab. #Trend, #LNK https://asec.ahnlab.com/en/94594
June 2026 Threat Trend Report on APT Attacks (South Korea) - ASEC
ASEC

June 2026 Threat Trend Report on APT Attacks (South Korea) - ASEC

June 2026 Threat Trend Report on APT Attacks (South Korea) ASEC

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 3w ago
"The DPRK’s Use of Overseas Labour to Violate and Evade UN Sanctions" published by MSMT. #Sanctions, #ITWorker, #MoneyLaundering https://msmt.info/Publications/detail/MSMT%20Report/4232
MSMT App
msmt.info

MSMT App

Multilateral Sanctions Monitoring Team

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 1w ago
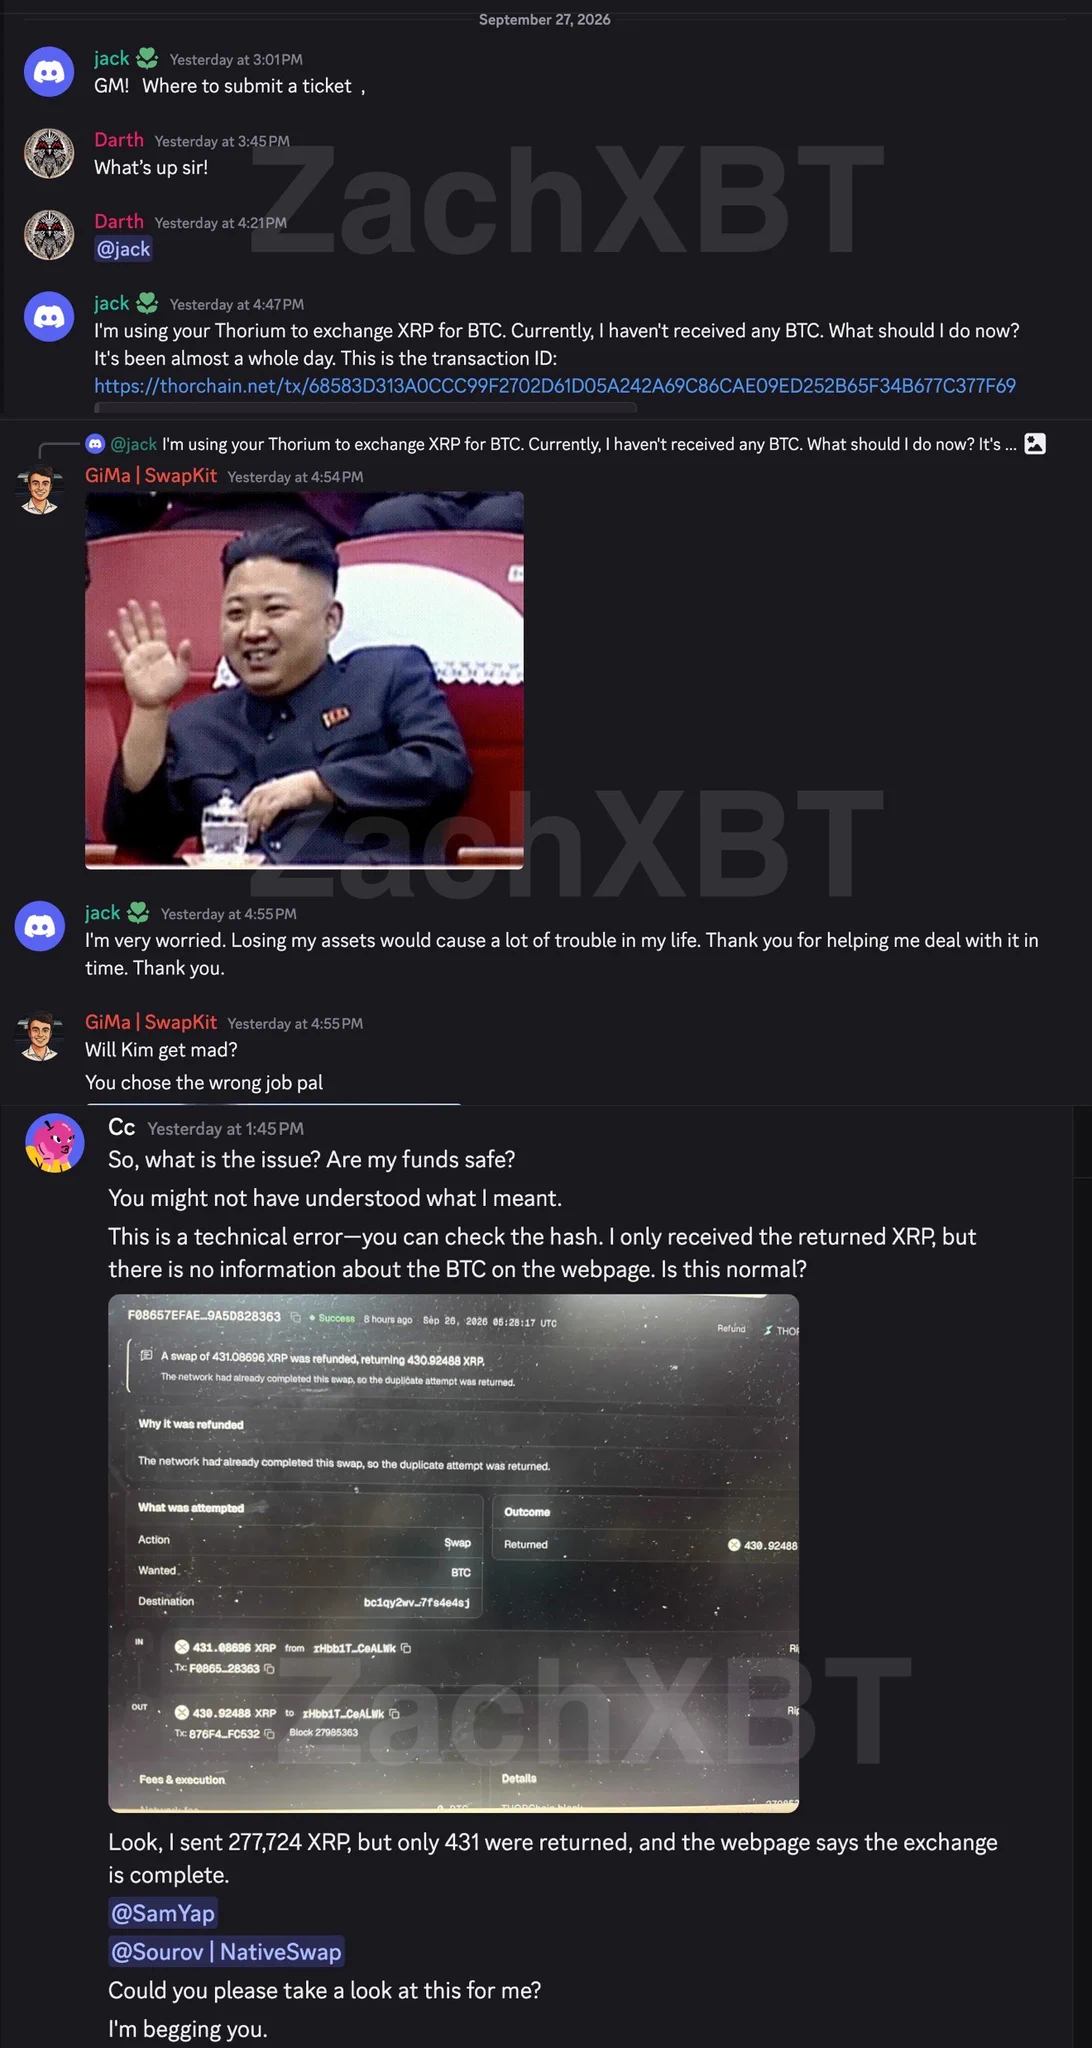
"Chinese illicit actors laundering Bitget exploit funds for alleged DPRK attackers" published by ZachXBT. #MoneyLaundering, #Bitget https://x.com/zachxbt/status/2104528688469647700
ZachXBT (@zachxbt) on X
X (formerly Twitter)

ZachXBT (@zachxbt) on X

BREAKING: Chinese illicit actors laundering funds from the $387M Bitget exploit on behalf of the alleged DPRK attackers are openly asking for support with orders in public Discord servers and Telegram channels of services they use. Notably, Alias 4 (below) was also seen laundering funds from the …

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2w ago
"SEAL weekly stats: Sept. 15-22, 2026" published by SecurityAlliance. #UNC1069, #ContagiousInterview, #SINT01 https://radar.securityalliance.org/seal-weekly-stats-sept-15-22-2026
SEAL weekly stats: Sept. 15-22, 2026
Radar | Security Alliance

SEAL weekly stats: Sept. 15-22, 2026

We dealt with 62 total incidents over the past week. Read more for losses by threat category, what we collected, and IOCs.

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"신종 Gomir Family를 이용한 Kimsuky의 국내 그룹웨어 개발사 공격 분석" published by ENKI. #Kimsuky, #Phishing, #SupplyChain, #Gomir, #HttpTroy https://www.enki.co.kr/media-center/blog/analysis-of-kimsuky-s-attack-on-a-south-korean-groupware-vendor-using-a-new-gomir-family-variant
신종 Gomir Family를 이용한 Kimsuky의 국내 그룹웨어 개발사 공격 분석  | 엔키화이트햇
enki.co.kr

신종 Gomir Family를 이용한 Kimsuky의 국내 그룹웨어 개발사 공격 분석 | 엔키화이트햇

Analysis of Kimsuky's Attack on a South Korean Groupware Vendor Using a New Gomir Family Variant

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Amazon identifies North Korean hacker group behind open-source supply chain attacks" published by Amazon. #SupplyChain, #NPM, #SapphireSleet, #Axios https://aws.amazon.com/blogs/security/amazon-identifies-north-korean-hacker-group-behind-open-source-supply-chain-attacks
Amazon identifies North Korean hacker group behind open-source supply chain attacks | Amazon Web Services
Amazon Web Services

Amazon identifies North Korean hacker group behind open-source supply chain attacks | Amazon Web Services

Amazon is sharing new findings about how a threat actor linked to the Democratic People’s Republic of Korea (DPRK) is targeting open source software libraries, the shared building blocks that companies around the world use to develop applications. Amazon Threat Intelligence has linked several recent compromises of popular Node Package Manager (NPM) libraries to the […]

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Sequel to ChainVeil npm malware: ViteVenom" published by Checkmarx. #SupplyChain, #NPM, #ChainVeil, #ViteVenom, #SuccessKey https://checkmarx.com/zero-post/sequel-to-chainveil-npm-malware-targets-vite-ecosystem/
Sequel to ChainVeil npm malware: ViteVenom - Checkmarx Zero
Checkmarx

Sequel to ChainVeil npm malware: ViteVenom - Checkmarx Zero

npm malware campaign ChainVeil has a sequel targeting the Vite ecosystem. Read about how to identify this ViteVendom variant, defend against it, and find it in your environment.

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"From Payroll to Pyongyang: The DPRK IT Worker Money Trail" published by Dtex. #Sanctions, #ITWorker, #MoneyLaundering https://www.dtex.ai/blog/dprk-it-worker-money-trail
From Payroll to Pyongyang: The DPRK IT Worker Money Trail
DTEX

From Payroll to Pyongyang: The DPRK IT Worker Money Trail

Follow the DPRK IT worker money trail. Our research reveals how payments are processed and funds flow through the regime.

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"DPRK Fake IT Workers: Inside Their Evolving Network Infrastructure" published by KudelskiSecurity. #ITWorker, #OpSec https://kudelskisecurity.com/research/dprk-fake-it-workers-inside-their-evolving-network-infrastructure
kudelskisecurity.com

DPRK Fake IT Workers: Inside Their Evolving Network Infrastructure - Kudelski Security Research Center

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 3mo ago

"PolinRider Jumps the Fence" published by OpenSourceMalware. #SupplyChain, #NPM, #PyPI, #VSCode, #PolinRider https://opensourcemalware.com/blog/polinrider-jumps-the-fence

PolinRider Jumps the Fence to Go, Packagist, npm, PyPI
opensourcemalware.com

PolinRider Jumps the Fence to Go, Packagist, npm, PyPI

DPRK’s most successful campaign spread from GitHub into several package ecosystems without any changes to the malware.

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Kimsuky 그룹의 외교 관련 종사자 사칭 공격 사례 (PebbleDash, PrxClient)" published by Ahnlab. #Kimsuky, #Phishing, #PebbleDash, #LNK, #PrxClient https://asec.ahnlab.com/ko/94553/
Kimsuky 그룹의 외교 관련 종사자 사칭 공격 사례 (PebbleDash, PrxClient) - ASEC
ASEC

Kimsuky 그룹의 외교 관련 종사자 사칭 공격 사례 (PebbleDash, PrxClient) - ASEC

Kimsuky 그룹의 외교 관련 종사자 사칭 공격 사례 (PebbleDash, PrxClient) ASEC

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 3mo ago
"How DPRK’s Contagious Interview Campaign Targets Developers" published by KudelskiSecurity. #Cryptocurrency, #GitHub, #NPM, #ContagiousInterview, #VSCode, #T1041, #T1071001, #T1059007 https://kudelskisecurity.com/research/how-dprks-contagious-interview-campaign-targets-developers
kudelskisecurity.com

How DPRK’s Contagious Interview Campaign Targets Developers - Kudelski Security Research Center

0
0
1
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"North Korea busts elite hacking ring inside its own banks" published by DailyNK. #News https://www.dailynk.com/english/north-korea-elite-bank-hacking-ring-arrested/
North Korea busts elite hacking ring inside its own banks
North Korea News — Daily NK | Latest DPRK Updates 2026

North Korea busts elite hacking ring inside its own banks

North Korea's spy agency arrested a ring of state-trained IT veterans who looted its central bank using cryptocurrency laundering schemes.

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 3mo ago

"북한 배후 조직의 자금세탁 인프라 및 네트워크 분석" published by S2W. #Cryptocurrency, #TraderTraitor, #MoneyLaundering, #Lazarus, #Bybit https://s2w.inc/ko/resource/detail/1090

s2w.inc
0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Operation Double Barrel (The Relationship Between a State-Sponsored Threat Actor and the Gunra Ransomware Group)" published by Ahnlab. #Phishing, #Ransomware, #Wateringhole, #Gunra, #Copperhedge, #DoubleBarrel https://asec.ahnlab.com/en/94696
[Joint Cybersecurity Advisory] Operation Double Barrel (The Relationship Between a State-Sponsored Threat Actor and the Gunra Ransomware Group) - ASEC
ASEC

[Joint Cybersecurity Advisory] Operation Double Barrel (The Relationship Between a State-Sponsored Threat Actor and the Gunra Ransomware Group) - ASEC

[Joint Cybersecurity Advisory] Operation Double Barrel (The Relationship Between a State-Sponsored Threat Actor and the Gunra Ransomware Group) ASEC

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago

"Operation Capsule Vault: RokRAT Attack Chain Analysis Using EMBED_PAYLOAD_v2" published by Genians. #APT37, #RokRAT, #T1566002, #T1055, #CapsuleVault https://www.genians.co.kr/en/blog/threat_intelligence/rokrat_capsule_vault

Operation Capsule Vault: RokRAT Attack Chain Analysis Using EMBED_PAYLOAD_v2
genians.co.kr

Operation Capsule Vault: RokRAT Attack Chain Analysis Using EMBED_PAYLOAD_v2

A targeted spear-phishing campaign was identified using a PIF file disguised as a PDF, embedding a malicious payload to ultimately load RokRAT into memory.

0
0
1
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"국내 그룹웨어 대상 북한 APT 공격 분석" published by ENKI. #Kimsuky, #Phishing, #Slides, #Gomir, #HttpTroy https://github.com/Plainbit/Slides/blob/main/2026%20상반기%20침해사고%20정보공유%20세미나/08-국내%20그룹웨어%20대상%20북한%20APT%20공격%20분석_김영운(엔키).pdf
GitHub

Slides/2026 상반기 침해사고 정보공유 세미나/08-국내 그룹웨어 대상 북한 APT 공격 분석_김영운(엔키).pdf at main · Plainbit/Slides

PLAINBIT 세미나/컨퍼런스 발표자료 목록. Contribute to Plainbit/Slides development by creating an account on GitHub.

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"국내 엔드포인트 대상 공격의 두 축, 스피어피싱과 워터링 홀" published by Ahnlab. #Phishing, #Wateringhole, #Fileless, #Slides https://github.com/Plainbit/Slides/blob/main/2026%20상반기%20침해사고%20정보공유%20세미나/04-국내%20엔드포인트%20대상%20공격의%20두%20축,%20스피어피싱과%20워터링%20홀_이선호(안랩).pdf
GitHub

Slides/2026 상반기 침해사고 정보공유 세미나/04-국내 엔드포인트 대상 공격의 두 축, 스피어피싱과 워터링 홀_이선호(안랩).pdf at main · Plainbit/Slides

PLAINBIT 세미나/컨퍼런스 발표자료 목록. Contribute to Plainbit/Slides development by creating an account on GitHub.

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2w ago
"PolinRider is A/B Testing its Way Past Your Detections" published by OpenSourceMalware. #GitHub, #VSCode, #PolinRider, #NullReceiver https://opensourcemalware.com/blog/polinrider-is-a-b-testing-its-way-past-your-detections
PolinRider is A/B Testing its Way Past Your Detections
opensourcemalware.com

PolinRider is A/B Testing its Way Past Your Detections

fa-solid-400.woff2 became 500 and 900, moved folders, and dropped its whitespace padding. What to look for now.

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Hato Tsusin: A Long-Forgotten DPRK Front Company Hiding in Plain Sight?" published by NKInternet. #OpSec https://nkinternet.com/2026/07/28/hato-tsusin-a-long-forgotten-dprk-front-company-hiding-in-plain-sight
nkinternet.com
0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Compromised npm Packages: @joyfill/components and @joyfill/layouts Ship an Obfuscated Remote Access Trojan" published by StepSecurity. #NPM, #Joyfill https://www.stepsecurity.io/blog/joyfill-npm-supply-chain-compromise
stepsecurity.io

Compromised npm Packages: @joyfill/components and @joyfill/layouts Ship an Obfuscated Remote Access Trojan - StepSecurity

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Detailed Analysis of BirdCall Malware: Masquerading as Zangi Messenger" published by S2W. #Scarcruft, #BirdCall https://s2w.medium.com/detailed-analysis-of-birdcall-malware-marsqurading-as-zangi-messenger-b80db8f5c320
Medium

Detailed Analysis of BirdCall Malware: Masquerading as Zangi Messenger

Author: HyeongJun Kim | S2W TALON

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago

"Operation Capsule Vault: EMBED_PAYLOAD_v2 기반 RokRAT 공격 체인 분석" published by Genians. #APT37, #RokRAT, #T1566002, #T1055, #CapsuleVault https://www.genians.co.kr/blog/threat_intelligence/rokrat_capsule_vault
Operation Capsule Vault: EMBED_PAYLOAD_v2 기반 RokRAT 공격 체인 분석
genians.co.kr

Operation Capsule Vault: EMBED_PAYLOAD_v2 기반 RokRAT 공격 체인 분석

정상 PDF로 위장한 PIF 파일에 악성 페이로드를 함께 내장해, 최종적으로 RokRAT을 메모리에 적재하는 다단계 표적형 스피어피싱 공격이 포착되었습니다.

0
0
1
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Batten Down Your Packages: Mitigation Guidance for Supply Chain Compromise" published by Google. #SupplyChain, #UNC1069, #Axios, #T1195002, #T1195001, #MidnightNeptune https://cloud.google.com/blog/topics/threat-intelligence/mitigation-guidance-for-supply-chain-compromise
Mitigation Guidance for Supply Chain Compromise | Google Cloud Blog
Google Cloud Blog

Mitigation Guidance for Supply Chain Compromise | Google Cloud Blog

Trends we have observed in threat actor use of software supply chain compromise, and provide mitigation and hardening recommendations.

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"게임 업계 대상 MoonPeak 감염 사례 분석" published by Hauri. #LNK, #XenoRAT, #MoonPeak https://hauri.co.kr/security/security_view.html?intSeq=90
hauri.co.kr

(주)하우리

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"ChainVeil and ViteVenom are DPRK’s PolinRider Campaign" published by OpenSourceMalware. #SupplyChain, #NPM, #PolinRider, #ChainVeil, #ViteVenom https://opensourcemalware.com/blog/chainveil-and-vitevenom-dprk-polinrider-campaign
ChainVeil and ViteVenom are DPRK’s PolinRider Campaign
opensourcemalware.com

ChainVeil and ViteVenom are DPRK’s PolinRider Campaign

Shared infrastructure is the smoking gun connecting the pieces.

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 3mo ago
"nodemon-sudo: an npm Backdoor With No Install Script" published by SafeDep. #SupplyChain, #NPM https://safedep.io/malicious-nodemon-sudo-tslint-conf-npm-backdoor/
nodemon-sudo: an npm Backdoor With No Install Script
SafeDep - Real-time Open Source Software Supply Chain Security

nodemon-sudo: an npm Backdoor With No Install Script

nodemon-sudo copies the real nodemon byte for byte, adds nothing malicious to its own code, and injects one extra dependency, tslint-conf, a repackaged pino…

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"Attack Cases by the Kimsuky Group Impersonating Diplomats (PebbleDash, PrxClient)" published by Ahnlab. #Kimsuky, #Phishing, #PebbleDash, #LNK, #PrxClient https://asec.ahnlab.com/en/94552/
Attack Cases by the Kimsuky Group Impersonating Diplomats (PebbleDash, PrxClient) - ASEC
ASEC

Attack Cases by the Kimsuky Group Impersonating Diplomats (PebbleDash, PrxClient) - ASEC

Attack Cases by the Kimsuky Group Impersonating Diplomats (PebbleDash, PrxClient) ASEC

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"A Detailed Post-Mortem on the AFX Security Incident" published by AFXTrade. #DeFi, #UNC4899, #AFX https://medium.com/@AFXTrade/a-detailed-post-mortem-on-the-afx-security-incident-57d564ef812f
A Detailed Post-Mortem on the AFX Security Incident
Medium

A Detailed Post-Mortem on the AFX Security Incident

Introduction

0
0
0
0
Open post
lazarusholic @lazarusholic@infosec.exchange
· 2mo ago
"New North Korean campaign uses fake coding interviews to steal developer credentials" published by Elastic. #BeaverTail, #OtterCookie, #REF9403 https://www.elastic.co/security-labs/contagious-interview-malware-svg-steganography
Contagious Interview malware in SVG images: DPRK campaign
elastic.co

Contagious Interview malware in SVG images: DPRK campaign

Contagious Interview malware uses SVG steganography to hide payloads in a developer coding challenge. No antivirus vendor detected it.

0
0
1
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 05:02:32 UTC