Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Censys

@censys@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Censys is the authority in Internet intelligence and insights. Delivering the most comprehensive, accurate, and up-to-date global map of Internet infrastructure, Censys provides the real-time external visibility organizations need to accelerate security operations, investigate threats, and understand Internet exposure. Global governments, Fortune 500 companies, and security providers trust Censys to uncover risks faster and respond more effectively.

315 Followers
24 Following
35 Posts
Joined November 14, 2022
Website:
https://censys.com/
Censys Platform:
https://censys.com/platform/
Censys Search:
https://censys.com/product/censys-enterprise/
Censys Attack Surface Management:
https://censys.com/product/attack-surface-management/
Censys Adversary Investigation:
https://censys.com/product/adversary-investigation/
Censys Critical Infrastructure Monitoring:
https://censys.com/product/critical-infrastructure/
Open post
Censys @censys@infosec.exchange
· 3w ago
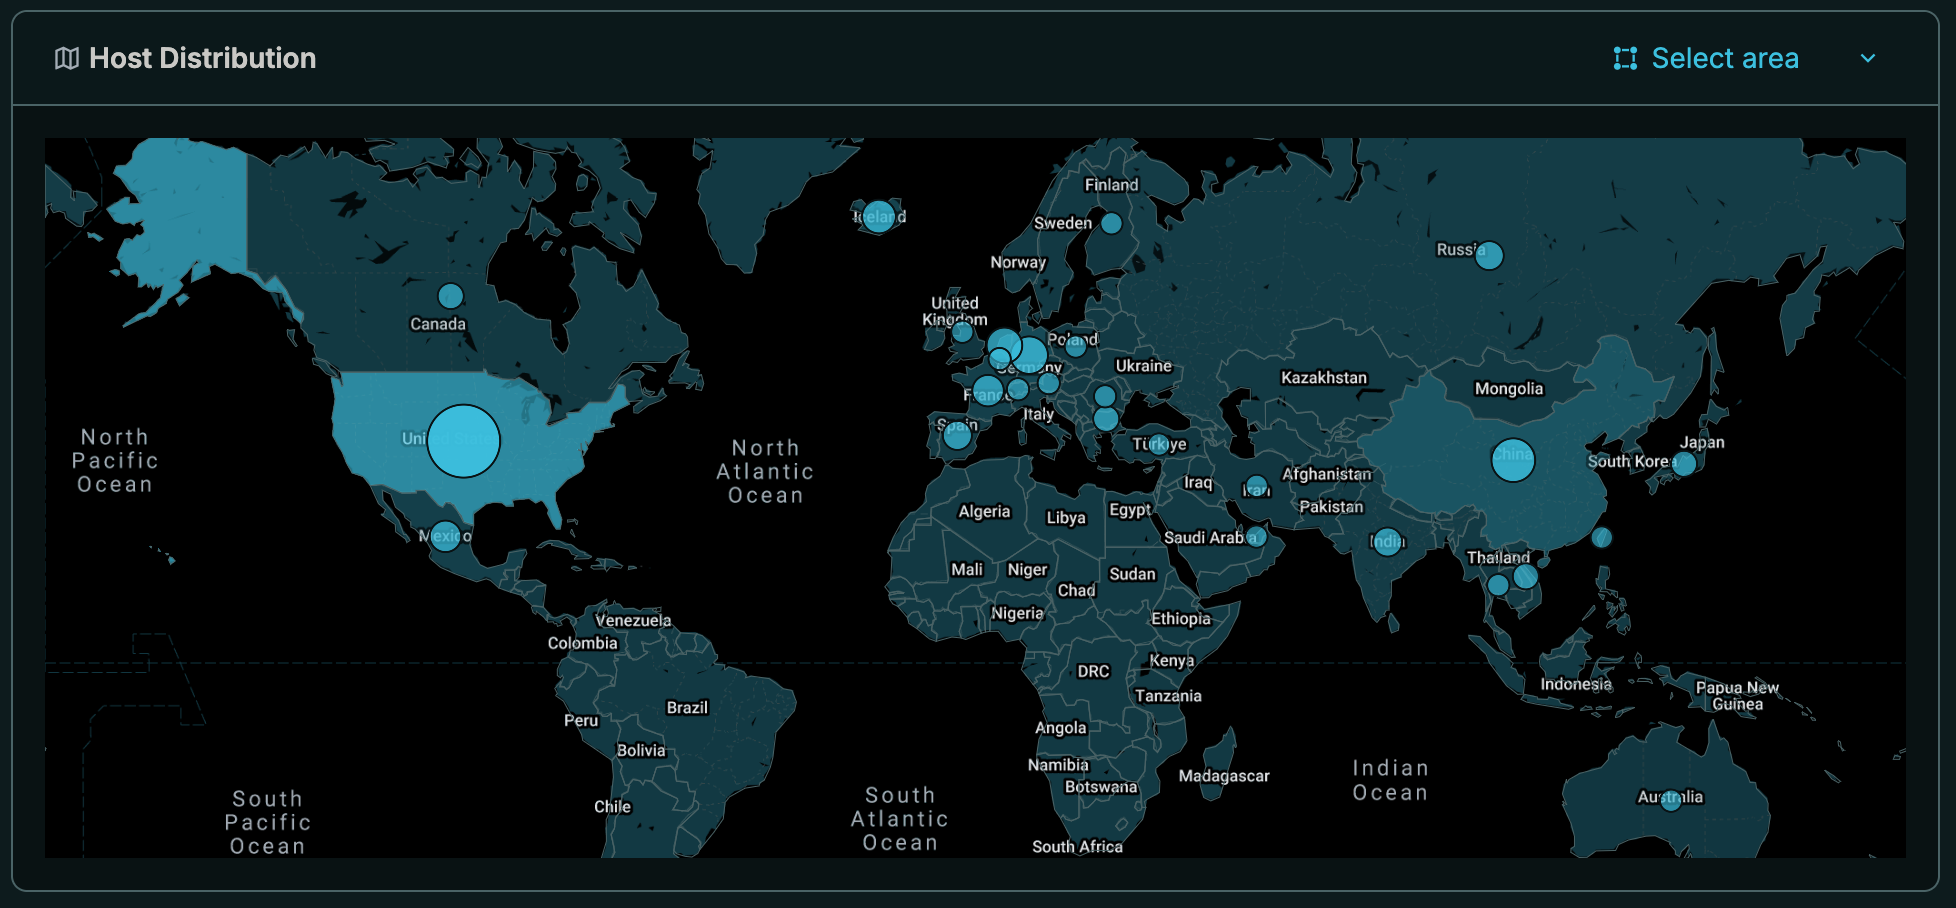
What does Mythic C2 look like across the public Internet? Censys ARC sees 131 Mythic-associated hosts, and many leave recognizable fingerprints. The infrastructure also tells a deeper story. One cluster appeared consistent with a shared lab environment. Another revealed custom Rust implants, Discord-based C2 transport, steganographic staging, and infrastructure designed to blend with legitimate telemetry traffic. This new Censys Threat Overview maps Mythic across the Internet and shares detection signals defenders can use to hunt for it: https://censys.com/blog/mythic-c2/#ThreatIntelligence #ThreatHunting #C2 #CensysARC
Mythic C2 Activity at Internet Scale - Censys
Censys

Mythic C2 Activity at Internet Scale - Censys

Censys tracks 131 hosts exposing Mythic to the public Internet. Learn about the C2 framework and how to defend against it.

3
0
3
0
Open post
Censys @censys@infosec.exchange
· 3w ago
The recent MikroTik RouterOS vulnerabilities have several conditions for exploitation. That may make mass exploitation more difficult, but targeted attacks are another story. @martijn_grooten@mastodon.social and @silas@infosec.exchange break down what an attacker needs. https://censys.com/podcasts-videos/censys-arc-flash-episode-5/#CensysARC #MikroTik #ThreatIntelligence #ThreatResearch #InfoSec #Cybersecurity
Censys ARC Flash Episode 5: MicroTik, NPS, and Camera Exposures - Censys
Censys

Censys ARC Flash Episode 5: MicroTik, NPS, and Camera Exposures - Censys

Silas Cutler and Martijn Grooten discuss new MikroTik RouterOS vulnerabilities, detecting malicious NPS activity, and exposed camera hacking.

1
0
1
0
Open post
Censys @censys@infosec.exchange
· 2mo ago
In Episode 3 of Censys ARC Flash, @thehappydinoa@infosec.exchange and Silas Cutler discuss Censys ARC research into nearly 40 AsyncRAT variants, how malware families evolve, and why defenders should care. If you missed the live webcast, the full recording is now available on demand: https://censys.com/podcasts-videos/censys-arc-flash-episode-3/ #CensysARC #Cybersecurity #ThreatIntelligence #Malware
Censys ARC Flash Episode 3: AsyncRAT and FortiBleed - Censys
Censys

Censys ARC Flash Episode 3: AsyncRAT and FortiBleed - Censys

In Episode 3 of Censys ARC Flash, Principal Security Researcher Silas Cutler and Senior Security Researcher Aidan Holland discuss recent research into AsyncRAT malware variants, emerging findings around the FortiBleed campaign targeting FortiGate devices, and what defenders should know about modern malware ecosystems. Silas: Hi my name is Silas Cutler. I’m a principal researcher here […]

1
0
0
0
Open post
Censys @censys@infosec.exchange
· 3mo ago
Replying to
Security teams have plenty of internal telemetry. What's often missing is external context. With integrated DNS, analysts can pivot across domains, IPs, hosts, certificates, services, and DNS history to quickly understand how infrastructure is connected.
1
1
0
0
Open post
Censys @censys@infosec.exchange
· 3mo ago
Replying to
Whether you're trying to: ✓ Triage alerts ✓ Investigate incidents ✓ Hunt adversaries ✓ Defend against emerging campaigns DNS is now another layer of the Censys Internet Map helping teams decide faster and more accurately across every stage of the security operations workflow: https://censys.com/blog/censys-expands-its-internet-map-to-include-dns-intelligence/#Censys #infosec #ThreatIntel #DNS
censys.com
1
0
0
0
Open post
Censys @censys@infosec.exchange
· 17mo ago

👀 It has been quite a wild week in the land of CVEs. Get the Censys research team perspective in our latest blog, "Now You CVE, Now You Don't: How the MITRE CVE Program Nearly Went Dark". https://censys.com/blog/now-you-cve-now-you-dont-how-the-cve-program-nearly-went-dark

censys.com
6
0
1
0
Open post
Censys @censys@infosec.exchange
· 17mo ago

The botnets 👾 out there; you just have to know how to grab them. We know how to grab them. Together with @greynoise@infosec.exchange, we've brought threat hunting to the next level. https://censys.com/blog/hunting-botnets-with-cursorai-greynoise-censys-and-censeye

censys.com
4
0
5
0
Open post
Censys @censys@infosec.exchange
· 15mo ago

Around 12PM UTC on June 18, scan error rates in Iran surged to nearly 100%, indicating a sudden, nationwide outage affecting almost all services. Systems that were previously reachable are now timing out or rejecting connections.

3
0
6
0
Open post
Censys @censys@infosec.exchange
· 16mo ago

We used the new Censys Threat Hunting Module to investigate a Colombian threat actor, uncovering a series of remote access trojan (RAT) C2 servers.

We also show how to use this information to create a set of IOCs for defensive measures:

https://censys.com/blog/unmasking-the-infrastructure-of-a-spearphishing-campaign

censys.com
3
0
2
0
Open post
Censys @censys@infosec.exchange
· 15mo ago

🔌 Iran Internet Outage Update
Since June 18, Iran has faced a near-total internet blackout. June 21 marked the lowest point in visibility—but signs of recovery are emerging.

📉 Some networks (e.g., DATAK, HAMYAR-AS) remain unstable.
📈 Others (e.g., RESPINA-AS, MOBINNET-AS) are bouncing back strong.
🧭 TIC appears in nearly all slow-recovering transit paths.

We’re tracking it all.
🔍 View the update at Censys: https://censys.com/blog/irans-internet-a-censys-perspective

#InternetShutdown #Iran #NetworkOutage #Censys #InternetIntelligence

censys.com
2
0
5
0
Open post
Censys @censys@infosec.exchange
· 16mo ago

In October 2024, Censys researchers discovered ~400 U.S. water facility web-based HMIs exposed online. Within a month of sharing data with the EPA and the vendor, 58% of systems were protected. Read more here:

https://censys.com/blog/turning-off-the-information-flow-working-with-the-epa-to-secure-hundreds-of-exposed-water-hmis

#ics #security #water

censys.com
2
0
3
0
Open post
Censys @censys@infosec.exchange
· 17mo ago

May 6 Advisory: Critical RCE Vulnerability Identified in Craft CMS [CVE-2025-32432] https://censys.com/advisory/cve-2025-32432

censys.com
2
0
1
0
Open post
Censys @censys@infosec.exchange
· 15mo ago

Multiple US gov agencies have warned orgs to stay vigilant for potential Iran-affiliated cyber activity. We studied exposure of 4 vendors previously known to be of interest to IR-affiliated groups.

Read more: https://censys.com/blog/ics-iran-exposure-of-previously-targeted-devices

#infosec #security

censys.com
1
0
1
0
Open post
Censys @censys@infosec.exchange
· 16mo ago

A defining moment for Censys - We are excited to announce that the Threat Hunting Module in the new Censys Platform is now #ga

https://www.censys.com/blog/internet-scale-proactive-threat-hunting-and-detection

infosec.exchange
1
0
1
0
Open post
Censys @censys@infosec.exchange
· 16mo ago

Trend Micro recently uncovered a campaign leveraging TikTok to distribute malware via AI-generated videos, tricking users into installing Vidar and StealC infostealers instead of the promised pirated software.

Using IOCs provided by Trend Micro, we used Censys to find more related infrastructure, including a relatively new bulletproof service provider. Read our analysis here:

https://censys.com/blog/tiktok-and-malware

#infosec #security #malware #tiktok

TikTok and Malware - Censys
Censys

TikTok and Malware - Censys

Uncovering hidden IOCs behind TikTok malware campaigns using AI-generated videos. Deep dive into Vidar & StealC info-stealers, malicious domains & PowerShell scripts.

1
0
5
0
Open post
Censys @censys@infosec.exchange
· 17mo ago

If you think Salt Typhoon has moved on—you might want to double-check your attack surface. We’re still seeing critical telecom infrastructure exposed to active targeting. Find out what we uncovered (and what you should be looking for) https://censys.com/blog/salt-typhoon-attacks-highlight-need-for-advanced-defenses

censys.com
1
0
0
0
Open post
Censys @censys@infosec.exchange
· 17mo ago

🚨 Launch Alert 🚨Censys just redefined threat hunting. Our new Threat Hunting Module delivers unmatched visibility and context from real-time Internet Intelligence that empowers you to proactively hunt emerging threats. See it in action: https://censys.com/solutions/threat-hunting #cybersecurity #threathunting

censys.com
1
0
2
0
Open post
Censys @censys@infosec.exchange
· 3mo ago
Replying to
Every Censys ARC Flash is built around what our researchers are seeing across the Internet. If you're interested in threat research, Internet intelligence, and understanding how campaigns evolve, we'd love to have you join us live. https://info.censys.com/arc-webcast #CensysARC #Cybersecurity #ThreatIntelligence #InfoSec
info.censys.com

Censys ARC Webcast Series

0
0
0
0
Open post
Censys @censys@infosec.exchange
· 3mo ago
Replying to
The research uncovered more than straightforward phishing. It also mapped "offerwall" sites that promise free in-game currency in exchange for surveys, app installs, and other tasks that collect children's data. One TLS certificate even led to a gambling brand tied to this ecosystem.
0
1
0
0
Open post
Censys @censys@infosec.exchange
· 3mo ago
Replying to
All of this was measured using Censys Internet intelligence to help defenders better understand an ecosystem that isn't well covered by traditional threat intelligence. Read Alex Gartner's full research: https://censys.com/blog/roblox-minecraft-and-the-insidious-internet-for-children/#InternetIntelligence #ThreatResearch #InfoSec #OSINT
Roblox, Minecraft, and the Insidious Internet for Children - Censys
Censys

Roblox, Minecraft, and the Insidious Internet for Children - Censys

An exploration of Roblox and Minecraft offerwalls and phishing lures — infrastructure that isn’t well covered by conventional threat intelligence.

0
0
0
0
Open post
Censys @censys@infosec.exchange
· 15mo ago

🔍 We looked at the C2 server associated with the Flodrix botnet and used an internet-exposed RPC service to uncover a world-readable NFS mount and 745 compromised hosts!

👀 https://censys.com/blog/poking-the-flodrix-botnet

#botnet #infosec

censys.com
0
0
2
0
Open post
Censys @censys@infosec.exchange
· 16mo ago

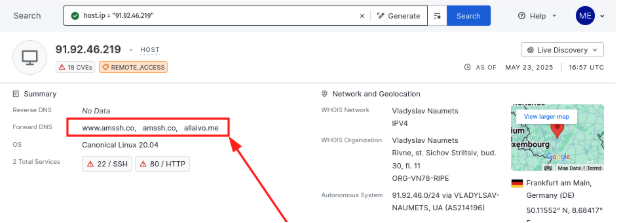
Thousands of compromised ASUS routers are being co-opted into a volatile but persistent botnet. Our latest blog takes IoCs from @greynoise@infosec.exchange and breaks down how the AyySSHush campaign has evolved over the past 5 months — and what makes it stand out:

https://censys.com/blog/tracking-ayysshush-a-newly-discovered-asus-router-botnet-campaign

#botnet #asus #infosec #security

censys.com
0
0
1
0
Open post
Censys @censys@infosec.exchange
· 17mo ago

🚩 May 7 Advisory: Unauthenticated Code Injection Vulnerability in Langflow [CVE-2025-3248] https://censys.com/advisory/cve-2025-3248

censys.com
0
0
0
0
Open post
Censys @censys@infosec.exchange
· 17mo ago

Censys was a proud contributor to the 2025 Verizon Data Breach Investigations Report, shedding light on the growing threat to firewalls, VPNs, and other perimeter gear. See that this sharp increase in targeting edge security devices means ➡️ https://censys.com/blog/postcards-from-the-edge-verizon-dbir-reveals-sharp-increase-in-targeting-of-edge-security-devices

censys.com
0
0
0
0
Open post
Censys @censys@infosec.exchange
· 17mo ago

Security advisory update for this week. April 28 Advisory: SAP NetWeaver Actively Exploited Unauthenticated File Upload Vuln [CVE-2025-31324]
This is an especially severe issue that combines several of the worst-case risk factors. Read more: https://censys.com/advisory/cve-2025-31324

censys.com
0
0
0
0
Open post
Censys @censys@infosec.exchange
· 17mo ago

Threat hunters, this is your inside track. 🎥 We just dropped an exclusive threat intelligence briefing from malware analyst Silas Cutler. Get insight into the BeaverTail malware campaign, North Korea’s infiltration of global tech, and more. Watch now. https://censys.com/podcasts-videos/inside-north-korea-cyber-ops-with-silas-cutler

censys.com
0
0
0
0
Open post
Censys @censys@infosec.exchange
· 17mo ago

CISA's SCuBA reminds us: strong government cloud security starts with strong fundamentals. 🔐 Censys' lead federal solutions engineer calls for a return to basics in a brand new Federal News Network article.
https://federalnewsnetwork.com/commentary/2025/04/securing-federal-cloud-environments-cisa-scuba-reminds-cloud-service-providers-of-the-basics/

federalnewsnetwork.com
0
0
0
0
Open post
Censys @censys@infosec.exchange
· 2mo ago

Every year, Censys scans the Internet and publishes what we find. This year's State of the Internet Report is almost here.

0
1
0
0
Open post
Censys @censys@infosec.exchange
· 2mo ago

Following a joint advisory from Dutch intelligence services, Censys ARC Principal Security Researcher Martijn Grooten examined Internet-connected camera exposure across Europe.

Censys observed more than 87,000 Internet-connected cameras with potentially exploitable vulnerabilities across Europe and Ukraine.

0
1
0
0
Open post
Censys @censys@infosec.exchange
· 3mo ago

Sometimes sensitive data is just sitting on the public Internet. An exposed database, an unauthenticated message broker, or a forgotten file transfer server, all accessible to anyone who finds it.

0
1
0
0
Open post
Censys @censys@infosec.exchange
· 3mo ago

In this clip from the Censys ARC Flash, Silas Cutler and Michael Schwartz discuss what we're seeing across the Internet and why it matters.

0
1
0
0
Open post
Censys @censys@infosec.exchange
· 3mo ago

Detection Engineering has evolved beyond the SIEM, into a broader SecOps discipline.

Detections increasingly have to start before endpoint execution: in identity, DNS, proxy, cloud, SaaS, exposed infrastructure, and the public Internet itself.

0
1
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 17:49:04 UTC