#rat
53 posts · Last used 11d
Boosted by @Dragofix@veganism.social
This diminutive and cute tree #rat 🩷🐀🌳has a difficult name: D’Entrecasteaux Archipelago Pogonomys. They’re #endangered in #PapuaNewGuinea due to #palmoil and #timber #deforestation. Help them survive and #BoycottPalmOil #Boycott4Wildlife @palmoildetectives@mastodonapp.uk https://palmoildetectives.com/2021/01/31/dentrecasteaux-archipelago-pogonomys-pogonomys-fergussoniensis/?utm_source=mastodon&utm_medium=Palm+Oil+Detectives&utm_campaign=publer
Boosted by @trending@homestead.social
Rat racer on a boulangerie run.
A collaboration with @fpiatti@mastodon.art who built & painted the car (and took these photos!) 💛
Tried a bunch of new things in terms of materials for this one! Really happy with how it turned out 😊
#MastoArt #sculpture #ModelCar #Racing #Rat
Chinese-Speaking Operator Uses AI Agents to Target Government and Education Systems Across Asia
Pulse ID: 6a9f95581dc4c6de1b0540b2
Pulse Link: https://otx.alienvault.com/pulse/6a9f95581dc4c6de1b0540b2
Pulse Author: Tr1sa111
Created: 2026-09-08 04:55:52
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#Asia #Chinese #CyberSecurity #Education #Government #InfoSec #OTX #OpenThreatExchange #RAT #bot #Tr1sa111
A distributed npm supply chain attack dropped a cross-platform RAT on Alibaba developers. Socket found malicious npm packages hiding loader code.
#npm #SupplyChainAttack #RAT #Alibaba #Malware #CyberSecurity
https://securityonline.info/npm-supply-chain-attack-alibaba-rat/?utm_source=mastodon&utm_medium=jetpack_social
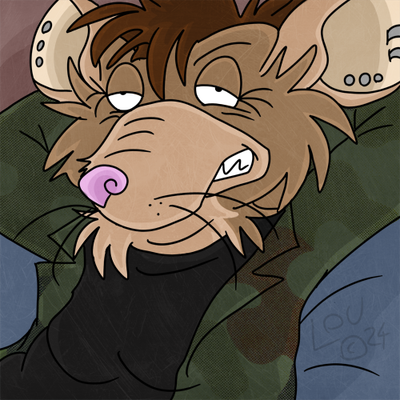
Lucia now in Dress :3
She will be my goth-Girl
slowly making her a full fledged OC >:D
#Ink #furry #furryart #furryartist #traditionalart #rat #fediart #gothic #goth
Currently decompiling LabubaRAT with Ghidra. It's taking ages to perform the initial analyzing, probably because of Rust.
https://blackpointcyber.com/blog/labubarat-a-rust-based-remote-access-tool-masquerading-as-nvidia-software/
#malware #rust #RAT #labubaRAT
🤖 "Flying Eagle": Premium mobile RAT builder-as-a-service targets Android users across China. Multiple threat groups use the MaaS platform to build infostealers that drain accounts via SMS interception and overlay attacks.
🔗 https://www.darkreading.com/endpoint-security/flying-eagle-mobile-rat-builder-china
#Malware #RAT #MobileSec #CyberSec
A Lampion malware campaign is hitting Portugal. The Portugal phishing campaign uses fake SAPO transfer pages to drop a multistage VBS infection chain.
#Lampion #Phishing #Portugal #Malware #RAT
http://securityonline.info/lampion-malware-campaign-portugal/?utm_source=mastodon&utm_medium=jetpack_social
Proofpoint details the Cruciferra crypter service that cloaks RATs and infostealers using BYOVD EDR tampering and 90+ custom encryption routines.
#Cruciferra #Crypter #MaaS #BYOVD #ProcessGhosting #Infostealer #RAT #Proofpoint
https://securityonline.info/cruciferra-crypter-service/?utm_source=mastodon&utm_medium=jetpack_social
Artfight on Mikmik
#artfight #artfight2026 #rat #furry #furryart #rodent #artfightattack #fullbody #digitalArt
flavor rats... rats foley? last minute sticker sheet design before the con next week!
#rat #rats #ratsOfMastodon #rodents #vocaloid #flavorFoley #vocaloidArt #fanArt #cute
🤖 New "Dolphin X" RAT uses AI-powered profiling to rank infected victims by value, helping attackers prioritize high-value targets. Includes keylogging, credential theft, and remote access features.
🔗 https://www.bleepingcomputer.com/news/security/new-dolphin-x-malware-uses-ai-to-rank-high-value-targets/
#Malware #AI #CyberSec #RAT
🤖 Fake Claude desktop app promoted via Bing ads pushes SectopRAT malware. The installer, hosted on a legitimate Claude.ai domain, delivers a remote access trojan that steals credentials and data.
🔗 https://www.bleepingcomputer.com/news/security/fake-claude-app-promoted-by-bing-ads-pushes-sectoprat-malware/
#Malware #RAT #CyberSec #Malvertising #SectopRAT
🤖 New Dolphin X RAT uses AI-powered profiling to rank infected victims by value. The malware scores user activity to help attackers prioritize which targets to compromise first.
🔗 https://www.bleepingcomputer.com/news/security/new-dolphin-x-malware-uses-ai-to-rank-high-value-targets/
#Malware #AI #CyberSec #RAT
Oh it's just me.
#furry #furryart #fursona #rat #mastoart #myart #creativetoots #smallartist #artist
artfight attack for GhostPrince, i turned his boy into a rat 🐀🐀🐀🐀🐀🐀🐀
#rat #rats #ratsOfMastodon #rodents #artFight #teamMystery #pokemon #pokemonArt #cute #cuteArt
LabubaRAT is a Rust-based remote access tool disguised as NVIDIA software. It supports HTTPS, WebView2, and DNS tunneling for command and control.
#LabubaRAT #Malware #Rust #RAT #ThreatIntel
https://securityonline.info/labubarat/?utm_source=mastodon&utm_medium=jetpack_social
Contagious Interview malware in SVG images: DPRK campaign
A DPRK-aligned threat group is targeting developers through fake job postings and coding challenges in a campaign tracked as REF9403. Attackers post fake job offers in developer forums, then send trojanized repositories containing fully functional e-commerce projects with malicious code hidden using steganography inside SVG flag images. When developers run these projects, the malware deploys four-stage payloads aligned with OTTERCOOKIE: a browser credential and cryptocurrency wallet stealer, a file exfiltration module, a Socket.IO-based remote access trojan, and a clipboard stealer. The campaign was discovered after targeting Elastic's community Slack workspace. Multiple trojanized repositories were found with zero antivirus detections at the time of discovery, demonstrating the sophistication of this supply chain attack vector against software developers.
Pulse ID: 6a5a8ba0229db5a5b2686baa
Pulse Link: https://otx.alienvault.com/pulse/6a5a8ba0229db5a5b2686baa
Pulse Author: AlienVault
Created: 2026-07-17 20:08:00
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#Browser #Clipboard #CyberSecurity #DPRK #InfoSec #Malware #OTX #OpenThreatExchange #RAT #RCE #RemoteAccessTrojan #SVG #Steganography #SupplyChain #Trojan #bot #cryptocurrency #developers #AlienVault
GigaWiper: wiper, stealer, ransomware w jednym. Szczegółowa analiza malware
Badacze bezpieczeństwa z Microsoft Threat Intelligence przeprowadzili analizę zaawansowanej kampanii, w której cyberprzestępcy wykorzystali rodzinę złośliwego oprogramowania o nazwie GigaWiper. Jak sama nazwa wskazuje, malware należy do kategorii wiperów, których głównym zadaniem jest bezpowrotne niszczenie danych na zainfekowanej maszynie. Działania te są realizowane poprzez usuwanie metadanych partycji dysków, szyfrowanie danych...
#Aktualności #Malware #Microsoft #Ransomware #RAT #Stealer #Wiper
https://sekurak.pl/gigawiper-wiper-stealer-ransomware-w-jednym-szczegolowa-analiza-malware/